

The ACSC Essential 8 is a critical cybersecurity framework for Australian businesses. It's a practical, prioritised list of security strategies from the Australian Cyber Security Centre (ACSC), designed to provide maximum defence against common cyber threats. This guide will break down the Essential 8 mitigation strategies, their maturity levels, and how they help protect your organisation from the modern Australian cyber threat landscape.
Think of it as the foundational set of controls for protecting your business online. It’s not just an exhaustive, tick-a-box compliance exercise; it’s a focused strategy to block the most prevalent ways that attackers compromise systems.
Decoding the ACSC Essential 8
The term ‘cybersecurity framework’ can sound intimidating. But imagine you’re securing your physical office. You’d start with strong locks, an alarm system, and perhaps some security cameras, right? The ACSC Essential 8 is the digital equivalent of that – a set of foundational security controls that protect your business from the most frequent and disruptive cyber attacks we see hitting Australian businesses every single day.
This is about much more than just keeping the tech team busy. It’s about building a business that your customers can trust. When you implement these controls, you're not just preventing problems; you're demonstrating that you take the security of their data seriously. That kind of trust is a powerful competitive advantage, turning cybersecurity from a cost centre into a genuine asset for your brand.
The Role of Maturity Levels
So, where do you start? The ACSC knows that a one-size-fits-all approach doesn't work. That's why they created Maturity Levels – a straightforward roadmap that lets any business build a solid defence, no matter its size or budget. It breaks the journey down into manageable steps.
These levels create a clear path forward, so you can improve your security posture over time.
- Maturity Level One: This is your baseline. It’s designed to protect you from opportunistic attackers who use widely available tools. For most small and medium-sized businesses, this is the perfect place to start.
- Maturity Level Two: Here, you’re stepping up your game. This level defends against more focused adversaries who have greater skill and are more deliberate in choosing their targets.
- Maturity Level Three: This is the highest level of protection. It’s built for organisations that are likely to be targeted by sophisticated, well-resourced attackers, including state-sponsored groups.
This tiered approach means you can methodically strengthen your defences as your business grows or as the threats you face evolve. It’s a journey, not a one-off task. You align your security investment with your real-world risks, ensuring you're not just protected today but also prepared for whatever comes next. This helps build a true security-first mindset, which you can explore further on the Australian Cyber Security Centre website.
The Eight Core Strategies That Protect Your Business
Let's move from theory to practical defence. The ACSC Essential 8 is built on eight specific, high-impact mitigation strategies. Think of them less as technical recommendations and more as the core defensive manoeuvres that shut down the most common attacks we see hitting Australian businesses every day. Each strategy is a layer of protection, and when you combine them, they form a truly formidable shield around your digital assets.
This image gives you a great visual overview of how the Essential 8 creates a multi-layered security posture, all centred on defence, resilience, and building trust.
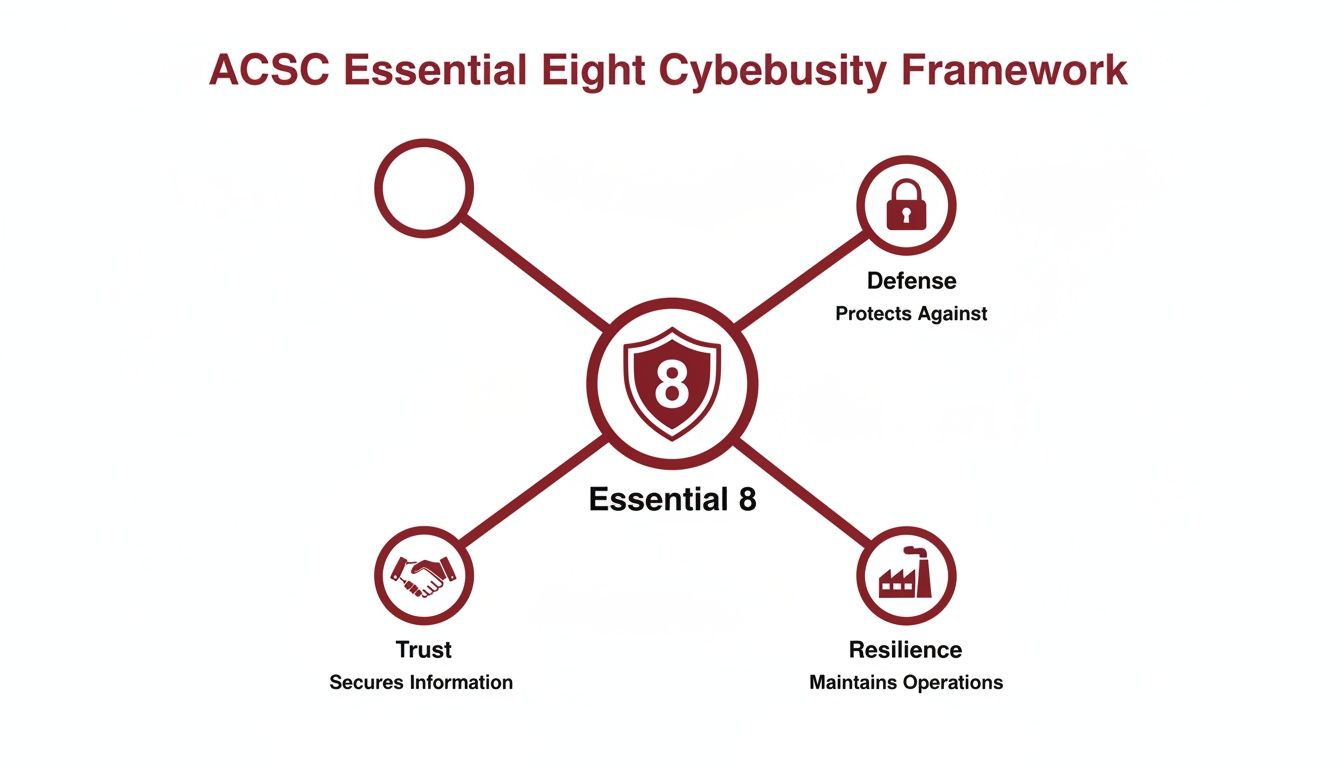
As you can see, these strategies don't just work in isolation. They team up to defend against immediate threats while also making sure your business can bounce back quickly from an incident, which is crucial for maintaining the trust of your clients and partners.
Let’s break down each of these eight core strategies.
How the Essential 8 Strategies Defend Your Business
To really grasp their power, it helps to see exactly what each control does and why it matters. The table below summarises how each strategy stops a specific threat and the direct, practical benefit that brings to your business.
| Mitigation Strategy | Threat Mitigated | Primary Business Benefit |
|---|---|---|
| 1. Application Control | Execution of unapproved or malicious software (e.g., malware, ransomware). | Prevents unauthorised programs from running, stopping most malware attacks before they can start. |
| 2. Patch Applications | Exploitation of known security vulnerabilities in everyday software. | Closes security holes in software like browsers and PDF readers, blocking a common entry point for attackers. |
| 3. Configure Microsoft Office Macro Settings | Malicious code execution via macros in Office documents. | Stops attackers from using booby-trapped documents to gain a foothold in your network. |
| 4. User Application Hardening | Exploitation of vulnerable features in common applications. | Reduces the 'attack surface' of your software by disabling risky, non-essential features. |
| 5. Restrict Administrative Privileges | Widespread network compromise after a single account is breached. | Limits the damage an attacker can do by containing them to a single user's account, not the whole system. |
| 6. Patch Operating Systems | Exploitation of vulnerabilities in Windows, macOS, Linux, and network devices. | Secures the foundational software of your systems, protecting against worms and other automated attacks. |
| 7. Multi-Factor Authentication | Unauthorised access using stolen or guessed passwords. | Makes stolen passwords useless, providing a massive barrier against account takeovers. |
| 8. Regular Backups | Data loss from ransomware, hardware failure, or accidental deletion. | Guarantees you can restore operations quickly after a major incident, ensuring business continuity. |
By implementing these controls together, you create a robust, layered defence that makes your business a much harder and less attractive target for cybercriminals.
Strategy 1: Application Control
Imagine Application Control as a strict "guest list" for your computers. Only pre-approved, trusted software is allowed to run. Everything else gets blocked at the door, no questions asked. This one strategy is an absolute game-changer because it stops most malware, including many ransomware variants, dead in its tracks.
Cybercriminals need their malicious programs to execute. If an employee accidentally clicks a bad link that tries to run an unknown file, Application Control simply says, "Sorry, you're not on the list," and shuts it down. This proactive block is far more effective than trying to chase down a threat after it's already running rampant.
Strategy 2: Patch Applications
The software you use daily—web browsers, office suites, PDF readers—is constantly being updated by developers. These updates, or patches, often contain urgent security fixes for flaws that attackers are actively looking for. Not patching is like leaving a known weak spot in your armour.
This strategy is all about applying security patches promptly. The ACSC’s advice is clear: patch any 'extreme risk' vulnerabilities in your applications within 48 hours. Regular, disciplined patching ensures those known security holes are sealed before criminals get a chance to wiggle through them.
Strategy 3: Configure Microsoft Office Macro Settings
Microsoft Office macros are small scripts that automate tasks, but they're also a classic weapon in an attacker's arsenal. They trick users into opening a weaponised Word doc or Excel sheet and enabling macros, which then executes code to download malware or steal data.
To shut this down, you need to configure Office to block all macros from files downloaded from the internet. If your business genuinely needs macros, they should only be allowed to run from highly trusted, secure locations and be digitally signed to prove they haven't been tampered with.
Strategy 4: User Application Hardening
This one is about reducing the 'attack surface' of the software your team relies on. It means disabling or removing features that aren't essential for business but could be exploited by attackers.
A few examples of what this looks like in practice:
- Blocking Flash content in web browsers, as it's a notorious target.
- Disabling unnecessary browser add-ons or plugins that might introduce their own security holes.
- Preventing Java from running on the web, where it’s rarely needed anymore.
By hardening your applications, you're essentially trimming away potential entry points. It makes it much harder for an attacker to find a foothold through the everyday software you use.
Strategy 5: Restrict Administrative Privileges
An administrative account is the "master key" to a system. It can install software, change critical settings, and access every single file. If an attacker gets their hands on one of these, it's game over. The solution is the principle of least privilege.
This strategy means every user should only have the bare minimum level of access they need to do their job. Admin rights should be locked down tight and only used for specific, necessary tasks. Day-to-day work like checking email or browsing the web should always be done from a standard, non-admin account.
This simple separation dramatically limits the potential damage. If a standard account is compromised, the attacker might see that user's files, but they won't be able to take over your entire network.
Strategy 6: Patch Operating Systems
Just like your applications, your operating systems (Windows, macOS, Linux) need regular security patches. These updates fix vulnerabilities found in the core system software. You can bet that attackers are constantly scanning the internet for unpatched systems, knowing they are low-hanging fruit.
The guidance here is just as urgent: patch or mitigate 'extreme risk' vulnerabilities in operating systems within 48 hours. This isn't just for servers and workstations; it includes network gear like routers and firewalls, too. Running unsupported operating systems that no longer get security updates is a massive, unacceptable risk.
Strategy 7: Multi-Factor Authentication
A password alone is no longer enough security. It's just not. Multi-factor authentication (MFA) adds a vital second layer of security by asking users to prove their identity with something more than just what they know (their password).
This is usually something you have (like a code from an authenticator app on your phone) or something you are (like a fingerprint). MFA is one of the single most effective ways to stop unauthorised access. Even if an attacker steals a user's password, they're stopped cold because they don't have that second factor.
You should have MFA on everything important: all internet-facing services, remote access systems like your VPN, and anywhere sensitive company data is stored.
Strategy 8: Regular Backups
This final strategy is your ultimate safety net. When a disaster happens—a catastrophic hardware failure, a devastating ransomware attack, or simple data corruption—reliable backups are often the only thing that can get you back in business. This means more than just occasionally copying files to an external hard drive.
This control demands daily backups of your important data, software, and system configurations. These backups absolutely must be stored separately from your main network—with at least one copy held offline—and kept for a minimum of three months.
And crucially, you have to test your ability to restore from these backups regularly. An untested backup is just a hope, not a plan. A core part of business resilience is having a proven data recovery process, like implementing robust backup strategies for Linux systems and other critical platforms.
Understanding the Modern Australian Cyber Threat Landscape
The conversation around cybersecurity has changed for good. It's no longer a question of if a cyber attack will happen, but a matter of when. For Australian businesses, this isn't just a distant warning; it's the daily reality of a threat environment that's getting more dangerous by the day. Proactive defence is now the only way to survive and grow.
Cybercriminals have shifted their focus. They aren't just going after the big end of town anymore. Small and medium-sized businesses (SMEs) are now squarely in their sights, often seen as an easier path into larger supply chains. In fact, these businesses make up a shocking 43% of all cyber attack targets in Australia, battling constant waves of ransomware, phishing scams, and sophisticated data breaches.
The Real-World Consequences
When an attack lands, the fallout is far more than a simple IT headache. The consequences can be devastating, sending ripples through every part of your business.
- Financial Loss: Think beyond just the direct hit. You're looking at potential ransom payments, hefty regulatory fines, and the massive cost of getting your systems back up and running.
- Reputational Damage: Trust is earned over years but can be shattered in an instant. A public data breach erodes customer confidence, leading to lost clients and a tarnished brand that can take years to repair.
- Operational Downtime: When ransomware locks your systems or a breach takes you offline, business stops. Every minute of downtime means lost revenue, missed deadlines, and a total halt in productivity.
This isn't just theory. The Australian Signals Directorate (ASD) fielded over 42,500 calls to its Cyber Security Hotline in the 2024-2025 financial year. That’s a 16% jump from the year before, and it paints a clear picture: attacks are on the rise, and businesses need a solid defence. This is precisely why a framework like the ACSC Essential 8 is so critical.
From Best Practice to Business Imperative
In this climate, implementing the ACSC Essential 8 is no longer a "nice-to-have." It’s moved from a best-practice recommendation to a fundamental business requirement. The framework gives you a structured, proven approach to shutting down the most common attack methods that hit Australian organisations again and again.
Adopting the Essential 8 is an act of strategic resilience. It's about taking deliberate, prioritised steps to make your organisation a harder, less attractive target for opportunistic and determined attackers alike.
By focusing on these eight core controls, you drastically shrink your attack surface. You also send a powerful message to clients, partners, and regulators that you take security seriously—not just for your own operations, but for the sensitive data they’ve entrusted to you. As business models evolve, knowing how to protect your organisation and employees is paramount.
How the Essential 8 Complements ISO 27001
For many Australian businesses, especially those with global ambitions, tackling an international standard like ISO 27001 can feel like a completely separate, uphill battle. But here’s the good news: the hard work you pour into implementing the ACSC Essential 8 isn’t a detour. It’s a massive head start.
Think of it this way: the Essential 8 is you laying a solid, steel-reinforced concrete slab. ISO 27001 is the entire architectural blueprint for the skyscraper you're building on top of it. One is about practical, foundational strength; the other is the holistic plan for the whole structure.
The two frameworks were born from different perspectives, but they work together beautifully. The Essential 8 gives you specific, tactical defences against the most common cyber attacks we see day in and day out. ISO 27001, on the other hand, provides the framework for a complete Information Security Management System (ISMS)—a comprehensive, risk-based approach to managing your organisation's entire security landscape.
Building a Strong Foundation for Your ISMS
When you implement the Essential 8, you’re creating tangible proof of your security diligence. This isn't just theory; it's operational security in action, and that’s precisely what auditors want to see for ISO 27001. They’re looking for evidence that you have real-world controls managing the risks you’ve identified.
For example, when you nail controls like 'Restrict Administrative Privileges' and 'Multi-Factor Authentication', you're directly ticking boxes for the access control objectives in ISO 27001's Annex A. This alignment means you’re not starting your ISO journey from a standstill. You’ve already built, tested, and proven some of the most critical security functions.
By mastering the ACSC Essential 8, you are building a practical, battle-tested foundation for your ISMS. This streamlines the path to ISO 27001 certification, saves resources, and helps you demonstrate a mature security posture to regulators and partners.
This practical overlap makes the entire certification process far more efficient. Instead of just talking about security policies, you can point to existing, functioning processes that are already defending your business every single day.
Mapping Essential 8 to ISO 27001 Annex A
The real magic happens when you map the controls side-by-side. You'll quickly see that the Essential 8 strategies align almost perfectly with the control domains in Annex A of ISO 27001—the catalogue of security control objectives. Understanding this relationship is a game-changer. You can dig deeper into the full list of ISO 27001 controls to see just how intertwined they are.
To give you a clearer picture, we've put together a table showing how these frameworks support each other.
Mapping ACSC Essential 8 to ISO 27001 Annex A Controls
| ACSC Essential 8 Strategy | Relevant ISO 27001 Annex A Control Area | Synergistic Benefit |
|---|---|---|
| Restrict Administrative Privileges | A.5.15, A.8.2 – Access Control | Provides concrete evidence of 'least privilege' principles, a fundamental requirement for managing user access rights. |
| Patch Applications & Operating Systems | A.8.5, A.8.19 – Technical Vulnerability Management | Directly demonstrates a robust process for identifying and remediating security vulnerabilities in a timely manner. |
| Multi-Factor Authentication | A.5.16, A.5.17 – Authentication Information | Fulfills requirements for strong authentication mechanisms to protect access to systems and applications. |
| Regular Backups | A.8.13 – Information Backup | Serves as direct proof of a data backup and recovery strategy, crucial for business continuity and data availability. |
This mapping makes one thing crystal clear: implementing the ACSC Essential 8 is far more than a local compliance task. It's a strategic investment in your security posture that pays huge dividends when you decide to pursue international certification, making your business both more secure and more competitive on the world stage.
Building Your Essential 8 Implementation Roadmap
Knowing you need to implement the ACSC Essential 8 is one thing; actually doing it is another. The key is to turn this list of best practices into a clear, actionable plan. Without a proper roadmap, it's easy to get overwhelmed. A structured approach breaks the whole project down into manageable chunks, letting you see real, measurable progress towards a much stronger security posture.
We can think of this journey in four distinct phases. Each stage naturally builds on the one before, taking you from figuring out where you stand today to keeping your defences sharp for the long haul.
Phase 1: Assess Your Current Position
You can't plan a trip without knowing your starting point. This first phase is all about creating a baseline. Where does your security currently sit when measured against the Essential 8? The goal here is simple: identify what you're already doing right and, more importantly, find the gaps.
This doesn't have to be a massive, complex audit right out of the gate. You can start by asking some direct questions for each of the eight controls.
- Application Control: Do we even have a list of approved software? Are we actively stopping unauthorised programs from running on our systems?
- Patching: Realistically, how quickly are we rolling out security patches for our software and operating systems? Is it anywhere near the recommended 48-hour window for the really critical stuff?
- Backups: Are we backing up our important data every day? Do we keep a copy completely offline, safe from ransomware? And when was the last time we actually tried to restore from a backup to see if it works?
Running this gap analysis is your crucial first step. A structured cybersecurity risk assessment template is a great guide for systematically looking at your environment.
Phase 2: Prioritise for Maximum Impact
Once your assessment is done, you'll have a much clearer picture of your security weaknesses. Now it's time to prioritise. Let's be honest, especially for a small business with limited resources, you can't fix everything at once. The trick is to focus on the quick wins that give you the biggest security boost for your efforts.
For most small to medium businesses, this usually means starting with the controls that stop malware in its tracks and prevent attackers from getting unauthorised access.
If you're wondering where to start, a highly effective approach is to prioritise Application Control, Patch Applications, and Multi-Factor Authentication. Nailing just these three can shut down the vast majority of opportunistic cyber attacks we see across Australia.
This risk-based approach makes sure your initial time and money go where they'll make the biggest difference in shrinking your attack surface.
Phase 3: Implement and Refine
This is where the real work begins. You'll start rolling out the new controls and processes you’ve planned, kicking off with those high-priority items. This could mean deploying new software to manage application whitelisting, getting much stricter with your patching schedule, or finally enforcing MFA across all your critical services.
It's absolutely critical to treat this as a cycle, not a one-off task. Implement a control, watch how it affects your day-to-day operations, get feedback from your team, and then tweak it as you go. Communication is everything here—make sure your staff know why these changes are happening and how they're helping protect the business.
Phase 4: Measure and Maintain
Cybersecurity is never "set and forget". The final phase of your roadmap is a continuous loop of measuring your progress and maintaining your defences. You have to constantly check that your controls are working as intended and remain effective over time.
Regularly go back to your initial assessment to see how you're tracking towards your target Maturity Level. Schedule routine tests, like trying a full data restore from your backups or running vulnerability scans to find new holes. This ongoing vigilance is what turns your Essential 8 implementation from a project with an end date into a living, breathing part of your business's defence.
Your Essential 8 Questions Answered
When you start digging into the ACSC Essential Eight, it’s natural for questions to pop up. How does this apply to my business? Where do I even begin? Here, we'll tackle the most common questions we hear from Australian businesses, giving you clear, no-nonsense answers to help you move forward with confidence.
Is the ACSC Essential 8 Mandatory for My Business?
This is the big one, and the answer isn't a simple yes or no. Officially, the Essential Eight is mandatory for non-corporate Commonwealth entities. But for everyone else, the ACSC strongly recommends it as the baseline for cyber security in all Australian organisations. Think of it less as a rule and more as the standard of care for doing business today.
What’s really pushing this into the mainstream, though, are contracts. If you’re a supplier to government or work in critical infrastructure, you’ll likely find Essential Eight compliance is a non-negotiable part of your agreements. Mandate aside, implementing these controls is simply good business practice—it's about protecting your operations, your reputation, and your customers' trust.
Which of the Essential 8 Should I Implement First?
While a proper risk assessment will give you a detailed game plan, the ACSC provides a pretty clear starting point for getting the most bang for your buck. Your first move should be to stop malware in its tracks.
That means prioritising two specific controls right out of the gate:
- Application Control: This is like having a strict bouncer at the door of your network, only letting approved software in and keeping malicious programs out.
- Patch Applications: This is cyber security 101. It involves closing the known security holes in the software you use every day—the very same backdoors that attackers love to exploit.
Once you’ve got that foundation in place, rolling out Multi-factor Authentication (MFA) is probably the single most powerful step you can take. It immediately shuts down the threat from stolen passwords, which are still one of the main ways attackers get in.
How Does the Essential 8 Help Against Phishing Attacks?
Phishing is relentless, and the Essential Eight framework is built to fight it with a defence-in-depth strategy. These attacks have become one of Australia's most stubborn and clever cyber threats. Recent data shows that, on average, 1.2% of Australian employees clicked on phishing links each month over the past year—a shocking 140% increase. The controls work together as a team to shut these attacks down. You can learn more about the evolving Australian cyber threat landscape and the rise of phishing on securityquotient.io.
Here’s how the different layers work together to stop a phishing attempt:
- Configure Microsoft Office Macro Settings: This stops a common phishing tactic dead in its tracks by preventing malicious code hidden in Word or Excel files from running.
- User Application Hardening: This control blocks the malicious ads and dodgy browser scripts that are often the delivery mechanism for phishing campaigns.
- Multi-factor Authentication: This is your ultimate safety net. Even if an employee is tricked into giving up their password, MFA ensures the attacker still can't get into their account.
What Are the Maturity Levels and Which Should We Aim For?
The Maturity Levels are a fantastic roadmap. They give you a clear, step-by-step way to improve your defences over time, letting you match your security efforts to your specific risk profile.
Maturity Level One is the perfect starting point for most small to medium businesses. It establishes a solid baseline that protects you from the common, opportunistic attacks that cybercriminals launch every day using readily available tools.
From there, you can climb the ladder to guard against more serious threats:
- Maturity Level Two is for businesses with a higher risk profile—maybe you handle more sensitive data or you're in an industry that's a bigger target.
- Maturity Level Three is the top tier, designed for critical infrastructure and organisations that could be targeted by sophisticated, well-funded attackers.
The best way to figure out which level is right for you is with a risk assessment. It ensures you're putting your time and money where it will have the biggest impact, without over-investing in controls you might not need just yet.
Navigating the path to implementing the ACSC Essential 8 and achieving ISO 27001 certification can feel overwhelming, but you don't have to go it alone. We specialise in helping Australian small businesses build robust and compliant security systems. Let our experts guide you with a clear, straightforward roadmap to a stronger, more resilient business. Find out how we can help.
Recent Comments