

APRA CPS 234 is a prudential standard from the Australian government that sets out strict, non-negotiable information security rules for all APRA-regulated businesses. Think of it less as a set of guidelines and more as a mandatory framework for protecting your most critical data. Its main job is to make sure these organisations can stand strong against security incidents, especially cyber-attacks, by building and maintaining a seriously robust security posture.
Building a Digital Fortress: Why APRA CPS 234 Is So Crucial
Picture a bank vault. You wouldn't just slap a single padlock on the door and call it a day, right? Of course not. A real vault has layers upon layers of security—thick steel walls, complex time-locks, constant surveillance, and guards on patrol. Each element has a job, and together they create a defence that’s almost impossible to breach.
In today's financial world, your organisation’s data is the new gold, and APRA CPS 234 is the architectural blueprint for building its digital fortress.
This standard effectively pulls information security out of the server room and places it squarely in the boardroom. It’s no longer just an IT problem; it’s a core business responsibility. CPS 234 lays down a clear set of rules to protect the confidentiality, integrity, and availability of your data, ultimately protecting the interests of depositors, policyholders, and superannuation fund members.
To give you a clearer picture, here's a quick rundown of what CPS 234 demands.
APRA CPS 234 At a Glance
The table below summarises the core components and key obligations of the standard, giving you a high-level view of what compliance looks like in practice.
| Core Requirement | Objective | Key Obligation |
|---|---|---|
| Information Security Framework | Establish a clear, board-approved strategy for managing information security. | Define roles, responsibilities, and the overall security policy. |
| Information Asset Management | Identify and classify all critical and sensitive data assets. | Maintain an inventory of information assets and assign ownership. |
| Implementation of Controls | Put security controls in place to protect assets from threats and vulnerabilities. | Controls must be proportional to the asset's criticality and the threat level. |
| Incident Management | Develop a robust plan to detect, respond to, and recover from security incidents. | Notify APRA within 72 hours of a material incident. |
| Testing of Controls | Regularly test the effectiveness of your security controls. | Conduct systematic testing by skilled, independent specialists. |
| Third-Party Management | Ensure third-party providers also meet your security standards. | Assess the security posture of any vendor handling your information assets. |
| Internal Audit | Have an independent internal audit function review your security controls. | The audit must assess the adequacy and effectiveness of your controls. |
This framework ensures that every aspect of information security is addressed, from foundational policies right through to how you handle a crisis.
Who Needs to Comply with CPS 234?
The reach of CPS 234 is wide, covering pretty much the entire Australian financial services industry. It’s not just for the big four banks. If you're regulated by APRA, this standard applies to you.
Compliance is mandatory for:
- Banks and Credit Unions: Every authorised deposit-taking institution (ADI) is covered, from the largest national players to the smallest local credit unions.
- Insurance Companies: This includes general insurers, life insurance companies, and private health insurers—all of whom handle a huge amount of sensitive customer data.
- Superannuation Funds: All registrable superannuation entity (RSE) licensees must comply to safeguard the retirement savings of millions of Australians.
Bottom line: if APRA is your regulator, CPS 234 is your reality. And it doesn't stop with you; the rules extend to any third parties you use to manage your data.
The Driving Force Behind the Standard
So, why did APRA introduce this standard? It was a direct reaction to a threat environment that was spiralling out of control. APRA officially launched CPS 234 on 1 July 2019, because the financial sector was getting hammered by cyber-attacks.
Even back in 2018, a staggering 90% of Australian companies reported they were on the receiving end of cyber-attack attempts. Faced with those numbers, APRA knew that friendly advice wasn't cutting it anymore. A legally binding framework became an urgent necessity. For a deeper dive into the drivers behind the regulation, you can find more background on CPS 234 compliance at Vanta.com.
The standard works on a simple but powerful principle: your security capability must be directly proportional to the size and scale of the threats you face.
The core idea is crystal clear: your security measures have to be just as sophisticated as the threats you’re trying to stop. APRA CPS 234 reframes information security not as a box-ticking exercise, but as a fundamental pillar of business resilience and customer trust.
Throughout this guide, we'll break down exactly what this means for you. We’ll cover everything from identifying your critical data and testing your security controls to managing third-party risks and responding effectively when the worst happens. By the end, you won't just be aiming for compliance; you'll be building a truly resilient security culture.
The Core Pillars of APRA CPS 234 Compliance
To really get to grips with APRA CPS 234, you need to understand its foundational requirements. Think of these as the core pillars holding up your entire security strategy. They aren’t just a checklist of tasks to tick off; they're interconnected parts of a single, powerful system designed to keep your business safe.
Each pillar builds on the last, creating a comprehensive defence that’s both proactive and reactive. Getting compliant isn't about buying the flashiest new technology. It's about building a systematic, repeatable process for managing your information security. Let's break down these core pillars, using some straightforward analogies to show what they mean in the real world.
Pillar 1: Identifying Your Most Valuable Information Assets
You can't protect what you don't know you have. This is the first, and arguably most crucial, step in the whole CPS 234 journey.
Imagine you're the curator of a massive library. Your collection has everything from common paperbacks to priceless, first-edition manuscripts. Your first job isn't to install security cameras everywhere; it's to create an inventory. You have to identify every single book, assess its value, and figure out which ones need the highest level of protection.
That’s exactly what information asset identification is all about. You need to create a complete catalogue of your data, sorting each asset based on how critical and sensitive it is.
An "information asset" isn't just a database. It could be customer records, financial transaction data, strategic business plans, employee details, or intellectual property. If it has value and could cause significant damage if compromised, it needs to be on your list.
Once you’ve identified an asset, you must assign it a clear owner within the business. This creates accountability. That owner is now responsible for its security, for deciding who gets to access it, and for understanding its role in the business. Without clear ownership, critical data often falls through the cracks, left completely exposed.
Pillar 2: Implementing Proportional Security Controls
Once you’ve identified and classified your valuable assets, the next step is to put the right security controls in place to protect them. This isn’t a one-size-fits-all approach; it’s about proportional security.
Let's go back to our library analogy. You wouldn't store a common paperback and a medieval manuscript in the same way. The paperback might sit on an open shelf, but the manuscript would be locked away in a climate-controlled, fireproof vault with heavily restricted access. The security measures are proportional to the asset's value and the threats it faces.
This is the central idea behind implementing controls under APRA CPS 234. Your security measures have to match the importance of the data they’re protecting.
Your control framework should have a healthy mix of preventative, detective, and corrective measures.
- Preventative Controls: These are your front-line defences, designed to stop an incident before it even starts. Think firewalls, access control policies, multi-factor authentication (MFA), and staff security training.
- Detective Controls: These are your alarm systems, meant to spot an incident while it’s happening or just after. This includes intrusion detection systems, security monitoring logs, and internal audits.
- Corrective Controls: When an incident happens, these controls help you respond and fix the problem, limiting the damage. This is where data backup and recovery systems and your formal incident response plan come in.
The key is to build layers of defence. A single control can fail, but a multi-layered system creates a much more resilient barrier against would-be attackers.
Pillar 3: Rigorous Security Control Testing
It’s one thing to install locks and alarms. It's another thing entirely to know they'll actually work during a break-in. This is where the third pillar, security control testing, comes into play. It’s all about regularly stress-testing your defences to find the weak spots before an attacker does.
Think of it as hiring a team of specialists to try and break into your library's vault. You want them to test the locks, try to bypass the alarms, and see if they can trick the guards. Their job is to find vulnerabilities so you can patch them up.
APRA CPS 234 insists that this testing must be systematic and carried out by skilled, functionally independent specialists. This ensures the assessment is unbiased and truly thorough.
Common forms of control testing include:
- Vulnerability Assessments: Scanning your systems for known security flaws.
- Penetration Testing: Simulating a real-world cyber-attack to test how your defences hold up.
- Control Design Reviews: Looking at your security controls on paper to see if they're designed correctly in the first place.
- Internal Audits: An independent review of your entire information security framework to make sure it's actually meeting its objectives.
Regular testing gives the board and senior management real assurance that the organisation’s security posture is genuinely effective, not just compliant on paper. It turns your security framework from a static document into a living, breathing defence mechanism.
Pillar 4: Mastering Incident Management and Response
No matter how strong your defences are, you have to plan for the worst-case scenario. The final pillar, incident management and response, is your critical action plan for when a breach happens.
This is your organisation’s fire department. When the alarm sounds, you need a well-drilled team that knows exactly what to do. They need the right tools, clear procedures, and the authority to act fast to contain the fire, minimise the damage, and get things back to normal as quickly as possible. A chaotic, unprepared response just pours fuel on the fire.
Your incident response plan must cover the entire lifecycle of an incident, from the first sign of trouble to the post-incident review. This means having clear steps for:
- Detection and Analysis: How will you spot a security incident? Who is responsible for assessing its severity?
- Containment: How do you stop the breach from spreading and causing more damage?
- Eradication: How do you completely remove the threat from your environment?
- Recovery: How do you safely restore affected systems and data?
- Post-Incident Review: What did we learn? How can we stop this from happening again?
A huge part of this is communication. APRA requires you to notify them within 72 hours of becoming aware of a material information security incident. This demands a streamlined process for escalating incidents and making swift, informed decisions. Having a solid plan isn't just good practice—it's a non-negotiable part of APRA CPS 234.
Managing Your Digital Supply Chain Risk
Let's be realistic: no business operates in a vacuum anymore. You're almost certainly relying on a whole network of third-party vendors for everything from cloud hosting and software platforms to data analytics and customer support. This is your digital supply chain, and while it's fantastic for efficiency, it also opens up a Pandora's box of security risks.
And on this point, APRA CPS 234 is crystal clear: you can't outsource your responsibility.
Think of it like this. You're the prime contractor building a new skyscraper. You hire subcontractors for specialised jobs—electrics, plumbing, windows. If a subcontractor uses shoddy wiring that starts a fire, who is ultimately responsible? You are. The buck stops with the prime contractor.
That’s exactly how APRA sees your data. Passing a service to a vendor doesn't mean you've passed on the risk. You remain 100% accountable for the security of your information assets, no matter where they live or who manages them. Your security is only as strong as its weakest link, and often, that link is an external partner.
The Mandate for Third-Party Diligence
CPS 234 demands a formal, rigorous process for managing the security risks that come with every single third-party provider touching your data. This isn't a friendly suggestion; it’s a non-negotiable part of compliance. You have to be ready to prove to APRA that you have a firm grip on the security of your entire digital supply chain.
This means you need a proper third-party risk management program. It needs to cover the full lifecycle of your vendor relationships, from the moment you consider them to the day you part ways. This has to be a proactive, continuous effort, not just a tick-box exercise during onboarding.
Step 1: Initial Due Diligence And Onboarding
Before any ink dries on a contract, you must conduct thorough due diligence on any potential vendor. This is your chance to really kick the tyres and scrutinise their security capabilities to see if they’re up to scratch.
Key activities here should include:
- Security Posture Assessment: Ask for and review their security policies, procedures, and any certifications they hold, like ISO 27001 or SOC 2 reports.
- Risk Evaluation: Analyse their control environment. Is it robust enough to protect the specific information assets you'll be entrusting to them?
- Data Handling Practices: Get a clear picture of how they will access, process, store, and transmit your data. You also need to know where, geographically, that data will be.
This initial deep dive is absolutely critical. It is far, far easier to choose a secure partner from day one than to try and patch the security holes of a vendor who is already deeply embedded in your operations.
Step 2: Clear Contractual Security Obligations
Once a vendor has passed your checks, the next step is embedding specific, unambiguous security requirements directly into your contract. A verbal agreement or a generic service level agreement (SLA) just won't cut it.
Your contracts must spell out, in no uncertain terms, the security controls the vendor is required to have in place.
Your contract is your most powerful enforcement tool. It transforms security expectations into legally binding obligations, giving you the right to audit the vendor and hold them accountable for any failures.
Specifically, your contracts should cover:
- The classification of the information assets they’ll be handling.
- The specific security controls they must implement and maintain.
- Your right to audit their controls and security practices.
- Their obligation to notify you immediately if a security incident occurs.
- Requirements for the secure handling and destruction of your data when the contract ends.
Without these clauses, you have no real power to enforce your security standards.
Step 3: Ongoing Monitoring And Assessment
Getting a vendor onboarded securely is just the start. The threat landscape is always shifting, and so is your vendor's security posture. APRA CPS 234 requires you to continuously assess and monitor your partners to ensure they remain compliant for the entire duration of your relationship.
This is where the standard gets particularly tough. The regulation demands stringent oversight of third-party service providers, mandating that you re-evaluate them as threats evolve. These risk assessments must dig into their vulnerabilities, the importance of the data they hold for you, and the potential fallout from an incident. Often, this involves using tools like risk registers and heat maps to guide your strategy.
This ongoing oversight is critical for maintaining a strong defence. And when you think about your digital supply chain, remember to cast a wide net. Even functions like outsourced recruitment introduce third-party risk. A guide on understanding models for Recruitment Process Outsourcing can offer a broader perspective on these kinds of external partnerships.
Ultimately, managing your digital supply chain under CPS 234 is all about extending your own security culture and controls to your partners. It takes diligence, clear communication, and an unwavering commitment to continuous oversight. By fortifying this critical front, you protect your organisation not just from direct attacks, but from the inherited risks that come with the vendors you trust.
Leveraging ISO 27001 for CPS 234 Compliance
If your organisation is already certified or aligned with ISO 27001, the thought of tackling another major security standard like APRA CPS 234 can feel like a mountain to climb. But here’s the good news: you’re not starting from scratch. Far from it, actually. Your existing Information Security Management System (ISMS) is a powerful head start.
Think of ISO 27001 as the foundational blueprint for a secure house. It establishes the structure, the processes, and the overall framework for managing information security in a systematic way. APRA CPS 234, on the other hand, is like a set of very specific, non-negotiable building codes required for houses built in a high-risk, cyclone-prone area. It doesn't replace the blueprint; it just adds mandatory reinforcements on top of it.
Your investment in ISO 27001 gives you a massive advantage. It allows you to map many of the CPS 234 requirements directly to controls you probably already have in place. This approach saves an enormous amount of time, slashes duplicate effort, and helps build a single, unified security strategy that satisfies both sets of requirements.
Mapping the Overlaps Between Standards
At their heart, both frameworks share the same DNA: identify your risks, put sensible controls in place, and never stop improving. Many of the technical and operational controls you’ve implemented from ISO 27001's Annex A provide a solid answer to the demands of CPS 234.
This synergy means you can translate a lot of your existing work directly. For example, your processes for asset management, access control, and cryptography under ISO 27001 already form the backbone of what CPS 234 requires for protecting information assets. Our comprehensive guide on achieving ISO 27001 compliance takes a much deeper look into these foundational elements.
So, how does this look in practice? Let's break down the mapping between some key areas.
Here is a comparative look at how key requirements of APRA CPS 234 align with the clauses and controls within the ISO 27001 framework.
Mapping APRA CPS 234 Requirements to ISO 27001 Controls
| APRA CPS 234 Requirement | Corresponding ISO 27001 Clause/Control | Key Differences and Considerations |
|---|---|---|
| Board Accountability | Clause 5: Leadership & Commitment | CPS 234 is far more explicit. It demands the Board be directly accountable for information security and for ensuring controls are maintained. |
| Information Asset Identification | A.8: Asset Management | Both require an asset inventory. CPS 234, however, puts a heavy emphasis on classifying assets based on their criticality and sensitivity, directly linking this to business impact. |
| Implementation of Controls | Clause 6: Planning; Annex A Controls | ISO 27001 offers a broad catalogue of potential controls. CPS 234 insists that the controls you choose must be proportional to the threat and the value of the asset. |
| Incident Management | A.16: Information security incident management | Both require a solid response plan. The game-changer with CPS 234 is the strict 72-hour notification deadline to APRA for any material incidents. |
| Control Testing | A.18: Compliance; Clause 9: Performance evaluation | While ISO 27001 requires regular reviews, CPS 234 mandates systematic testing by functionally independent and skilled specialists—a much higher bar. |
| Third-Party Management | A.15: Supplier Relationships | Both cover supplier security, but CPS 234 is intensely focused here. It requires you to ensure that vendors with access to your assets also comply with the standard. |
As you can see, there’s a tonne of overlap, but the table also highlights exactly where CPS 234 adds a thick layer of regulatory rigour.
Identifying the Critical Gaps
While ISO 27001 provides the 'what' and 'how', APRA CPS 234 is laser-focused on the 'who' and 'when', especially when it comes to accountability and timelines. It’s simply not enough to have controls; you must be able to prove they are effective and that the Board is actively overseeing them.
Think of it this way: ISO 27001 helps you build a strong security management system. CPS 234 forces you to prove that system can withstand the specific pressures and threats faced by the Australian financial sector, with direct accountability resting at the very top of your organisation.
The most significant gaps you’ll likely need to bridge are:
- Explicit Board Accountability: Your existing ISO 27001 framework might tick the "leadership commitment" box, but CPS 234 requires demonstrable, Board-level responsibility for the information security policy and control effectiveness. This means Board meeting minutes, formal reports, and clear charters are non-negotiable evidence.
- Mandatory Incident Notification: That 72-hour notification rule is a hard deadline. It demands a highly efficient incident classification and escalation process that’s been tested and proven. Your ISO 27001 incident response plan must be updated to include this specific, time-sensitive regulatory step.
- Independent Control Testing: The CPS 234 requirement for testing by functionally independent parties is stricter than a standard internal audit. This often means bringing in external testers or ensuring your internal audit team has a distinct, separate reporting line for this specific function.
By focusing your energy on these key differences, you can efficiently upgrade your existing ISMS. Instead of building an entirely new compliance program from the ground up, you are simply reinforcing your current one to meet the specific, high-stakes demands of a prudential regulator. It’s a strategic approach that ensures you not only achieve compliance but also build a genuinely resilient security posture.
Your Actionable APRA CPS 234 Compliance Roadmap
Knowing the rules of APRA CPS 234 is one thing. Actually putting them into practice across your business is a whole different ball game. It’s easy to get lost in the details, so let's break it down into a clear, phased project plan you can start using today.
Think of this roadmap as a blueprint for building genuine cyber resilience, not just a box-ticking exercise. Each phase builds on the last, taking you logically from figuring out where you stand to achieving a state of constant, defensible compliance.
Phase 1: Discovery and Assessment
You can't build a fortress without first surveying the land. This first phase is all about getting a brutally honest look at your current security situation. You need to know what your most valuable assets are and, crucially, identify the gaps between what you're doing now and what APRA demands.
Skipping this foundational work is a recipe for disaster. Here’s what you need to do:
- Identify and Classify Information Assets: You can't protect what you don't know you have. Your first job is to create a full list of all your information assets. Then, you need to classify them based on how critical they are to keeping the lights on.
- Audit Existing Security Controls: Take a hard look at every security control you currently have in place. This means everything from firewalls and access policies right through to your incident response plans and the security clauses in your third-party contracts.
- Perform a Gap Analysis: Now, compare your current setup against every single requirement in APRA CPS 234. This analysis becomes your roadmap for the next phase, highlighting exactly where you need to focus your efforts.
Getting this initial assessment right gives you the clarity to build a targeted and efficient plan. You'll stop wasting time and money on the wrong things and focus your resources where they’ll have the biggest impact.
Phase 2: Implementation and Remediation
With a clear picture of your gaps, it's time to roll up your sleeves and get to work. Phase 2 is where the heavy lifting happens. We're talking about writing solid policies, deploying the right tech, and making sure your people are your strongest defence, not your weakest link.
This is a big job that will touch almost every part of your organisation. Getting everyone on board is key. To help manage this shift, exploring professional change management facilitation programs can make the transition much smoother for your team.
Here are your key actions for this phase:
- Develop and Formalise Policies: Write (or update) your information security policies so they perfectly align with CPS 234. These can't just sit on a shelf; they need to be formally signed off by the Board to show that accountability starts at the top.
- Deploy Technical Controls: Start implementing the security measures you identified in your gap analysis. This might mean rolling out multi-factor authentication (MFA), beefing up your data encryption, or strengthening your network segmentation.
- Strengthen Third-Party Management: Go through every single one of your vendor contracts and add specific, enforceable security clauses. You also need a program to continuously monitor any third party that handles your critical information.
- Conduct Comprehensive Staff Training: Your people are your first line of defence. Run targeted training sessions that go beyond a simple "don't click on phishing links" email. The training needs to be relevant to their specific roles and responsibilities under the new security rules.
Remember, the goal here isn't just to tick boxes. It's about putting controls in place that actually work and are proportional to the risks you face. Every single control should directly fix a specific weakness you found back in Phase 1.
This process chart shows how using an existing framework like ISO 27001 can give you a massive head start on your APRA CPS 234 journey.
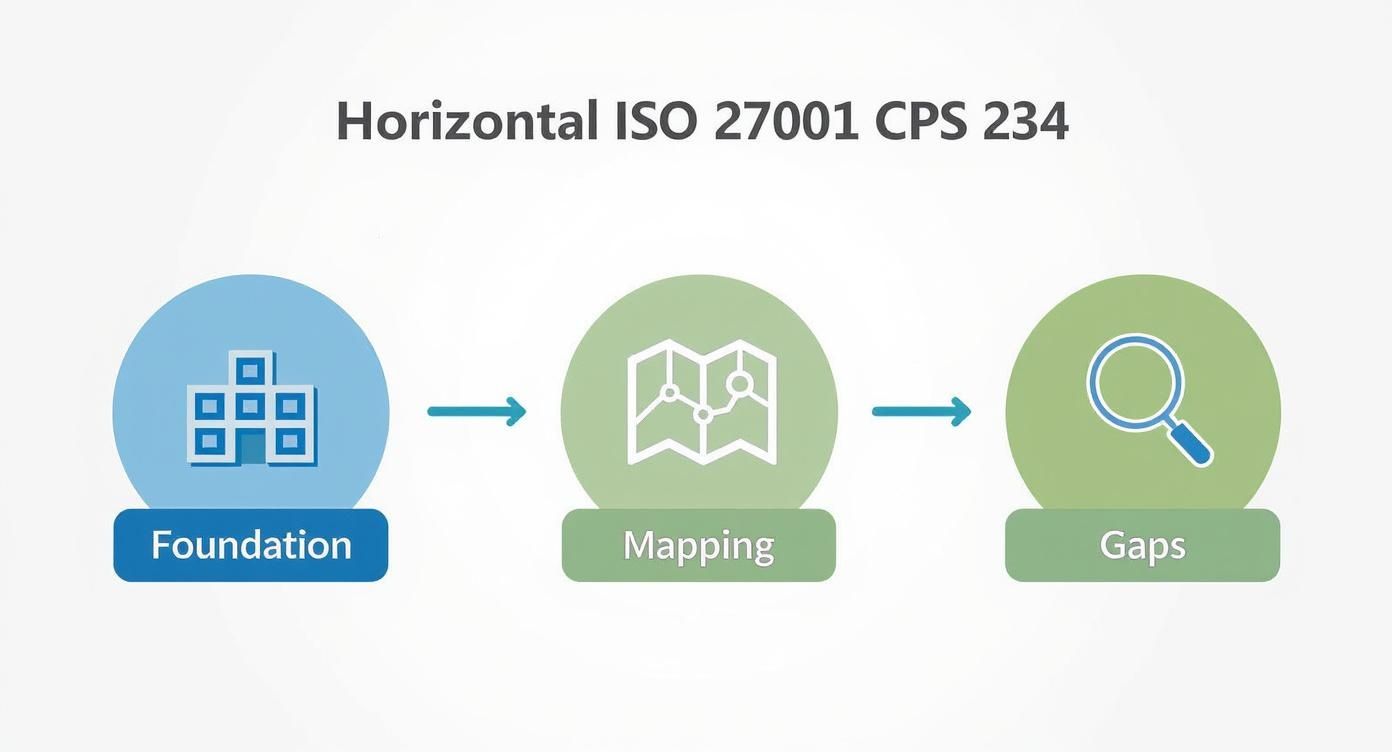
As you can see, starting with a solid foundation (like ISO 27001) lets you strategically map requirements and pour your resources into closing the specific gaps that CPS 234 highlights.
Phase 3: Testing and Reporting
Once your new controls are in place, you have to prove they actually work. Phase 3 is all about validation. It involves rigorous testing to find weaknesses before the bad guys do, sharpening your response plans, and creating a clear reporting line to the Board.
APRA has made it crystal clear they care about outcomes, not just on-paper compliance. This makes the testing phase more important than ever.
Here’s what to focus on:
- Conducting Independent Control Testing: Get skilled, independent specialists to systematically test your security controls. This isn't optional. It must include things like vulnerability assessments and penetration tests to mimic a real-world attack.
- Refining Your Incident Response Plan: A solid incident response plan is a cornerstone of CPS 234. Once you've got one, you need to run drills and tabletop exercises to make sure your team can actually follow it under pressure.
- Establishing Board Reporting Mechanisms: Create clear, simple dashboards and reports to keep the Board updated on your security posture. This reporting has to prove that your controls are effective and that you're meeting your obligations under CPS 234.
- Initiating an Internal Audit Review: Ask your internal audit team to provide an independent review of your security controls. This gives the Board that final layer of assurance that everything is working as it should.
Finishing this three-phase roadmap puts you in a strong, defensible position. But remember, compliance is never "done". This roadmap should become a living cycle of assessment, fixing, and testing to ensure you stay resilient as threats continue to change.
Beyond Compliance: Forging a Truly Resilient Security Culture
It's tempting to breathe a sigh of relief once you’ve ticked off every item on the APRA CPS 234 checklist. Controls are in place, reports are filed—job done, right? Not quite. This is actually one of the most dangerous moments for any organisation. True cyber resilience isn’t a finish line you cross; it’s a culture you build, nurture, and live out every single day.
The critical mindset shift is seeing APRA CPS 234 as the foundation, not the ceiling. The standard gives you the blueprint for a digital fortress, but it’s your people who stand guard on the walls. A genuinely resilient security culture weaves this sense of duty into the very fabric of your organisation.
This means kicking the ‘tick-box’ mentality to the curb and embracing a state of constant improvement. It's about shifting information security from being an "IT problem" to a shared business value that everyone, from the front desk to the boardroom, champions.
From Annual Training to Active Vigilance
Building a human firewall starts with training, but it can't end there. A once-a-year phishing test and a tired slide deck on password policies just won't cut it anymore. To foster real vigilance, your approach to security education has to be continuous, engaging, and genuinely relevant to people's daily work.
You need to create an environment where security is an ongoing conversation.
- Think Beyond the Phishing Test: These are still useful, but they should be one tool in a much larger toolkit. Follow them up by discussing real-world breaches in the news. Explain exactly how the attack succeeded and what your team could have done differently to spot it.
- Create Role-Specific Scenarios: A generic, one-size-fits-all training program is a waste of everyone's time. Your finance team is up against very different threats than your marketing team. Develop tailored training that uses scenarios they would actually face.
- Focus on Positive Reinforcement: Don't just penalise people who click the wrong link. Build a system that rewards and publicly celebrates employees who proactively report suspicious emails or activities. This simple switch turns security from a chore into a collaborative team effort.
When your people understand the 'why' behind a security rule, they’re far more likely to become your most valuable defenders.
Fostering a Culture of Shared Responsibility
A truly resilient culture is one where every single person feels a personal sense of ownership over information security. This is a massive cultural shift, and it has to be driven from the top down and embraced from the bottom up. Security can no longer be seen as someone else's job.
To make this happen, your leadership team must empower employees to be security champions. This means creating a blameless culture where staff feel safe raising their hands to report a mistake. If someone clicks on a malicious link, the first response should always be, "Thanks for letting us know so quickly," not, "How could you do that?"
True resilience is built when your people become your best sensors. A culture of shared responsibility means every employee understands they are a vital part of the organisation's immune system, capable of detecting and flagging threats long before they cause serious harm.
This shift takes more than an email memo. It requires constant communication, clear expectations, and a visible commitment from the leadership team. When the board and C-suite actively discuss security and model the right behaviours, it sends a powerful message that this is a core priority for everyone.
The Board’s Continuing Mission
APRA CPS 234 makes the Board’s accountability crystal clear, but their role has to be more than just oversight. An engaged board doesn't just skim through security reports; it actively challenges assumptions, asks tough questions, and helps steer the organisation's security strategy. They must stay curious and informed.
This kind of active governance ensures cybersecurity gets the strategic focus—and the budget—it needs to keep pace with an ever-changing threat landscape. The conversation in the boardroom has to evolve from "Are we compliant?" to "Are we secure, and what are we doing to get even better?"
At the end of the day, APRA CPS 234 gives you the framework, but your culture is what provides the real resilience. Start treating information security not as a burdensome cost, but as a core business enabler. It's the bedrock that protects your reputation, builds customer trust, and secures your future in a world where digital threats are simply a fact of life.
Got Questions About APRA CPS 234? We've Got Answers.
When a standard like APRA CPS 234 lands on your desk, it’s natural for questions to pop up. It’s one thing to read the official text, but it's another to understand how it actually plays out in the real world.
Let's cut through the jargon and tackle some of the most common questions we hear from businesses trying to get to grips with these requirements.
Does APRA CPS 234 Really Apply to My Small Business?
In a word: yes. If you’re an APRA-regulated entity, you’re on the hook for CPS 234, no matter your size. This includes all authorised deposit-taking institutions (ADIs), insurers (general, life, and private health), and superannuation funds.
But here’s the crucial part: the standard is built on a principle of proportionality. This is a common-sense approach from APRA. They don't expect a small, regional credit union to have the same sprawling, multi-million dollar security setup as one of the big four banks.
What they do expect is a security framework that is fit for purpose. It needs to be robust, clearly documented, and genuinely effective at protecting your members' and customers' data against the threats you actually face. It's about smart security, not just expensive security.
What Exactly Does the Board Need to Do?
Under CPS 234, the Board can’t just delegate and forget. They are ultimately accountable for the organisation's information security. This isn't about being cybersecurity experts; it's about governance and demonstrating active oversight.
So, what does that look like in practice? The Board is expected to:
- Sign off on the organisation's official information security policy.
- Make sure the right controls are in place and, critically, that they are being tested regularly.
- Review reports that show how effective those controls are, including findings from audits and penetration tests.
- Be informed immediately of any significant security incidents.
The goal is to create a clear paper trail showing the Board is engaged. Your meeting minutes should reflect genuine discussion and decision-making on cyber risk, proving it's a priority at the highest level.
What Counts as a "Material" Security Incident?
This is a big one. A "material incident" is any security event that could seriously affect your business or the interests of your customers, policyholders, or members. APRA wants you to define what's "material" for your specific business, but it typically covers things like:
- An attack that knocks out your critical business systems.
- A major breach of sensitive customer information.
- Anything that could threaten the financial health of your organisation.
- An event serious enough that you have to report it to the police or other regulators.
The clock starts ticking the moment you're aware of a material incident. You have just 72 hours to notify APRA. Without a well-drilled incident response plan, that deadline is almost impossible to meet.
Are There Real Penalties for Getting This Wrong?
Absolutely, and they have teeth. APRA isn't just making suggestions. While they often start with warnings and mandating a fix-it plan, they have serious powers to escalate.
Penalties can include:
- Formal Directions: APRA can issue a legally binding order forcing you to take specific actions to fix your security gaps.
- Capital Penalties: In more severe cases, they can force you to hold more regulatory capital, tying up funds until you prove the issues are resolved.
- Disqualification: APRA can have directors and senior managers removed from their positions for failing in their duties.
Beyond the regulatory slap-down, the reputational damage from a public failing can be devastating. Losing customer trust is often a much higher price to pay than any fine. Getting CPS 234 right isn't just about ticking a compliance box—it's about survival.
Trying to map the demands of APRA CPS 234 to an existing framework like ISO 27001 can feel like a puzzle. We specialise in helping Australian businesses cut through the complexity to build security that is not only compliant but genuinely strong. Visit us at https://iso-27001.com.au to see how our experts can help secure your business.
Recent Comments