

Preventing a data breach isn't about ticking boxes. It's about building a proactive defence that weaves together strong technical safeguards, consistent employee training, and a rock-solid incident response plan. You need to shift from a reactive mindset to a strategy that anticipates and neutralises threats before they can do any real damage. This comprehensive guide will walk you through the essential steps, from foundational risk assessments to advanced strategies, ensuring your small or medium-sized enterprise (SME) is prepared for the modern threat landscape. The digital world is fraught with perils, and understanding how to prevent data breaches is not just an IT concern—it's a fundamental business imperative.
Why Data Breach Prevention Is No longer Optional
For Australian small and medium-sized businesses (SMEs), the question has changed. It's no longer if a data breach will happen, but when. The digital economy, while offering unprecedented opportunities for growth and connection, has also opened up new avenues for malicious actors seeking to exploit vulnerabilities for financial gain or disruption. The days of cyber threats being a problem exclusive to large corporations are long gone. In fact, the opposite is now true: SMEs are increasingly in the crosshairs.
The old idea that "we're too small to be a target" is dangerously outdated. Cybercriminals now see SMEs as the perfect mark—you hold valuable data but often have fewer security resources than the big end of town. This perception makes smaller businesses low-hanging fruit for automated, widespread attacks that cast a wide net, looking for any system with a chink in its armour. They understand that a successful breach against an SME can be just as profitable, and often requires far less effort, than targeting a fortified enterprise.
Let’s be clear: a data breach isn't just an IT headache. It's a business catastrophe waiting to unfold. It can grind your operations to a halt, trigger eye-watering fines, and completely shatter the trust you’ve worked so hard to build with your customers. The repercussions extend far beyond the immediate technical cleanup. A breach can lead to prolonged business interruption, loss of competitive advantage if intellectual property is stolen, and a tarnished brand reputation that can take years to rebuild, if it can be rebuilt at all.
The threats come from all angles, from sophisticated external attacks to simple, honest mistakes made by your own team. Understanding this multi-faceted threat landscape is the first step toward building an effective defence. You are not just fighting against shadowy hackers in distant countries; you are also contending with the realities of human fallibility within your own organisation.
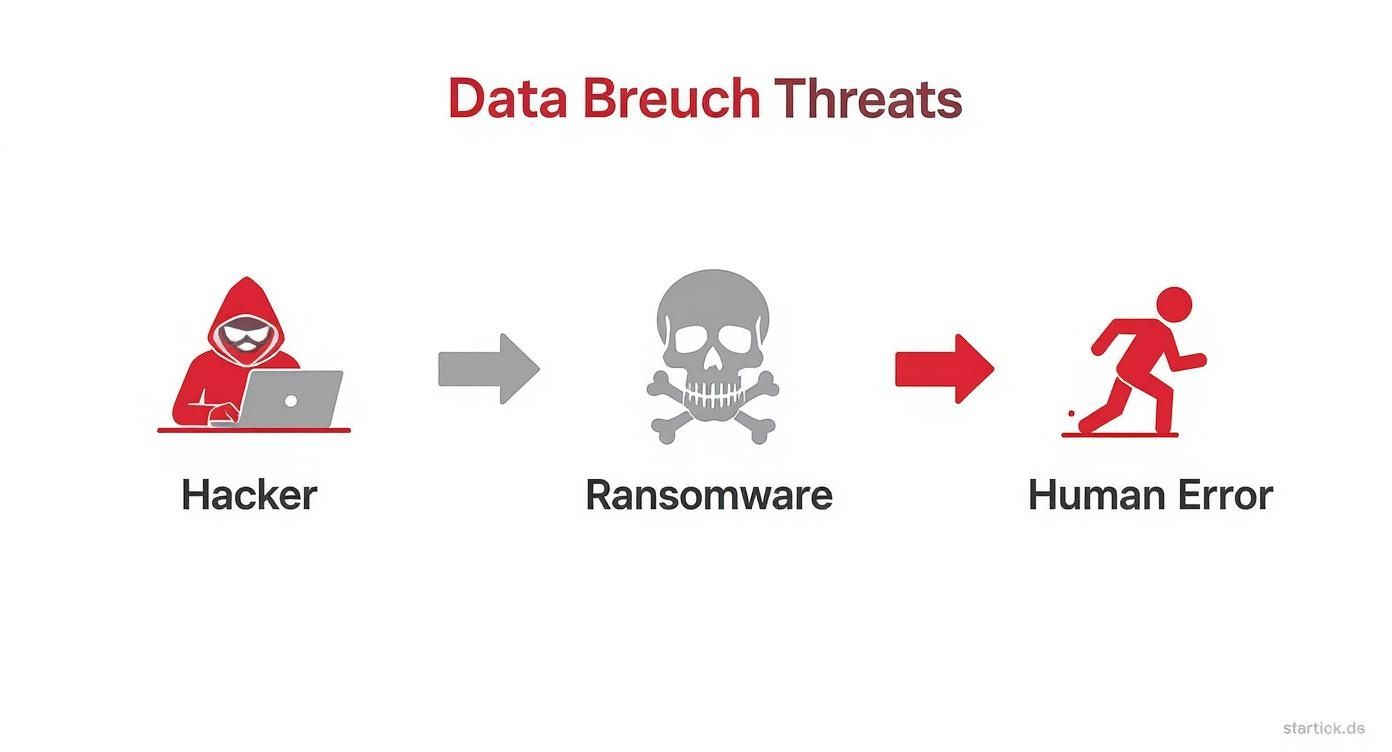
As you can see, you’re up against organised hackers, opportunistic ransomware attacks, and the ever-present risk of human error. This is exactly why you need a defence with multiple layers. A single point of failure is a recipe for disaster. A layered, or "defence-in-depth," strategy ensures that if one security control fails, another is in place to stop or slow down an attacker, giving you more time to detect and respond to the threat.
The Problem Is Getting Worse in Australia
This isn't just fear-mongering; it's a documented, growing problem right here at home. Ever since the Notifiable Data Breaches (NDB) scheme kicked off in 2018, the number of reported incidents has climbed sharply. This legislation mandated that organisations report eligible data breaches to the Office of the Australian Information Commissioner (OAIC) and notify affected individuals, bringing the scale of the problem into the public light.
This is a clear signal that Australian businesses are under immense pressure to protect their information. According to the Office of the Australian Information Commissioner (OAIC), we’re seeing record numbers of breaches, especially in sectors that handle a lot of personal data, like healthcare, finance, legal services, and retail. These sectors are prime targets because the data they hold—medical records, financial details, legal case files—is highly valuable on the dark web and can be used for identity theft, fraud, and other criminal activities.
A data breach is more than just lost files. It’s lost revenue, a lost reputation, and lost time. For a small business, the recovery process can be absolutely devastating, making proactive prevention the only smart move.
The average cost of a breach in Australia is now in the millions—a figure that would send most SMEs to the wall. This financial hit comes from all sides:
- Regulatory Fines: Hefty penalties for not complying with privacy laws. The Privacy Act 1988 allows for significant fines for serious or repeated interferences with privacy, and these penalties are designed to be a strong deterrent.
- Legal Fees: The costs of defending yourself against lawsuits from affected customers. Class-action lawsuits following major data breaches are becoming more common, and the legal costs can be astronomical.
- Remediation Costs: Paying experts to investigate the breach, restore systems, and clean up the mess. This includes forensic investigators, cybersecurity consultants, and public relations firms to manage the reputational fallout.
- Reputational Damage: The long-term, often unquantifiable loss of customers and future business. Trust is a fragile commodity, and once broken, it is incredibly difficult to regain. Customers will take their business to competitors they perceive as more secure.
Getting to Know the Common Attack Methods
To build a decent defence, you have to know what you’re fighting. Cyber attacks aren't always the high-tech operations you see in movies. More often than not, they exploit simple, preventable weaknesses. The vast majority of successful breaches are not the result of a zero-day exploit or a nation-state level attack, but rather a failure of basic security hygiene.
One of the most common culprits is phishing. This is where attackers send deceptive emails to trick your staff into giving up their passwords or downloading malware. These emails are often cleverly disguised to look like they come from a legitimate source, such as a bank, a supplier, or even the CEO of your own company. Another huge one is ransomware, where malicious software locks up all your files, and the criminals demand a massive payment to release them. This can bring an entire business to a standstill, with criminals demanding payment in cryptocurrency to make it harder to trace.
And then there's the persistent issue of human error. This covers everything from an employee using a weak, guessable password to accidentally emailing a sensitive spreadsheet to the wrong person. It can also include misconfiguring a cloud server, leaving sensitive data exposed to the public internet. These aren't malicious acts, but their consequences can be just as severe. The rise in these threats shows why adopting robust frameworks and even understanding SOC 2 compliance is becoming essential for building trust and keeping data safe, especially for businesses that provide services to other companies.
Your First Move: A Practical Risk Assessment
Before you can build a solid defence, you need to know what you're defending and where the enemy might attack. This is exactly what a practical risk assessment does. Forget about drowning in complex spreadsheets or getting lost in technical jargon. At its core, this is about methodically figuring out where your most valuable data is, who can touch it, and what threats could put it in jeopardy. It is a systematic process of identifying, analysing, and evaluating risks to your organisation's information assets.
For any small business, this is the bedrock of a smart, targeted security strategy. It's the step that takes you from guesswork to informed action. Instead of throwing your limited budget at generic security tools, you can pinpoint your resources exactly where they'll make the biggest difference. It’s the difference between blindly firing in the dark and taking a calculated, strategic shot. A well-executed risk assessment allows you to prioritise your security efforts, ensuring that you address the most significant threats to your most critical assets first.
Identifying Your Most Valuable Data Assets
First things first: what are you actually trying to protect? Not all data is created equal. Losing your marketing contact list is an annoyance, but having your entire customer database—complete with financial details—leaked online is a business-ending catastrophe. This process, often called data classification, is fundamental to effective information security.
Your first job is to catalogue your critical data assets. Think about the information that, if stolen, messed with, or lost, would cause the most harm to your operations, reputation, and bottom line. You need to create an inventory of the information you hold, understand its value, and determine its level of sensitivity.
This list will almost always include:
- Personally Identifiable Information (PII): Things like customer names, addresses, phone numbers, and birth dates. This is often regulated by privacy laws, and its loss can trigger mandatory breach notification requirements.
- Financial Data: Credit card numbers, bank account details, and transaction histories. This is highly sought after by criminals for direct financial fraud.
- Intellectual Property (IP): Your unique business processes, proprietary designs, or confidential client files. The theft of IP can erode your competitive advantage.
- Employee Records: Sensitive info like payroll details, tax file numbers, and personal contact information. Protecting this is not only a legal requirement but also crucial for maintaining employee trust.
Once you have this list, you can start to prioritise. This isn't just busywork; it's a foundational step that gives you a clear focus for every security decision you make from here on out. You can apply labels like "Confidential," "Internal," and "Public" to your data to help guide how it should be handled and protected.
Mapping the Flow of Your Data
Now that you know what your key assets are, the next logical step is to understand where this data lives and how it moves around. Data is rarely static. It flows between employees, systems, and even third-party vendors. You need to trace its entire journey to spot the potential weak points. This is known as data flow mapping and is a critical part of understanding your risk exposure.
Start by asking some crucial questions:
- Where is it stored? Is it sitting on a local server in the office, floating in cloud apps like Google Drive or Dropbox, stored on employee laptops, or even tucked away in physical filing cabinets? Each location has its own unique set of risks.
- How is it transferred? Are employees emailing sensitive files, using a dedicated file-sharing service, or accessing data remotely from their home Wi-Fi? Data in transit is often more vulnerable than data at rest if not properly secured.
- Who has access? Which employees, departments, or external contractors can view, change, or delete this data? Access control is a cornerstone of data security.
I can almost guarantee this mapping process will uncover a few surprises. You might find sensitive customer data in an unsecured spreadsheet on someone’s desktop or realise that a former employee still has active accounts for your cloud services. These are the exact vulnerabilities a good risk assessment is designed to bring to light. It provides visibility into practices that may have developed organically over time without proper security consideration.
For a more structured approach, our comprehensive guide on a risk assessment for cyber security offers a deeper framework to help you organise your findings.
A thorough risk assessment isn't an accusation of failure; it's an act of responsible business management. It provides the clarity needed to build a defence that is both effective and affordable, protecting the very core of your business.
Analysing Threats and Vulnerabilities
Okay, it's time to connect the dots between your valuable data and the things that could go wrong. For each critical data asset you’ve identified, start thinking about all the different ways it could be compromised. This means looking at weaknesses in your people, your processes, and your technology. A vulnerability is a weakness that can be exploited, while a threat is the potential for that vulnerability to be exploited. Risk is the intersection of these two concepts.
To guide you, we've put together a simple checklist to get you started on evaluating your current security posture.
Small Business Risk Assessment Checklist
| Assessment Area | Key Questions to Ask | Example Vulnerability |
|---|---|---|
| Data & Assets | Do we know where all our sensitive data is stored? Who has access to it? | Critical customer financial data is stored in an Excel sheet on a shared, unsecured network drive. |
| Access Control | Are we using strong, unique passwords? Is Multi-Factor Authentication (MFA) enabled everywhere possible? | Employees use simple, easily guessable passwords like "Winter2024" for key systems. |
| People & Training | Are staff trained to spot phishing emails? Do they know our data handling policies? | A new employee clicks a malicious link in a fake "urgent invoice" email, compromising their credentials. |
| Software & Systems | Is our software (e.g., WordPress, accounting software) kept up to date with security patches? | The company website is running on an outdated version of a plugin with a known, unpatched vulnerability. |
| Network Security | Is our office Wi-Fi network secured with a strong password? Is it separate from any guest network? | The main office Wi-Fi uses a weak, default password that has never been changed. |
| Physical Security | Are laptops and servers physically secure? What happens if a device is stolen? | An employee's work laptop, containing unencrypted client data, is stolen from their car. |
This checklist is a starting point, not the final word. Every business is different, but thinking through these areas will reveal your most urgent priorities and give you a clear action plan. By systematically evaluating these areas, you move from a vague list of problems to a concrete roadmap detailing exactly where to invest your time and resources.
Right, you’ve mapped out your risks. Now it’s time to get your hands dirty and build the digital fortress that will actually protect your data. This is where we move from planning to doing.
Think of it like securing your home. You don't just lock the front door and hope for the best. You've got window locks, a security alarm, and maybe some cameras. Each layer adds strength, and together, they make your home a much harder target. We're going to apply that same layered thinking to your business's digital security.
Lock It Down With Encryption
One of the most powerful tools in your arsenal is encryption. It essentially scrambles your data into an unreadable mess for anyone who doesn't have the key. If a cybercriminal manages to sneak past your defences and grab a file, all they get is gobbledygook. Encryption is a foundational technology that renders data useless to unauthorised parties.
You need to apply encryption in two key situations:
- Data in Transit: This is your data on the move, like an email being sent or a customer filling out a form on your website. SSL/TLS certificates (the little padlock in the browser bar) are the standard here, and they're non-negotiable. This ensures that any data sent between your customer's browser and your server is protected from eavesdropping.
- Data at Rest: This is your data sitting on a server, a laptop's hard drive, or even a USB stick. Most modern operating systems and cloud platforms have built-in encryption. Your job is to make sure it’s switched on. This is crucial for protecting data in case of physical theft of a device.
Get this right, and a potentially business-ending data theft becomes a minor headache. The thief has the file, but they can’t do a single thing with it.
Make Unauthorised Access a Thing of the Past
Next, let's slam the door on anyone trying to get into your systems who shouldn't be there. Stolen passwords are a dime a dozen online, which is why a simple password just doesn't cut it anymore. Credential theft is one of the most common ways attackers gain initial access to a network.
This is where Multi-Factor Authentication (MFA) comes in, and it’s an absolute must-have. MFA forces anyone logging in to prove their identity with at least two separate pieces of evidence.
If you do one thing from this list, make it MFA. It is the single most effective way to stop an attacker with a stolen password from waltzing right into your most sensitive systems.
It’s simple, really. The first factor is something you know (your password). The second is something you have (like a code from an authenticator app on your phone) or something you are (your fingerprint). A crook might steal your password, but it’s a whole lot harder for them to also steal your phone. This layered approach to authentication dramatically increases the difficulty for an attacker.
You need to enable MFA everywhere you can, especially on:
- Email (Microsoft 365, Google Workspace)
- Cloud storage and accounting software
- Your Customer Relationship Management (CRM) system
Stick to the Principle of Least Privilege
Just because someone has the keys to get in, doesn't mean they should have access to every room in the house. The Principle of Least Privilege (PoLP) is a simple but critical security concept: give people access only to the information and tools they absolutely need to do their job. Nothing more.
Your marketing coordinator doesn't need access to payroll files. Your accountant doesn't need to be able to change website code. By limiting access on a need-to-know basis, you shrink the potential blast radius if an account is ever compromised. The attacker is stuck with only what that one user could see. This containment is crucial for limiting the damage of a breach.
Make a habit of reviewing who has access to what, especially when people change roles or leave the business. It’s simple admin, but it’s a massive security win. Regular access reviews are a key part of maintaining a strong security posture.
Guard Your Network Perimeter
Think of your network as the digital plumbing connecting all your computers, servers, and data. You need a gatekeeper to watch the entry and exit points. That gatekeeper is your firewall.
A good business-grade firewall doesn't just block a bit of traffic; it actively inspects everything coming in and out, blocking anything that looks malicious or breaks the rules you’ve set. It's your first line of defence against probes and attacks from the outside world. Modern firewalls can provide advanced features like intrusion prevention and deep packet inspection.
Take it a step further with network segmentation. This just means splitting your network into smaller, isolated zones. For instance, put your public Wi-Fi on a completely separate network from your internal staff network. That way, if one area is breached, the intruders are walled off and can’t easily jump over to your critical systems. Segmentation helps to contain breaches and prevent lateral movement by attackers.
Keep Your Software Up to Date. Always.
Software vulnerabilities are like unlocked doors just waiting for a burglar. When developers find a security flaw, they release a "patch" to fix it. Attackers are constantly scanning the internet for unpatched systems because they are easy pickings.
This is why a strict patching schedule is non-negotiable. And it’s not just about your operating system. It’s every single piece of software you use—from your accounting package to the plugins running on your company website. A robust patch management program is a fundamental security control.
Turn on automatic updates wherever you can. For everything else, set a recurring calendar reminder to check for and apply security patches weekly. Procrastinating on updates is an open invitation for an attack. Many of these controls are foundational security hygiene, echoing best practices like those in the Australian Cyber Security Centre's framework. To see how these ideas fit into a recognised standard, check out the ACSC Essential Eight.
Your Last Line of Defence: Backups
Let’s be realistic. No defence is perfect. You have to be prepared for the worst-case scenario. A solid, well-tested backup and recovery plan is your ultimate safety net against everything from a ransomware attack to a simple hardware failure.
A great rule of thumb is the 3-2-1 rule:
- Keep at least three copies of your data.
- Store them on two different types of media (e.g., a hard drive and the cloud).
- Make sure one of those copies is stored completely off-site. This off-site copy is critical for recovering from a disaster that affects your primary location, such as a fire, flood, or a ransomware attack that encrypts network-connected backups.
But here’s the most important part: test your backups! Regularly try restoring a few files to make sure the process actually works. An untested backup isn't a plan; it's a prayer. You need to have confidence that you can recover your data when you need it most.
The Human Element in Your Security Strategy
Your technical defences are absolutely crucial, but they’re only half the story. The most sophisticated firewall in the world can be completely undone by a single, convincing phishing email. This is why tackling the human element isn't just a "nice-to-have"—it's a core part of any serious plan to prevent data breaches. People are often described as the weakest link in the security chain, but with the right training and culture, they can become your strongest asset.
Think of your employees as your first and last line of defence. When they're empowered with knowledge and a sense of shared responsibility, they become an incredible security asset. But when they're left untrained, they can unintentionally become your biggest vulnerability. Fostering a security-first culture is all about turning every single team member into a proactive defender of your business's data. It’s about creating an environment where security is everyone's responsibility.
Building a Human Firewall Through Training
Security awareness training isn't a one-off event you just tick off a list. To be effective, it needs to be an ongoing conversation that keeps security front-of-mind for everyone. The real goal is to make safe data handling an instinct, not an afterthought. The threat landscape is constantly evolving, so your training needs to be continuous to keep pace with new attack techniques.
Good training moves beyond dry, technical lectures. It should use real-world examples and interactive sessions to show people what threats actually look like in their daily workflow. A well-trained team is simply far less likely to fall for the common tricks that lead to costly disasters. Engagement is key; if training is seen as a chore, the lessons won't stick.
Let's be honest: human error is a persistent and growing factor in security incidents. A lot of the most damaging breaches we see in Australia stem from ransomware, phishing, and compromised accounts—all attacks that prey on human behaviour. As Australian Information Commissioner Carly Kind recently pointed out, this highlights the need for a combined approach that safeguards systems while also tackling the human factor head-on. You can read more on these trends from the Australian Cyber Security Magazine.
Core Topics for Security Awareness Sessions
Your training program doesn't need to be overly complicated, but it must be consistent and cover the most common threats your team will face. Repetition is what builds good habits. A structured curriculum ensures all essential topics are covered and reinforced over time.
Here’s a look at some of the essential topics you should be covering regularly.
Building a security-aware culture starts with consistent, relevant training. The table below outlines a foundational program to get you started, focusing on high-risk areas that impact every employee.
Effective Security Training Topics for Employees
| Training Topic | Key Learning Outcome | Frequency |
|---|---|---|
| Phishing & Social Engineering | Team members can confidently identify and report suspicious emails, texts, and phone calls. | Quarterly Drills & Annual Refresher |
| Strong Password Management | Everyone understands and uses strong, unique passwords for all business systems, ideally with a password manager. | Onboarding & Annual Refresher |
| Safe Data Handling | Staff know how to correctly handle, store, and dispose of sensitive customer and company information. | Onboarding & As-Needed Updates |
| Remote Work Security | Remote employees follow clear guidelines for securing home networks and company-issued devices. | Onboarding & Annual Refresher |
This framework provides a solid starting point. By focusing on these high-impact areas, you’re directly addressing the most likely ways an attacker will try to get in.
Making Training Stick
The secret to successful training is engagement. A boring presentation will be forgotten the moment it ends. You need to create sessions that are interactive, relevant, and memorable. Adult learning principles tell us that people learn best by doing and by understanding the relevance of the material to their own lives.
Try these practical tips to boost retention and make the lessons land:
- Run Phishing Simulations: Send out safe, simulated phishing emails to your team. This is a brilliant, no-risk way for them to practice spotting fakes, and it gives you valuable insight into who might need a bit of extra coaching. It provides a safe environment to fail and learn.
- Use Real-World Examples: Instead of generic warnings, show them actual examples of recent phishing scams. Break down the red flags—the dodgy sender address, the manufactured sense of urgency, the suspicious link—so they know exactly what to look for.
- Keep it Short and Sweet: People have short attention spans. It’s far more effective to run a focused 20-minute session every quarter than a three-hour marathon once a year. This micro-learning approach helps with retention and makes it easier to fit training into busy schedules.
Your goal is not to turn every employee into a cybersecurity expert. It's to give them the core skills and confidence to spot a threat and know exactly what to do—and who to tell—when they see one.
From Training to Policy
Training teaches the "why" and the "how," but your policies provide the clear, documented rules everyone is expected to follow. Simple, easy-to-understand policies are essential for creating consistency and accountability. Policies codify the expected behaviours and provide a formal basis for enforcement.
And no, your policies don't need to be hundred-page legal documents. In fact, they shouldn't be. They should be clear, concise guides that cover the critical areas of your day-to-day operations. Accessibility and clarity are far more important than length.
Start with these foundational policies:
- Acceptable Use Policy (AUP): This outlines the rules for using company computers, networks, and software. It should cover what is and isn't allowed, like installing unauthorised software or using company devices for personal activities that could introduce risk.
- Remote Work Policy: With so many people working from home, this is non-negotiable. It needs to specify requirements for secure home Wi-Fi, the use of company-provided devices, and how to handle sensitive data when you're not in the office.
- Data Handling Policy: This is where you define what data is considered sensitive and provide clear instructions on how it must be stored, shared, and ultimately destroyed. It removes the guesswork and ensures everyone treats your most valuable information with the care it deserves.
By combining practical, ongoing training with clear, enforceable policies, you transform the human element from your greatest risk into your strongest defensive layer. You start to build a culture where every single person understands their role in protecting the business, creating a collective vigilance that technology alone can never replicate.
What to Do When a Breach Happens Anyway
Let's be realistic. You can have the best defences in the world, but a determined attacker or a simple human error can still slip through. The unfortunate truth is that a breach can still happen. The mantra in cybersecurity is "it's not a matter of if, but when." Therefore, preparation for an incident is just as critical as prevention.
When it does, your response in those first few critical hours will define everything that comes next—the impact on your business, your reputation, and your bottom line. A swift, coordinated, and effective response can significantly mitigate the damage caused by a breach.
This is where a solid, practical Incident Response Plan (IRP) becomes your most valuable asset. It's not just another document to file away; it's your playbook for navigating the chaos. A well-thought-out plan helps your team act decisively, not react with panic, which can dramatically minimise the damage and get you back on your feet faster. It provides a structured approach to a high-stress situation.
Assembling Your Incident Response Team
Long before an incident occurs, you need to know exactly who is doing what. Trying to assign roles in the middle of a crisis is a recipe for disaster. Your first move is to put together a dedicated Incident Response Team, even if it’s just a handful of key people in your small business. This team should be pre-identified, trained, and empowered to act.
Get specific about roles and responsibilities. This isn't about fancy titles; it's about who owns which practical jobs.
- Incident Coordinator: This is your quarterback. They oversee the entire response, manage communication, and have the final say on big decisions. This role requires strong leadership and decision-making skills.
- Technical Lead: This is your hands-on IT expert. They'll be the one diving in to contain the breach, figure out what happened, and get systems back online. They will lead the forensic investigation and remediation efforts.
- Communications Lead: This person handles all messaging, both inside and outside the company. They’ll be updating employees, notifying customers, and dealing with regulators if needed. This role is crucial for managing the reputational impact of the breach.
Everyone on the team needs to know their role inside and out and have the authority to act fast. A clear chain of command is essential to prevent confusion when every second counts. The IRP should also include contact information for all team members and external resources like legal counsel or forensic investigators.
The Core Phases of Incident Response
A strong IRP breaks the whole messy process down into manageable stages. This structure ensures you don’t miss a critical step when the pressure is on. Think of it as your checklist for getting from initial alert to final recovery. Most incident response frameworks follow a similar lifecycle.
Your plan needs to spell out the specific actions for each phase:
- Detection and Analysis: How do you even know you've been breached? What are the first things you check? This is all about confirming you have a genuine incident on your hands and getting a quick handle on how bad it is.
- Containment: Your absolute first priority is to stop the bleeding. This means isolating affected computers or servers from the rest of your network to stop the attacker from digging deeper and causing more damage.
- Eradication: Once you've got the situation contained, it’s time to get the threat out of your environment for good. This could involve removing malware, shutting down compromised accounts, and fixing the vulnerability that let the attacker in.
- Recovery: Now you can start carefully restoring systems and data from clean, trusted backups. The key word here is carefully—you have to be certain you aren't accidentally reintroducing the problem.
- Post-Incident Review: After the dust settles, you have to look back and learn. What went wrong? How can we strengthen our defences to make sure this doesn't happen again? This "lessons learned" phase is critical for continuous improvement.
This structured approach turns a chaotic event into a methodical process. For a deeper dive into building out each of these phases, our guide on crafting a detailed data breach response plan is an excellent resource.
The goal of an Incident Response Plan isn't just to fix a technical glitch. It's about managing the entire crisis—protecting your customers, preserving evidence, and safeguarding the future of your business.
Establishing Clear Communication Protocols
How you communicate during a breach is just as important as how you fix it. Clumsy or delayed communication can shatter customer trust in an instant and create a public relations nightmare. Transparency and timeliness are key.
Your IRP must include a clear communications plan that specifies:
- Who to notify: This list includes staff, customers, regulatory bodies (like the OAIC in Australia), and maybe even law enforcement. The plan should also consider notifying suppliers, partners, and insurance providers.
- When to notify them: Set clear timelines for these notifications based on legal obligations and what’s best for your customers. For example, the NDB scheme has specific timeframes for reporting.
- What to tell them: Prepare some draft messages ahead of time. You want to be clear, honest, and give people helpful advice without causing unnecessary panic. Pre-approved templates can save valuable time during a crisis.
Having these protocols locked in means your Communications Lead can act immediately, ensuring your messaging stays consistent, transparent, and under your control.
The Power of Practice Drills
A plan you’ve never tested is just a piece of paper. The only way to know if your IRP will hold up under real pressure is to practise. Regular drills and tabletop exercises are absolutely non-negotiable. These exercises simulate a breach scenario and allow your team to walk through the response process in a controlled environment.
These simulations don't need to be overwhelming. You can start with a simple discussion: "Okay team, we've just found ransomware on the main server. What are the first three things we do? Who makes the call?" This simple tabletop exercise can reveal significant gaps in your plan.
These drills are invaluable. They:
- Help everyone get comfortable with their roles and the plan's procedures.
- Shine a light on gaps or weak spots in your plan that you can fix before you need it.
- Build the muscle memory and confidence your team needs to perform when it really matters.
By investing time in creating and testing a robust Incident Response Plan, you’re acknowledging that while perfect prevention might be impossible, excellent preparation is entirely within your control. It’s the ultimate safety net that ensures your business can not only survive a data breach but emerge stronger and more resilient.
Moving Forward With Ongoing Vigilance
Getting your initial defences in place is a massive achievement, but cybersecurity isn’t a ‘set and forget’ task. It's a continuous process of learning, adapting, and improving. Your business evolves, and so do the threats—new tactics, scams, and vulnerabilities pop up almost daily. To truly protect your business for the long haul, you need to embed a mindset of ongoing vigilance into your company culture. Security is a journey, not a destination.
This means moving beyond that first big security push. It’s about making security a living, breathing part of your day-to-day operations, not just a box you tick once a year. It’s about constantly questioning your assumptions, pressure-testing your controls, and actively seeking out the latest threat intelligence. A proactive security culture is one of continuous improvement.
Conduct Regular Security Health Checks
One of the best habits you can get into is performing regular security audits and vulnerability assessments. Think of these as a routine check-up for your business's digital health. They give you a clear, objective view of your systems and processes, highlighting weaknesses before an attacker can find them. These activities provide the data needed to make informed decisions about your security investments.
This really breaks down into two key activities:
- Internal Audits: These are the reviews you handle in-house. It could be as simple as a quarterly check to ensure security policies are actually being followed, all your software is patched, and old employee accounts have been properly deactivated.
- External Audits (Penetration Testing): This is where you bring in the pros. You hire a team of ethical hackers to actively try and breach your defences. It's the ultimate stress test, and it provides incredibly valuable, real-world insights into where your security gaps truly are.
Catching these issues early is the whole point. It’s a proactive stance that separates the resilient businesses from the easy targets.
Stay Plugged into Emerging Threats
You can't defend against an enemy you don't know exists. A huge part of staying vigilant is keeping up with the latest cybersecurity trends, scams, and vulnerabilities—especially those targeting Australian businesses. You don’t need to become a cybersecurity guru overnight, but you do need reliable sources of information. Threat intelligence is a critical component of a modern security program.
Here’s where to look:
- The Australian Cyber Security Centre (ACSC): The ACSC is fantastic. They issue timely alerts, practical guides, and advice tailored specifically for Australian organisations.
- Reputable Cybersecurity News Sites: Following a few trusted industry blogs and news outlets will keep you in the loop on new phishing campaigns or major software flaws.
- Your Tech Partners: Don’t ignore those emails from your software vendors or IT provider. They often contain critical security bulletins and patch information.
Staying informed lets you shift from a reactive to a proactive defence. If you read about a new strain of ransomware hitting businesses in your industry, you can immediately double-check your backups and remind your team about suspicious attachments.
This constant feedback loop is what keeps your security strategy relevant and effective against the threats you’re most likely to face.
Adapt Your Defences as Your Business Grows
Your business isn’t static, so why would your security plan be? Every new employee, every new piece of software, and every new service you offer changes your risk profile. The security plan that worked perfectly for a five-person team will be hopelessly outdated by the time you hit fifty. Security must be integrated into your business processes and evolve with them.
True vigilance means constantly reassessing your security as your business evolves. Launching a new cloud-based CRM? It needs to go through your risk assessment process. Onboarding a new batch of staff? They need to be enrolled in security awareness training from day one.
This ensures your security measures scale alongside your success, preventing new gaps from opening up. A critical, and often forgotten, part of this lifecycle is the secure disposal of old IT gear. As you upgrade, ensuring old hard drives and computers are properly sanitised is non-negotiable. This is where you should always obtain Certificates of Destruction, which serve as legally defensible proof that your sensitive company data has been completely and permanently destroyed.
Build a Security A-Team with Strategic Partners
Let's be realistic—most small businesses don't have the resources to manage every facet of cybersecurity in-house. And that’s okay. This is where leaning on strategic partners can be a game-changer. Working with a trusted Managed Service Provider (MSP) or a specialised cybersecurity consultant gives you access to enterprise-grade expertise and tools without the enterprise-grade price tag.
These partnerships can seriously level up your capabilities by:
- Providing 24/7 Monitoring: They can implement and manage sophisticated tools to watch for any suspicious activity across your network, day and night.
- Handling Patch Management: They can take the tedious but critical task of keeping all your systems updated off your plate, ensuring it gets done consistently.
- Offering Expert Guidance: A good partner acts as a trusted advisor, helping you make smart security investments and navigate the complexities of compliance.
Bringing in the right partner transforms your security posture. It shifts from being a reactive, best-effort chore to a proactive, professionally managed business function. This single step can be one of the most powerful moves you make to build lasting resilience, giving you the confidence to focus on what you do best: growing your business.
Got Questions About Preventing Data Breaches? We've Got Answers.
Even with the best plan, you're bound to have questions. Trying to nail down data breach prevention can feel like a moving target, but getting straight answers to common worries is how you make smart, confident decisions for your business.
We've heard them all, so we've put together answers to the questions that pop up most often for Australian small business owners. Our goal is to cut through the jargon and give you practical advice you can use right away.
How Much Security Is "Enough" for a Small Business?
This is the big one, isn't it? It’s easy to get overwhelmed, picturing a security budget the size of a major bank's. Let me put your mind at ease: you don't need it.
For a small business, effective security isn’t about buying every flashy tool on the market. It’s about being strategic. The best approach is to start with the fundamentals that give you the most bang for your buck. Your risk assessment should guide your spending, ensuring you're addressing your biggest risks.
Think of these as your non-negotiables:
- Multi-Factor Authentication (MFA) on every important account. Honestly, this one control is a game-changer for stopping hackers from getting into your systems.
- Regular Software Patching to close the security gaps that criminals love to exploit.
- Reliable Data Backups that you actually test to make sure they work.
- Ongoing Staff Training because your people are your first and best line of defence.
Nail these basics first. You can always layer on more sophisticated tools as you grow, but getting these core controls right will put you streets ahead of most other small businesses.
Is Proper Cybersecurity Going to Break the Bank?
While you can certainly spend a fortune on security, protecting a small business is far more affordable than you probably think. In my experience, some of the most powerful security wins are low-cost or even free. The concept of "return on security investment" is important; focus on controls that provide the greatest risk reduction for the lowest cost.
Take MFA, for instance. Turning it on costs nothing but a bit of time. The same goes for enforcing a strong password policy or teaching your team how to spot a dodgy phishing email. The real cost is in time and attention, not dollars.
Your risk assessment is your roadmap here. Let it show you where your money is best spent.
The most important thing to remember is this: the cost of preventing a breach is a tiny fraction of the cost of cleaning one up. A proactive investment in security is one of the smartest financial decisions you can make, full stop.
Can't We Just Outsource All of This Security Stuff?
Bringing in a Managed Service Provider (MSP) or a security specialist can be a brilliant move. It gives you immediate access to expertise and technology that would be a real headache to manage on your own. It allows you to focus on your core business while leveraging specialist skills.
But—and this is a big but—outsourcing your security operations doesn't mean you can outsource your responsibility. At the end of the day, you are still accountable for protecting your customers' data. This is a critical point often misunderstood. You can delegate the task, but not the ultimate accountability.
If you decide to partner with an MSP, you need to do your homework.
- Grill them on their security practices. How do they protect their systems? A breach of your provider can lead to a breach of your systems.
- Get a contract that clearly spells out who is responsible for what. Service Level Agreements (SLAs) are crucial here.
- Keep the lines of communication wide open with regular check-ins. A good partnership requires ongoing communication and management.
A great security partner works with you, not just for you. They should feel like a trusted advisor who keeps you in the loop and involves you in the big decisions.
What's the Single Biggest Mistake Businesses Make?
Hands down, the biggest mistake is thinking, "we're too small to be a target." That one belief leads to complacency, and complacency is a cybercriminal's best friend. This "security through obscurity" mindset is a fallacy in the digital age.
When a business owner thinks "it won't happen to us," security gets pushed to the bottom of the list. Software updates are ignored, MFA isn't enforced, and training becomes an afterthought. Each little omission is another crack in the wall.
Attackers absolutely love small businesses for this reason. They know many are running on a false sense of security, which makes them the perfect soft targets for automated attacks like phishing and ransomware. The very first step to effective breach prevention is acknowledging that you are a target.
How Often Should We Be Reviewing Our Security?
Cybersecurity is never a "set and forget" task. The threats are constantly changing, and so is your business. It needs regular attention. Security is a continuous process, not a one-time project.
As a rule of thumb, plan for a formal, deep-dive review of your entire security posture at least once a year. This means dusting off your risk assessment, updating your incident response plan, and checking that your policies still make sense.
But some things need to happen far more often.
- Weekly: Check for and install critical software patches. Don't put it off.
- Monthly: Take a look at the access logs for your most sensitive data and systems.
- Quarterly: Run a phishing simulation to keep your team's security senses sharp.
When you build these checks into your normal business rhythm, security stops being an annual chore and becomes a process of continuous improvement. That proactive mindset is what it takes to stay protected long-term.
Ready to move from questions to action? At Anitech, we specialise in helping Australian small businesses implement robust Information Security Management Systems. Our expert consultants can guide you through the complexities of ISO 27001, providing a clear path to certification and a stronger security posture. Secure your business's future today.
Recent Comments