

Let's get one common misconception out of the way right from the start. ISO 31000 isn't a standard you get certified against; there's no shiny plaque for your wall. Instead, think of it as a universal guide—a strategic playbook for managing the uncertainties every business faces. This comprehensive framework, developed by the International Organization for Standardization, provides principles, a framework, and a process for managing risk. It is designed to be applicable to any organization, regardless of its size, activity, or sector. By integrating risk management into governance, strategy, and planning, management, reporting processes, policies, values, and culture, ISO 31000 aims to create and protect value. It improves performance, encourages innovation, and supports the achievement of objectives.
Its real power lies in helping you weave risk management into the very fabric of your organisation, from high-level boardroom strategy right down to day-to-day operational decisions. The standard emphasizes that risk management is an integral part of all organizational activities and should be tailored to the specific context of the organization. It is not a one-size-fits-all solution but a flexible guide that can be adapted to meet the unique needs and objectives of any business. This approach ensures that risk management is not a standalone activity performed by a few specialists, but a core component of how the entire organization operates, making it more resilient and agile in the face of uncertainty.
Decoding ISO 31000: A Strategic Framework
It’s easy to mistake ISO 31000 for a rigid rulebook, but it’s actually the complete opposite. It’s a set of sophisticated guidelines that acts more like a navigation system for your business. The framework is deliberately adaptable, giving you a common language and approach to risk that works for any organisation, no matter its size, industry, or location. This flexibility is one of its greatest strengths, allowing organizations to integrate risk management into their existing processes and systems without requiring a complete overhaul. The standard provides a structure for identifying, analyzing, evaluating, treating, monitoring, and communicating risks in a systematic, transparent, and credible manner.
Here’s an analogy I like to use: a pilot files a flight plan not just to steer clear of storms (threats), but also to catch favourable tailwinds (opportunities). ISO 31000 operates on the same principle. It equips your organisation to make smarter, more informed decisions by understanding the full spectrum of what might happen, good or bad. This proactive approach to risk management allows businesses to not only protect themselves from potential harm but also to identify and capitalize on opportunities that might otherwise be missed. By considering both the positive and negative aspects of uncertainty, organizations can develop a more balanced and strategic approach to achieving their objectives.
A Universal Approach to Uncertainty
At its heart, ISO 31000 encourages a fundamental shift in how we think about risk. It’s not merely about preventing financial losses or avoiding accidents. The standard defines risk as the "effect of uncertainty on objectives." This definition is intentionally broad, encompassing any deviation from the expected, whether positive or negative. It moves the concept of risk beyond the traditional focus on hazards and threats to include opportunities and potential gains.
That’s a crucial distinction. Uncertainty isn't inherently negative; it can just as easily open doors to incredible new opportunities. By adopting this perspective, organizations can foster a culture that is not risk-averse, but risk-aware. This means encouraging employees to take calculated risks that align with the organization's strategic goals and risk appetite. It is about making informed decisions in the face of uncertainty, rather than trying to eliminate uncertainty altogether.
By embracing this mindset, Australian businesses can build genuine resilience. You move beyond simply reacting to disruptions and start proactively turning potential challenges into a real competitive advantage, setting the stage for long-term, sustainable growth. This proactive stance enables organizations to anticipate and prepare for potential disruptions, minimizing their impact and ensuring business continuity. It also allows them to identify and seize opportunities as they arise, giving them a competitive edge in the marketplace.
ISO 31000 provides a flexible skeleton for managing uncertainty. A well-defined enterprise risk management strategy provides the connective tissue, integrating the framework with daily operations to create a system that doesn’t just monitor risk but actively manages it. This integration ensures that risk management becomes a part of the everyday decision-making process, rather than a separate, periodic exercise.
Key Objectives of the Standard
The standard was created to help organisations achieve several key goals, and none of them involve creating more red tape. It’s all about boosting performance and building confidence with your stakeholders. The primary objective is to enable organizations to manage uncertainty effectively, thereby increasing the likelihood of achieving objectives and improving the protection of assets. Before we get into the nitty-gritty, it's worth reviewing the foundational concepts of risk management to make sure you have a solid grasp of the basics. Understanding these fundamentals is crucial for successfully implementing the ISO 31000 framework.
The main aims of an ISO 31000-aligned approach include:
- Enhancing decision-making: By giving you a structured way to weigh up uncertainty, it helps leaders put resources where they’ll have the most impact. This systematic approach ensures that decisions are based on a thorough understanding of the potential risks and opportunities, leading to better outcomes.
- Improving governance and accountability: It makes it crystal clear who is responsible for managing which risks across the business. By defining roles and responsibilities, the standard helps to create a culture of accountability where everyone understands their role in managing risk.
- Boosting operational efficiency: A proactive stance means you can spot potential problems before they blow up, saving you from costly surprises down the track. By identifying and addressing risks early, organizations can prevent disruptions to their operations and reduce the costs associated with reactive problem-solving.
- Building stakeholder trust: When you can demonstrate a mature, considered approach to risk, you give customers, investors, and regulators every reason to have faith in you. This transparency and commitment to responsible risk management can enhance an organization's reputation and strengthen its relationships with key stakeholders.
Not an Island but a Foundation
It’s also critical to see how ISO 31000 fits in with other management system standards. While you can't get certified in ISO 31000 itself, its principles and framework are the bedrock for the risk management activities demanded by other popular ISO certifications. The principles and guidelines of ISO 31000 are designed to be compatible with other management systems, making it easier to integrate risk management into existing frameworks.
Take ISO 27001 for Information Security Management, for example. It relies heavily on a robust risk assessment and treatment process. My clients who have already adopted the principles of ISO 31000 find it significantly easier to meet these specific requirements. The structured approach to risk management provided by ISO 31000 aligns perfectly with the risk-based approach required by ISO 27001, streamlining the implementation and certification process. Similarly, standards like ISO 9001 (Quality Management) and ISO 14001 (Environmental Management) also incorporate risk-based thinking, making ISO 31000 a valuable foundation for a wide range of management systems.
The first step is always to develop a clear plan, and that starts with understanding what you’re already doing well. Exploring what a comprehensive risk management strategy entails will show you how it all connects to these broader certification goals. This foundational work doesn't just streamline compliance; it helps you build a more cohesive and effective management system across your entire business. By aligning your risk management practices with the principles of ISO 31000, you can create a more resilient and successful organization.
The Core Principles That Drive Success
To really get to grips with ISO 31000 risk management, you have to look past the processes and paperwork. You need to understand its philosophical heart—the core principles. These aren't just vague ideas; they are the strategic pillars that hold up a truly resilient and forward-thinking organisation. These principles are the foundation upon which the framework and process are built, and they are essential for effective risk management.
Treating these principles as actionable values, not just buzzwords, is what separates a box-ticking exercise from a genuine competitive advantage. When these principles are embedded in the organization's culture, they guide behavior and decision-making at all levels, ensuring a consistent and effective approach to managing risk.
Think of them as the constitution for your risk management efforts. They’re the guiding beliefs ensuring every decision—from the boardroom to the front line—is consistent, effective, and pulls in the same direction as your business goals. When you weave these principles into your company culture, managing uncertainty becomes second nature for everyone. This cultural shift is crucial for moving beyond a compliance-focused approach to one that truly creates and protects value.
Principle 1: Integrated
First off, and arguably the most important, risk management has to be integrated into everything your organisation does. It can’t be stuck in a silo, managed by a department that only shows up when things go wrong. True integration means risk awareness is part of your company's DNA. This principle emphasizes that risk management is not a separate activity but an inherent part of all organizational processes.
Integrated: Risk management isn’t a stand-alone activity. It’s an essential part of all organisational processes, from governance and strategic planning to day-to-day operations.
Imagine a Melbourne-based retailer planning its stock for the Christmas rush. An integrated approach means the procurement team doesn’t just reorder what sold well last year. They’re actively talking to marketing about upcoming promotions, to logistics about potential supply chain delays from overseas, and to finance about currency fluctuation risks. Risk isn't an afterthought; it's a key factor in the decision-making equation. This holistic view ensures that all relevant factors are considered, leading to more robust and effective plans.
Principle 2: Structured and Comprehensive
Good risk management isn't improvised. It needs a structured and comprehensive approach to make sure risks are identified and handled consistently across the whole business. This systematic method leads to results that are far more efficient, reliable, and repeatable. A structured approach ensures that all significant risks are identified and assessed, and that appropriate treatment measures are implemented.
This principle is your safety net, ensuring no major risks fall through the cracks. For instance, a tech startup in Sydney building a new app would use a consistent risk assessment process for every feature—from data privacy concerns in user logins to potential server crashes during a product launch. This structure gets all your teams speaking the same language when it comes to risk. It also provides a clear and auditable trail of the risk management process, which is essential for governance and accountability.
Principle 3: Customised
While your approach needs structure, the framework itself must be customised to fit your organisation's unique reality. There's no such thing as a one-size-fits-all risk management system. Your strategy has to reflect your specific goals, your culture, and the world you operate in. This principle acknowledges that every organization is different and that its risk management framework must be tailored to its specific context.
Customised: The risk management framework and process are tailored to the organisation’s external and internal context and its objectives.
Think about two very different Australian businesses: a massive mining company in Western Australia and a small organic farm in regional Victoria. The mining company's risk framework will be laser-focused on workplace safety, environmental regulations, and global commodity prices. The organic farm, on the other hand, will customise its framework to tackle risks like climate change hitting crop yields, shifts in local market demand, and staying compliant with organic certifications. Both use ISO 31000 principles, but how they apply them is worlds apart. This customization ensures that the risk management efforts are relevant and effective for the specific organization.
Principle 4: Inclusive
You can’t make the best decisions in a vacuum. The inclusive principle is all about involving the right stakeholders at every level. Getting different perspectives on board ensures you identify and assess risks from all angles, giving you a much clearer and more complete picture. This collaborative approach leads to better-informed decisions and greater buy-in from those involved.
By talking to employees, customers, suppliers, and even regulators, you tap into a massive pool of knowledge. A construction firm in Brisbane, for example, would consult its frontline workers to pinpoint on-the-ground safety hazards. They'd also talk to the local council about zoning rules and to suppliers about potential material shortages. This collaborative approach doesn't just uncover hidden risks; it builds a sense of shared ownership. It ensures that the risk management process is transparent and that the perspectives of all relevant stakeholders are considered.
Principle 5: Dynamic
The world is constantly changing, and so are your risks. An effective risk management process has to be dynamic. That means it's built to anticipate, spot, and respond to changes as they happen. It’s a continuous cycle of scanning the horizon, assessing new information, and tweaking your strategy. This principle emphasizes that risk management is not a one-time event but an ongoing process that must adapt to the changing internal and external environment.
This is absolutely critical for any business navigating rapid change. A financial services company in Australia must constantly adapt its risk framework to deal with new cybersecurity threats, evolving regulations from APRA, and sudden shifts in the market. A static risk register that’s dusted off once a year just won't cut it anymore; your process has to be agile and responsive. A dynamic approach ensures that the organization remains resilient and prepared for whatever the future may hold.
The final three principles anchor your efforts in reality and drive a culture of constant growth.
- Best Available Information: Base your decisions on the best data you can get your hands on—whether that’s historical records, expert opinions, or predictive analysis. This principle ensures that the risk management process is informed and credible.
- Human and Cultural Factors: Never forget that people and culture have a huge impact on how well risk management actually works in practice. This principle acknowledges that risk management is not just a technical process but is also influenced by human behavior and organizational culture.
- Continual Improvement: Your risk management framework isn’t set in stone. It should constantly evolve and get better as you learn from experience. This principle ensures that the risk management process remains effective and relevant over time.
By truly embracing these foundational principles, you turn ISO 31000 risk management from a theoretical exercise into a powerful, practical toolkit. It becomes the engine that not only protects your organisation from harm but also empowers you to seize opportunities with confidence.
Building Your Risk Management Framework
If the principles of ISO 31000 are the ‘why’, then the framework is the ‘how’. This is where the big ideas about managing risk get translated into a concrete, repeatable system that actually works day-to-day. It’s what weaves risk-based thinking into the fabric of your organisation, from the boardroom right down to the front lines. The framework provides the structure and components necessary for implementing risk management throughout the organization.
Think of it like this: the principles are the architectural blueprints for a house—they show what a strong, safe structure should look like. But the framework is the actual foundation, the timber frame, and the roof trusses. It’s the tangible structure that gives the blueprints life and makes the building stand. Without it, the principles are just nice ideas on paper. The framework ensures that the principles are applied consistently and effectively across the organization.
Leadership and Commitment: The Non-Negotiable Starting Point
Let’s get one thing straight. If your leadership team isn't genuinely bought in, your risk management efforts are dead in the water. I’m not talking about just signing off on a policy document; I mean actively championing a culture where spotting and managing risks is everyone’s job. This top-down commitment is essential for creating a risk-aware culture and ensuring that risk management is taken seriously at all levels of the organization.
This is the absolute bedrock of the entire framework. Leaders set the tone for the whole company. They need to integrate risk into strategic planning, put real resources (money, people, and time) behind it, and make it crystal clear who is accountable for what. When your team sees the C-suite constantly asking, "What are the risks here?" and "How are we handling them?", that attitude trickles down fast. This visible support from leadership is crucial for driving engagement and ensuring the long-term success of the risk management program.
True leadership commitment is when risk management stops being a box-ticking chore and becomes a powerful tool for hitting your goals more reliably. It's about recognizing that effective risk management is a key enabler of success, not just a compliance requirement.
From Design to Continual Improvement
Once you have that solid leadership backing, the framework follows a logical lifecycle. Each step builds on the one before it, creating a living system that not only deals with the risks you know about today but also flexes to handle whatever comes next. This structured journey is the heart of a proper ISO 31000 risk management implementation. This cyclical process ensures that the framework remains relevant and effective as the organization and its environment change over time.
A huge blind spot for many businesses is the risk that comes from outside your four walls. Your suppliers, contractors, and partners can open you up to significant threats, which is why a dedicated focus on Third-Party Risk Management (TPRM) is a crucial piece of the puzzle. An effective framework must consider all sources of risk, both internal and external.
The framework’s lifecycle moves through these interconnected stages:
- Integration: Weaving risk management into every important process, project, and decision your business makes. This ensures that risk considerations are a natural part of how the organization operates.
- Design: Crafting a framework that’s a perfect fit for your company’s unique culture, goals, and industry. This customization is key to ensuring the framework is relevant and practical.
- Implementation: Rolling up your sleeves and putting the plan into action across the business. This involves developing the necessary processes, tools, and training to support the framework.
- Evaluation: Stepping back regularly to ask, "Is this working? Is it still right for us?" This monitoring and review process is essential for identifying areas for improvement.
- Improvement: Fine-tuning and adapting the framework based on what you learn and how your business changes. This commitment to continual improvement ensures that the framework remains effective over the long term.
A Practical Blueprint for Your Framework
To help you turn these concepts into a real-world plan, the table below breaks down each component of the framework. It maps out the main goal for each part and the key activities you’ll need to undertake. Think of it as a clear blueprint for any Australian business looking to get this right. This structured approach can help you systematically build and implement a robust risk management framework.
This is much more than a simple checklist; it's your roadmap to building a system that’s both robust and effective. To see how different structures can work in practice, have a read of our detailed guide on various risk management frameworks to find the best approach for your specific needs. Understanding the different options available can help you design a framework that is perfectly suited to your organization.
Components of the ISO 31000 Risk Management Framework
This table breaks down each core component of the ISO 31000 framework, outlining its primary objective and the key activities required for successful implementation.
| Framework Component | Primary Objective | Key Activities |
|---|---|---|
| Leadership & Commitment | To ensure risk management is fully supported and directed from the top of the organisation. | 1. Develop and endorse a formal risk management policy. 2. Assign clear roles, responsibilities, and accountabilities. 3. Allocate sufficient resources. |
| Integration | To embed risk management thinking and processes into all organisational activities. | 1. Incorporate risk criteria into strategic planning and budgeting. 2. Include risk responsibilities in job descriptions. 3. Make risk a standard agenda item. |
| Design | To create a risk management framework that is customised to the organisation’s unique context. | 1. Understand the internal and external context. 2. Define the organisation's risk appetite and criteria. 3. Establish communication and reporting protocols. |
| Implementation | To put the designed framework into effective operation across the entire organisation. | 1. Develop a detailed implementation plan with timelines. 2. Conduct training to build risk management skills. 3. Execute the defined risk management process. |
| Evaluation | To periodically measure the performance and effectiveness of the framework against its goals. | 1. Monitor key performance indicators (KPIs) for risk management. 2. Conduct regular reviews and internal audits. 3. Gather feedback from stakeholders. |
| Improvement | To continuously adapt and enhance the framework to remain relevant and effective over time. | 1. Identify gaps and opportunities from evaluations. 2. Update policies, processes, and controls as needed. 3. Share lessons learned across the organisation. |
This systematic approach isn't just theory; it has been widely adopted across Australia, proving its worth in both the public and private sectors. Since its local introduction as AS/NZS ISO 31000:2009, its influence has only grown. By the time the standard was updated in 2018, it was being formally promoted by Australian government agencies as best practice. In fact, a 2020 information sheet showed that over 90% of major government agencies were using ISO 31000 as the foundation for their risk processes. This widespread adoption demonstrates the value and effectiveness of the standard in a variety of contexts.
By following this structure—starting with committed leadership and moving through a cycle of design, implementation, and constant improvement—you’re not just building a process. You’re building a core business capability that helps you turn uncertainty into opportunity. This capability can provide a significant competitive advantage in today's increasingly volatile and uncertain world.
How to Execute The Risk Management Process
Alright, with a solid framework in place, it’s time to get our hands dirty. The ISO 31000 risk management process is where the rubber meets the road—it’s the practical, step-by-step sequence you’ll follow to actually identify, assess, and handle the uncertainties your business faces. This is the engine room of your entire risk strategy. The process is a systematic application of management policies, procedures, and practices to the activities of communicating, consulting, establishing the context, and identifying, analyzing, evaluating, treating, monitoring, and reviewing risk.
To make this real, let’s follow the journey of a hypothetical Aussie agriculture business, "Drover's Harvest." They're a family-run operation in the Murray-Darling Basin, and they've got their sights set on expanding into the Asian export market. Their story will bring the ISO 31000 risk management process to life. This practical example will help to illustrate how the different stages of the process work in a real-world setting.
This visual captures the essence of a living risk framework—it all starts with leadership, flows into smart design, and is kept alive through constant improvement.
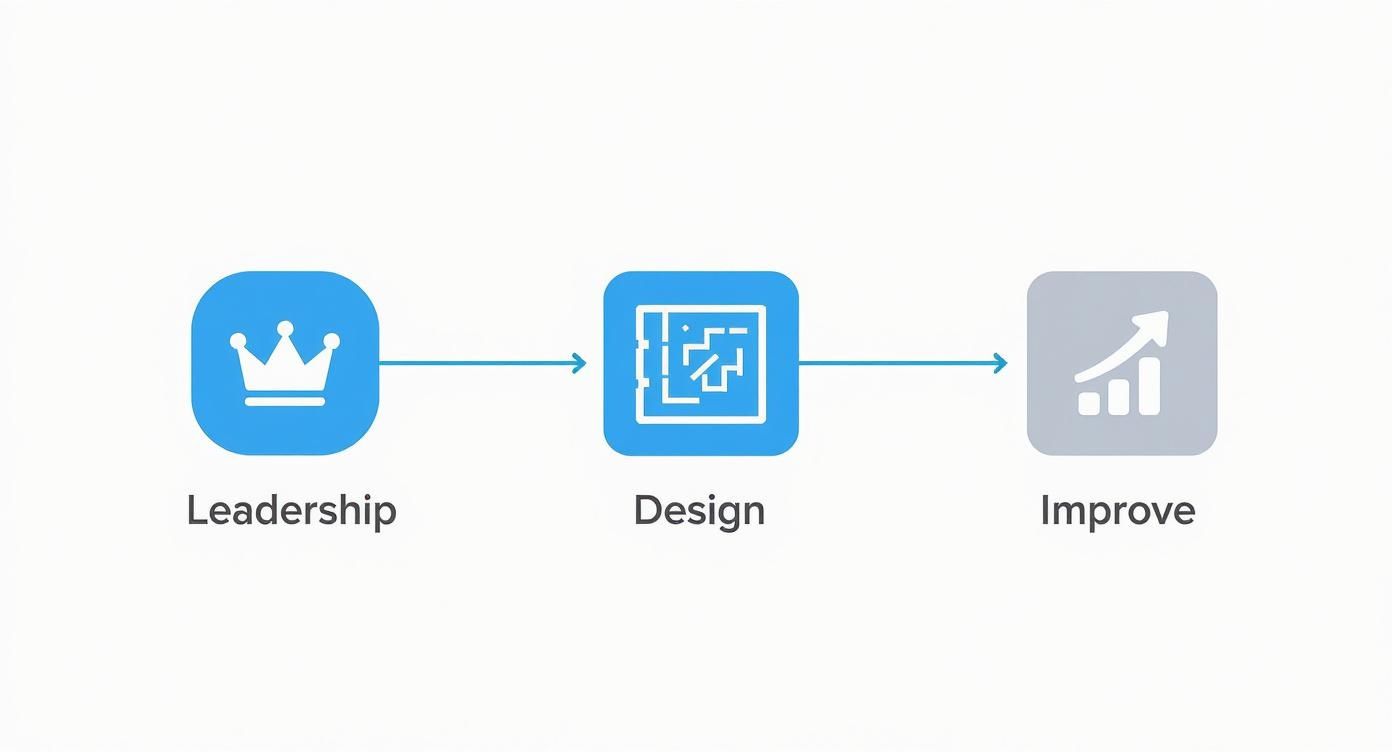
The path from strong leadership to thoughtful design and a genuine commitment to getting better is what makes any risk management process truly work in the long run. These three elements are the pillars that support a successful and sustainable risk management program.
Communication and Consultation
Before you even start listing risks, you need to talk to people. Communication and consultation isn't just another box to tick; it's the constant, two-way conversation that runs through every single stage of the process. Think of it as the oil that keeps the engine running smoothly. This ongoing dialogue ensures that all relevant stakeholders are informed and involved, leading to better decision-making and greater buy-in.
So, why is this so important? Because no one person has a monopoly on the truth. The team on the factory floor, your suppliers, your customers, and even the local community—they all hold vital pieces of the risk puzzle. Bringing them into the conversation not only builds a more complete picture but also creates a culture where everyone feels a sense of ownership. This collaborative approach helps to ensure that the risk management process is comprehensive and well-informed.
For our friends at Drover's Harvest, this looks like:
- Internally: Holding regular catch-ups with farm managers, logistics crew, and the finance team to talk through operational headaches and shifting market prices.
- Externally: Chatting with water authorities about irrigation allowances, talking to international freight companies about shipping reliability, and actually listening to what potential buyers in Asia are saying.
Establishing the Context
You can’t manage risk in a vacuum. The first real step is to establish the context—in other words, understanding the world your business operates in and setting the rules of the game for how you’ll manage risk. This breaks down into two parts. This stage is crucial for ensuring that the risk management process is aligned with the organization's objectives and environment.
First, you map out your external and internal context. This is all about getting your bearings. For Drover's Harvest, this means looking at their market goal (cracking the Asian market), the regulatory landscape (export compliance laws), and their very real exposure to climate events like droughts and floods. Understanding the context helps to identify the key factors that could influence the organization's ability to achieve its objectives.
Second, you establish the risk criteria. This is where you decide, as a business, how much risk you're willing to stomach to achieve your goals. You'll define how you measure risk, which often involves creating a simple matrix of likelihood versus consequence. These criteria provide a basis for evaluating the significance of risks and making decisions about risk treatment.
Establishing the context ensures your risk management efforts are laser-focused on your strategic goals. It answers the big question: "What are we trying to do, and what could get in our way?" This clarity of purpose is essential for effective risk management.
Risk Assessment: The Core Analysis
Once you've set the scene, it's time for the risk assessment. This is the absolute heart of the process, involving three distinct steps that build on each other to give you a deep understanding of what you're up against. Using a structured tool, like a good cybersecurity risk assessment template, can be a brilliant starting point here, even if your risks have nothing to do with IT. The principles of a systematic assessment are universal.
1. Risk Identification
This is the "what if" stage. The goal here is to brainstorm a comprehensive list of anything and everything that could throw a spanner in the works. Don't hold back—think about what could happen, where, when, why, and how. A thorough identification process is essential for ensuring that no significant risks are overlooked.
The team at Drover's Harvest puts their heads together and uncovers a few big ones:
- A severe drought slashing crop yields by over 40%.
- Industrial action at major Aussie ports holding up their shipments.
- A sudden change in import tariffs from their target Asian market.
- A pest infestation wiping out a chunk of their harvest.
2. Risk Analysis
With your list of risks identified, you need to dig a little deeper to understand their true nature. This means figuring out the likelihood of each risk happening and the potential consequences if it does. You can keep it simple with a qualitative scale (low, medium, high) or get more detailed with quantitative figures (like assigning dollar values). The analysis provides a basis for understanding the level of risk and prioritizing risks for further action.
Drover's Harvest looks at the port disruption risk. They figure the likelihood is 'possible' (based on recent news) and the financial hit would be 'major' because of contractual penalties and spoiled produce. This analysis gives them a clear understanding of the potential impact of this risk.
3. Risk Evaluation
The final piece of the assessment is evaluation. This is where you take your analysis and compare it against the risk criteria you defined earlier. This simple comparison immediately helps you prioritise which risks need your attention right now. The evaluation process helps to determine which risks are acceptable and which require treatment.
The criteria at Drover's Harvest say that any risk rated 'high' or 'extreme' needs a formal treatment plan. The port disruption risk, with its 'possible' likelihood and 'major' consequence, lands squarely in the 'high' category. It's officially on the action list. This prioritization ensures that resources are focused on the most significant risks.
Risk Treatment
Risk treatment is all about action. It’s your response to the high-priority risks you’ve just pinpointed. The goal is to choose and implement the best option for dealing with the risk. ISO 31000 gives you a few strategic choices. The selection of a treatment option should be based on a cost-benefit analysis and should consider the organization's risk appetite.
You can decide to:
- Avoid the risk by choosing not to start or continue with the activity causing it.
- Mitigate the risk by taking practical steps to reduce its likelihood or impact.
- Share or transfer the risk to someone else (think insurance policies or specific contract clauses).
- Accept the risk by making an informed decision, usually for minor risks where the cost of treatment is more than the potential damage.
For their top-priority risks, Drover's Harvest decides on a couple of smart treatments:
- Drought Risk (Mitigation): They invest in some seriously clever, water-efficient irrigation technology to become less reliant on mother nature.
- Port Disruption Risk (Sharing & Mitigation): They diversify, building relationships with transport partners at two different major ports. This way, they're not putting all their eggs in one basket.
Monitoring and Review
Last but not least, risk management isn't a "set and forget" exercise; it’s a living, breathing cycle. The world is constantly changing, new risks pop up, and old ones fade away. The monitoring and review stage makes sure your entire risk management process stays relevant and effective. This ongoing process ensures that the organization remains aware of its risk profile and can adapt its risk management activities as needed.
This means regularly checking in on your identified risks, seeing how well your treatment plans are working, and keeping an eye on the horizon for new threats. For Drover's Harvest, this translates to quarterly reviews of their risk register, monthly checks on water allocation forecasts, and keeping a close watch on international trade news. This dynamic approach ensures their ISO 31000 risk management process remains a valuable, strategic part of their business, not just a document gathering dust on a shelf.
Common Implementation Mistakes to Avoid
Learning from others' mistakes is one of the fastest ways to get ahead. While the ISO 31000 risk management standard is a fantastic blueprint, the road to putting it into practice is littered with common traps. Stumbling into one can turn a potent strategic tool into just another bureaucratic headache that adds zero real value. Awareness of these common pitfalls can help organizations navigate the implementation process more effectively.
Dodging these pitfalls is key. It ensures your risk management journey is smooth, strategic, and actually makes your organisation stronger from the get-go. Let's walk through the most common blunders I've seen and, more importantly, how you can sidestep them. By being proactive, you can avoid these mistakes and build a truly effective risk management system.
Treating It as a Compliance Chore
The single biggest mistake you can make is treating risk management as a box-ticking exercise. This is what happens when the goal is simply to "have" a risk register, rather than to genuinely use what you learn from it to make smarter decisions. You end up with a system that looks good on paper but does absolutely nothing in the real world. This compliance-driven approach misses the true value of risk management, which is to improve decision-making and performance.
Think of Company A. They spend ages crafting a detailed risk register. It gets filed away, only to be dusted off once a year for the board meeting. It's a dead document, completely disconnected from the day-to-day grind. For them, risk management is just a task to be completed. This approach is reactive and fails to integrate risk management into the core business processes.
Now, contrast that with Company B. Their risk register is a living, breathing document that gets brought up in weekly team meetings. When they're planning a new product launch, the first question on everyone's lips is, "What are the risks here, and how do we get ahead of them?" They use risk insights to steer their quarterly planning, turning potential threats into a real competitive edge. This proactive and integrated approach is what makes risk management a strategic asset.
To avoid this trap, you have to link every single risk management activity back to a business objective. The question should never be "Are we compliant?" Instead, ask "Is this helping us hit our goals more effectively?" This focus on value creation is the key to successful risk management.
Failing to Secure Genuine Leadership Buy-In
Let's be blunt: without a visible, unwavering commitment from the top, any risk management program is dead on arrival. It will always be seen as a low-priority distraction. When leaders don't actively champion the process, it sends a crystal-clear message to everyone else that it just doesn't matter. This leads to poor engagement, no resources, and ultimately, failure. Leadership commitment is the single most important success factor for any risk management initiative.
A classic sign of this is when a risk manager is appointed but given no real authority or budget. They're tasked with implementing a huge new process but get nothing more than a pat on the back from senior execs. This lack of support undermines the credibility and effectiveness of the risk management function.
To prevent this, leadership has to do more than just sign off on a policy. They need to:
- Actively Participate: Leaders should be the ones kicking off risk discussions in strategic meetings. Their active involvement demonstrates the importance of risk management.
- Allocate Resources: This means putting real money, time, and people behind the initiative. Adequate resources are essential for building and sustaining an effective risk management program.
- Set the Tone: When the boss constantly asks, "What are the risks?", it quickly becomes part of the company's DNA. This creates a culture where risk awareness is a shared responsibility.
Creating Overly Complex Processes
Another common misstep is designing a risk management process so convoluted and academic that no one can actually follow it. Drowning people in confusing jargon, creating multi-page forms for tiny risks, and building overly complex scoring systems just pushes away the very people you need on board. Simplicity and practicality are key to user adoption and engagement.
Imagine asking a busy operations manager to fill out a 15-page risk assessment for a minor tweak to a process. What do you think will happen? They'll either ignore it or tick the boxes with zero thought, making the whole exercise pointless. Complexity is the enemy of adoption. The process should be as simple as possible while still being effective.
Keep it simple, especially when you're starting out. Use plain English. Design tools and templates that feel intuitive and make it easy for people to chip in. Your goal is engagement, not creating a system so perfect that only a risk specialist can understand it. A simple process that everyone actually uses is infinitely more valuable than a "perfect" one that gathers dust.
Communicating Poorly Across the Organisation
Finally, so many implementations fall flat simply because of poor communication. If your team doesn't understand why you're suddenly focused on risk management or what their role is, they can't contribute. Risk management just becomes "someone else's job." Effective communication is essential for building awareness, understanding, and commitment across the organization.
This mistake often looks like a single, company-wide email announcing the new "risk policy," with no follow-up training or discussion. People are left confused, disconnected, and a bit suspicious. A one-off communication is not enough to embed a new way of thinking and working.
The fix is a sustained communication plan. You have to explain the "why" behind your ISO 31000 risk management efforts—how it protects the company, secures jobs, and helps everyone succeed. Use real-world examples that resonate with different departments. When you make the benefits clear and personal, you transform risk management from an abstract corporate mandate into a shared responsibility. This ongoing dialogue is crucial for building a strong risk culture.
So, What Are Your Next Steps Toward ISO 31000 Alignment?
You've got the principles, the framework, and the process down. Now, the ball is in your court. The biggest leap you'll take is moving from simply understanding ISO 31000 risk management to actually doing it. This isn't about ticking boxes for a certificate; it's about weaving a smarter, more forward-thinking approach into the very DNA of your business. The journey to alignment is a practical one that requires commitment and action.
Think of this final section as your playbook for turning knowledge into action. It's a clear, practical guide for any Australian business, big or small, to start aligning with ISO 31000. The whole journey starts with one simple, concrete step. By following these steps, you can begin to build a more resilient and successful organization.
First, Start with a Gap Analysis
Before you start building, you need to know what you’re working with. A gap analysis is basically a health check, where you measure your current way of doing things against the ISO 31000 guidelines. You’ll probably be surprised to find you're already doing a lot of this stuff, even if it's just informally. This assessment provides a baseline for your implementation plan.
It all comes down to asking some honest questions:
- Leadership: Do our leaders actually talk about risk in meetings, or is it just a footnote?
- Process: Do we have a consistent way of spotting what might go wrong, or is it a bit of a free-for-all?
- Culture: Are our people comfortable flagging potential issues, or is there a fear of rocking the boat?
The goal here isn't perfection. It’s about getting a clear, unfiltered look at your strengths and where you need to improve. This baseline assessment will become the foundation for your entire plan, making sure you put your efforts where they'll make the biggest difference. It helps you to prioritize your actions and focus on the areas that need the most attention.
Get Your Leadership On Board
Once you have your gap analysis, your next job is to get genuine, enthusiastic buy-in from the top. This is more than a quick chat in the hallway. You need to build a rock-solid business case that directly links good risk management to hitting your company's big goals. This business case should clearly articulate the benefits of adopting a structured approach to risk management.
Frame the conversation around value, not just compliance. Show them how an ISO 31000 risk management approach helps the business:
- Make smarter investment decisions by truly understanding the potential wins and losses.
- Protect its reputation by getting ahead of operational and strategic threats.
- Work more efficiently by catching small problems before they balloon into expensive disasters.
Getting leadership to champion this is the single most important factor for success. It shifts risk management from a side-project into a core part of your strategy, driven from the very top. This top-down support is essential for driving the necessary cultural and process changes.
Develop a Plan That Fits Your Business
Alright, it’s time to draw the map. Your implementation plan should be a practical, step-by-step guide that’s built for your business, not some generic template. Don’t try to do everything at once. Start small, aim for some early wins, and build momentum from there. A phased approach can make the implementation process more manageable and increase the likelihood of success.
A simple, phased plan might look something like this:
- Phase 1 (The Groundwork): Formally adopt a risk management policy. Get it in writing and assign clear roles so everyone knows who’s responsible for what.
- Phase 2 (The Test Run): Pick a single, important project or department and apply the risk assessment process to it. See what works and what doesn’t.
- Phase 3 (The Rollout): Take what you learned from the pilot and start rolling the process out across other key areas of the business.
- Phase 4 (Making It Stick): Start weaving risk conversations into your regular strategic planning meetings and performance reviews.
Roll Out Training That Actually Helps
A framework is useless if your people don't know how to use it. Your team needs to get the 'why' behind all this and understand the part they play. Targeted training is key to getting everyone speaking the same language and building real capability around risk. This training should be tailored to the specific roles and responsibilities of different employees.
This doesn't have to be a week-long offsite. Think short, punchy workshops focused on practical skills, like how to spot risks in their day-to-day work or how to use a simple risk matrix. When you empower your employees like this, they stop being bystanders and become active players in making the company stronger. This bottom-up engagement is crucial for building a strong risk culture.
Here’s the real kicker: getting aligned with ISO 31000 makes achieving other formal certifications so much easier down the track. A solid risk management foundation is a non-negotiable for standards like ISO 27001 (Information Security) or ISO 45001 (Health & Safety). By laying these foundations now, you’re not just building resilience—you’re setting your business up for future growth and success.
Your ISO 31000 Questions, Answered
As you start exploring ISO standards, a few questions always pop up. It's completely normal. While the big picture of ISO 31000 risk management makes sense, the real-world application is where the details matter. So, let’s clear up some of the most common queries I hear from business owners. Addressing these common questions can help to demystify the standard and facilitate its adoption.
Think of this as our Q&A session. You've got the foundational knowledge; now we’ll lock in the practicalities so you can move forward with genuine confidence. These answers will provide you with the clarity you need to take the next steps on your risk management journey.
Is ISO 31000 a Certification Standard?
This is probably the biggest point of confusion, so let's get it straight: No, you can't get "certified" in ISO 31000. It's not that kind of standard. This is a fundamental distinction that is important to understand from the outset.
Unlike its cousins, ISO 27001 for Information Security or ISO 9001 for Quality Management, ISO 31000 is a set of guidelines. It provides internationally recognised principles and a best-practice framework that any organisation, big or small, can use to get better at making decisions. The entire focus is on building a strong, internal capability for managing risk, not on passing an external audit just to get a certificate for the wall. The value lies in the implementation and integration of the standard, not in the certification itself.
The true win from adopting ISO 31000 isn't a piece of paper. It's about becoming a more resilient business that can handle uncertainty and jump on opportunities. You're building muscle, not just ticking a box. This focus on internal capability is what makes ISO 31000 so powerful.
How Does ISO 31000 Apply to a Small Business?
The beauty of ISO 31000 is that it scales perfectly. This makes it a fantastic tool for small businesses, not a burden. Forget the idea of a huge, stuffy risk management department—that's not what this is about. You simply apply the principles in a way that fits your size and complexity. The flexibility of the standard allows it to be adapted to the specific needs and resources of any organization.
For a small business, ISO 31000 risk management can look incredibly practical.
- Leadership and Commitment: This could be as simple as the business owner making risk a regular five-minute topic in team meetings.
- Risk Assessment: Forget complex software. Grab a whiteboard in a team workshop and brainstorm key threats (like losing a major client) and opportunities (like a new market opening up).
- Risk Treatment: The solutions are often straightforward, like diversifying your customer base so you're not reliant on one client, or cross-training a couple of staff members on critical tasks.
By adopting this way of thinking, a small business can be much smarter about where it puts its time and money. It gives you a structured way to handle potential roadblocks and spot chances for growth, which is a massive competitive edge. This proactive approach can help small businesses to navigate the challenges of the modern business environment more effectively.
What Is the Difference Between Risk Management and Risk Assessment?
It’s easy to mix these two up, but they operate on different levels. Think of risk management as the whole game plan. It's the big picture—the entire system you build, including the framework, your leadership's commitment, how you communicate, and the ongoing cycle of review and improvement. It is the overall process of identifying, assessing, and controlling threats to an organization's capital and earnings.
A risk assessment, on the other hand, is a specific and crucial play within that game plan. It’s the analytical engine at the heart of the system. It breaks down into three key steps:
- Risk Identification: Simply asking, "What could happen that might help or hinder our goals?"
- Risk Analysis: Figuring out how likely each of those things is to happen and what the impact would be.
- Risk Evaluation: Looking at the results of your analysis and deciding which risks need your attention first.
So, in short: you run a risk assessment as one of the most important parts of your overall risk management program. One is a vital process; the other is the entire system that makes it work. Understanding this distinction is key to implementing a comprehensive and effective risk management system.
How Does ISO 31000 Support Business Growth?
Most people hear "risk management" and immediately think defence—stopping bad things from happening. But ISO 31000 is just as much about playing offence. The standard defines risk as the "effect of uncertainty on objectives," and uncertainty can be a good thing. This broader definition of risk encourages organizations to consider both the upside and downside of uncertainty.
When you start systematically looking for and analysing uncertainties, you naturally uncover opportunities. A proper risk assessment might shine a light on a competitor’s weakness you can exploit, an untapped customer group, or a chance to innovate your services. It shifts the entire conversation from "What could go wrong?" to "What do we need to get right to win?" This focus on opportunity is a key differentiator of the ISO 31000 approach.
Proper ISO 31000 risk management gives you the clarity to take smart, calculated risks. It helps you pour resources into the ventures with the highest potential and builds the resilience you need to chase ambitious goals. It’s how you turn uncertainty from something to fear into your greatest strategic asset. By embracing this approach, organizations can not only protect themselves from harm but also create a platform for sustainable growth and success.
Ready to build a more resilient and competitive business? At Anitech, we specialise in helping Australian small businesses navigate the complexities of ISO standards. Our expert consultants can simplify your journey towards robust information security and risk management, making certification achievable. Strengthen your security posture by visiting us at iso-27001.com.au.
Recent Comments