

Quick Summary: An IT security policy is a vital blueprint for your business's cyber defence, not just compliance paperwork. This guide explains how to create a robust policy covering acceptable use, access control, data classification, and incident response, aligning it with ISO 27001 standards and embedding it into your company culture.
Let's be honest: when you hear "IT security policy," you probably think of a dusty binder on a shelf, something you create once to tick a compliance box and then forget about. That mindset is a dangerous liability.
In a world where cyber threats are becoming more common and more sophisticated, your IT security policy is far more than paperwork. It's the strategic blueprint for your company's entire defence system. It’s a living document that guides everything from how your team handles data to the technical controls you put in place to keep attackers out.
Don't Just Tick the Box—Build Your Shield
Thinking of your policy as a mere formality is a critical mistake. A well-crafted, actively used IT security policy is one of the most powerful tools you have to reduce risk and build a security-conscious culture. It takes the vague idea of "being secure" and turns it into clear, practical rules that everyone in your business can understand and follow.
Ultimately, this document is your first line of defence. It sets clear expectations for how your team should handle sensitive information, use company devices, and react if they spot something suspicious. Without it, you're just hoping for the best, leaving your business wide open.
The Reality of Cyber Threats for Australian Businesses
The digital world is a minefield, especially for Australian businesses. The latest statistics paint a pretty grim picture.
During the 2024-2025 financial year, the Australian Cyber Security Centre (ACSC) had to jump in on over 1,200 serious cyber security incidents. That's an 11% increase from the year before. On top of that, they sent out more than 1,700 warnings to organisations about potential attacks—a massive 83% jump. These aren't just numbers; they represent real businesses facing real threats.
And don't make the mistake of thinking this is only a "big company" problem. Hackers often go after smaller businesses precisely because they assume their defences are weaker.
A good policy isn't about tying your team's hands; it's about protecting the business they work for. It gives everyone a clear framework to make smart, secure decisions, effectively turning your whole team into a human firewall.
Why You Need to Be Proactive, Not Reactive
Waiting for a breach to happen before you get serious about security is a recipe for disaster. The cost of a single incident—both in dollars and in damage to your reputation—can be crippling for a small business. A solid IT security policy lets you get on the front foot.
Here’s what a proactive approach gives you:
- Clarity in Chaos: It removes the guesswork by clearly defining rules for using technology, handling data, and responding to incidents. No more ambiguity.
- A Consistent Defence: It ensures security isn't an afterthought. The same strong measures are applied everywhere in the business, closing gaps attackers love to exploit.
- Staying on the Right Side of the Law: It’s your proof that you’re meeting legal duties, like those under the Privacy Act, and adhering to industry standards.
- Building Client Trust: Showing you take security seriously isn't just good practice; it's a competitive advantage. It tells clients and partners that their data is safe with you.
Your security policy is the foundation of your entire defence. To see how this foundation supports a wider defence strategy, it's worth exploring comprehensive cyber security solutions that bring your policy to life. By setting down these clear rules, you build a more resilient business that can confidently face the threats of today and tomorrow.
Building the Foundational Pillars of Your Policy
Don't think of your IT security policy as one massive, scary document. It’s much more like a structure built on a few solid, interconnected pillars. Each pillar tackles a specific area of risk, and when they stand together, they create a formidable defence for your business. The trouble is, if you skip even one, you're leaving a gaping hole for attackers to walk right through.
Breaking it down this way makes the whole process feel so much more achievable. Let's walk through the essential pillars you need to construct, and I'll give you some practical advice for making each one work for your specific business.
Acceptable Use Policy (AUP)
This is your ground-rules pillar. An Acceptable Use Policy (AUP) spells out exactly what your team can and can’t do with company technology and data. It’s all about setting clear expectations to stop accidental breaches and misuse before they happen.
A solid AUP needs to cover:
- Email and Comms: Strictly forbid sending sensitive company data to personal email addresses and set the standard for professional communication.
- Internet Usage: Make it clear that company networks are not for illegal activities, dodgy websites, or so much personal browsing that work grinds to a halt.
- Software Installation: This is a big one. Restrict employees from installing unapproved software—a classic entry point for malware. Every piece of software must be vetted and approved by IT.
- Social Media: Lay down the law on how employees represent the business online and warn them about accidentally sharing confidential info.
For example, a simple but powerful AUP statement could be: "Employees are prohibited from connecting personal, unmanaged devices such as USB drives to the company network without prior approval from the IT department." A single rule like this can shut down a major source of malware infections.
Access Control Policy
This pillar is built on a non-negotiable security concept: the principle of least privilege. All it means is that people should only have access to the exact data and systems they need to do their job—and not an ounce more.
Giving everyone too much access is a disaster waiting to happen. If an employee with the keys to the kingdom clicks a phishing link, the attacker instantly gets a master key. A strong access control policy dramatically limits the damage from any single compromised account.
Your policy needs to be firm: "User access rights will be reviewed quarterly and immediately upon any change in job role or employment status. All access will be granted based on the principle of least privilege required for the employee's designated responsibilities."
This stops access permissions from slowly building up over time, a common problem we call "privilege creep." A crucial part of this is doing regular risk assessments to figure out where your most sensitive data lives. If you're not sure how to get started, this cybersecurity risk assessment template is a great guide to building a solid framework.
Data Classification Policy
Let's be honest, not all data is created equal. Your customers' financial details are infinitely more sensitive than your public marketing brochures. A data classification policy helps your team understand this difference by sorting information into categories based on how sensitive it is.
A simple three-tier system works beautifully for most small businesses:
- Public: Info that can be shared freely without any risk (e.g., press releases, website content).
- Internal: Data for day-to-day business that would cause minimal damage if it got out (e.g., project plans, internal memos).
- Confidential/Restricted: The crown jewels. Highly sensitive data that could cause serious financial or reputational harm if compromised (e.g., customer personal info, financial records, intellectual property).
Once you've classified your data, you can then attach specific handling rules. For example, 'Confidential' data must always be encrypted, can never be stored on portable devices, and can only be seen by specifically authorised people.
Incident Response Plan
It's no longer a question of if a security incident will happen, but when. This pillar is your game plan for that moment. A clear, well-rehearsed Incident Response Plan (IRP) is what separates a minor hiccup from a full-blown catastrophe.
Your IRP has to detail:
- Who to Call: A clear chain of command and contact list for your response team. No one should be scrambling for phone numbers during a crisis.
- What to Do First: Immediate actions to contain the breach, like yanking affected systems off the network.
- How to Investigate: Proper procedures for preserving evidence and figuring out the scope of the incident.
- When to Communicate: Clear guidelines on who to notify and when—including management, lawyers, and potentially customers and regulators.
Password Management Policy
Weak and reused passwords are the low-hanging fruit for hackers. This policy pillar enforces strong password hygiene across your entire organisation, making that easy entry point much, much harder to breach.
Your key requirements should include:
- Complexity: Insist on a minimum length (I recommend at least 12 characters) and a mix of uppercase, lowercase, numbers, and symbols.
- Uniqueness: Outright ban the reuse of passwords across different systems.
- Multi-Factor Authentication (MFA): This is non-negotiable. Require MFA for all critical systems, especially anything with sensitive data or remote access. It's your single most effective defence against password theft.
- Storage: Explicitly forbid writing passwords on sticky notes or saving them in unsecured spreadsheets. Get your team using a company-approved password manager.
Aligning Your Policy with ISO 27001 Standards
The thought of ISO 27001 certification can feel intimidating, I get it. But here’s the thing: it’s not about starting from scratch. It's about taking the smart security work you’re already doing and organising it into a globally recognised framework. Your IT security policy is the heart of this entire process.
Think of your policy as the central piece of evidence you’ll show an auditor. It’s the formal, management-backed document that proves your commitment to information security isn't just talk. Aligning with ISO 27001 elevates your internal rules into a full-blown Information Security Management System (ISMS), transforming your policy from a company handbook into a powerful tool for building client trust.
Connecting Policy to Key ISO 27001 Controls
The link between your day-to-day policy and the ISO 27001 standard is incredibly direct. Many of the core requirements, which they call 'controls', are actually satisfied by the rules you’ve already set. It's all about mapping what you do to what the standard asks for.
Let’s break down how your policy pillars line up with some of the big-ticket ISO 27001 controls:
- Risk Assessment (A.12.1.2): At its core, ISO 27001 is all about managing risk. Your policy needs a clear statement committing the business to regularly finding, analysing, and dealing with security risks. This sentence is the formal foundation for your entire risk management program.
- Asset Management (A.8): Remember that Data Classification Policy we talked about? That directly ticks this box. By creating categories like 'Confidential' or 'Internal' and setting handling rules, you're building the "inventory of information assets" the standard demands.
- Access Control (A.9): The Access Control Policy you built, especially the parts about the principle of least privilege, directly covers this whole family of controls. It’s the documented proof that you’re serious about managing who gets to see and touch your data.
Crafting Policy Language for Auditors
When an auditor sits down with your documents, they’re looking for absolute clarity. They need to see intent and enforcement in black and white. Vague statements won’t cut it; your policy language needs to be direct, actionable, and leave zero room for guessing.
This is especially true for today's common business situations.
For example, instead of something generic, get specific:
- For Remote Work: "All staff connecting to company systems from outside the corporate network must use the company-provided VPN. Any personal devices used for work must be enrolled in our Mobile Device Management system and have device-level encryption and approved anti-malware software enabled."
- For Third-Party Vendors: "Prior to engagement, all third-party vendors who will access company data must complete our security assessment questionnaire. All contracts must contain a security exhibit requiring vendors to meet our data protection standards and notify us of any security incidents within 24 hours."
Embedding ISO 27001 principles into your policy isn't just about passing an audit. It’s about making your security posture genuinely stronger. It forces you to connect every rule to a real-world purpose and a measurable outcome.
Practical Steps for Alignment
Getting your IT security policy aligned with ISO 27001 is more of a mapping exercise than a complete rewrite. You’re looking at what you have, comparing it to the standard's requirements, and then filling in the gaps.
For example, as you firm up your server security rules, a detailed VPS Hosting Security Checklist can be a fantastic guide to ensure your configurations are up to snuff.
The process is simple: go through each clause of the standard and ask yourself, "Where in my existing policy do I cover this?" You'll often find the spirit of the rule is already there; it just needs to be stated more formally. To get a handle on all the requirements, it's worth digging into the complete list of ISO 27001 controls to see how they apply to your operations. This isn't just about compliance; it's a real-world security upgrade.
Defining Clear Roles for Security Accountability
An IT security policy is just a piece of paper until you put people in charge of it. Honestly, you could write the most brilliant, comprehensive security rules imaginable, but they’re completely useless if no one is actually responsible for making them happen. This is a classic trap I've seen countless businesses fall into: they get the "what" perfect but completely forget about the "who."
True success comes from weaving accountability right into the fabric of your company culture. It's about turning that static document into a living, breathing framework that your team actively uses and champions.
Without clear ownership, things just don't get done. Who's in charge of checking user access rights every few months? Who jumps into action when a security incident is flagged? If the answer is a vague "everyone," you can bet it will actually be no one. By assigning specific security duties, you kill the confusion and build a culture where security is a shared, yet clearly delegated, responsibility.
This doesn't mean you need to go out and hire a dedicated security team, especially when you're running a small business. It's simply about assigning security-related functions to the people you already have, making sure every crucial part of your policy has a name next to it.
Establishing a Clear Chain of Command
Accountability has to flow from the top down. When your team sees that the leadership is genuinely invested in security, they get the message loud and clear—this isn't just another box-ticking exercise. This structure makes it obvious who makes the big decisions, who implements them, and who's responsible for the day-to-day stuff.
A simple, three-tiered structure often works best:
- Executive Sponsor: This is your CEO, business owner, or a senior manager. Their job is to give the policy its authority, officially sign off on it, and make sure it has the resources it needs (like a budget for security tools or time for training). Their visible support is absolutely non-negotiable.
- Security Officer/Coordinator: Don't get hung up on the title. In a small business, this could be your IT manager, an office manager, or even just a tech-savvy employee who’s keen to take it on. This person is your on-the-ground security champion. They oversee implementation, organise training, and are the first port of call for any security questions.
- All Employees: Every single person on your team has a part to play. Their responsibility is to understand and follow the rules—like using strong passwords and reporting suspicious emails—and to actively participate in security awareness training.
Assigning Specific Security Responsibilities
Broad roles are a great starting point, but genuine accountability comes from assigning specific, tangible tasks. The person you’ve designated as the Security Officer, for instance, would own a list of duties that bring your it security policy to life.
Think about assigning concrete responsibilities like these:
- User Access Reviews: Someone needs to be tasked with doing a quarterly review of all user accounts, making sure permissions are locked down to only what's necessary for each person's job.
- Incident Reporting: Define a single point of contact for reporting potential security incidents. That person is then responsible for kicking off the first steps of your Incident Response Plan.
- Security Awareness Training: Put someone in charge of scheduling and tracking participation in annual security training and regular phishing tests.
- Vendor Security Vetting: When you're about to sign up for a new piece of software, one person should be responsible for running through a security checklist to make sure the vendor meets your standards.
The current threat landscape makes this kind of clarity non-negotiable. Australia's cyber threat environment saw a staggering 47 million data breaches in 2024, and phishing attacks targeting employees actually doubled, thanks to sophisticated AI-driven tactics. With Business Email Compromise (BEC) being the number one incident type and 75% of them bypassing multi-factor authentication (MFA), having clearly defined roles is what makes the difference. It ensures your policies mandating vital security controls and training are actually enforced. You can explore more about Australia's threat environment to really understand the risks.
A policy without named owners is an orphan document. By assigning roles—from the CEO who signs it off to the employee who reports a phishing email—you create a human infrastructure that gives your policy purpose and power.
This approach transforms your policy from a theoretical document gathering digital dust into a practical, operational guide. When every key security function has a name next to it, accountability becomes ingrained in your operations, dramatically strengthening your defence against the threats you'll face in the real world.
Bringing Your IT Security Policy to Life
You’ve done the hard work of creating a solid IT security policy. That’s a huge step, but the document itself is just the starting point. A policy gathering dust in a shared drive is completely useless. The real challenge—and where you’ll see the payoff—is turning those words on a page into a living, breathing part of your company culture. This is how you build a genuine security posture that actively defends your business day in, day out.
Think of it less as a one-time launch and more as a continuous effort. It's about clear communication, consistent training, and weaving security into the very fabric of your daily operations. This is the difference between simply having a policy and truly being secure.
This chart breaks down how security responsibility flows through a typical business, from the top down.
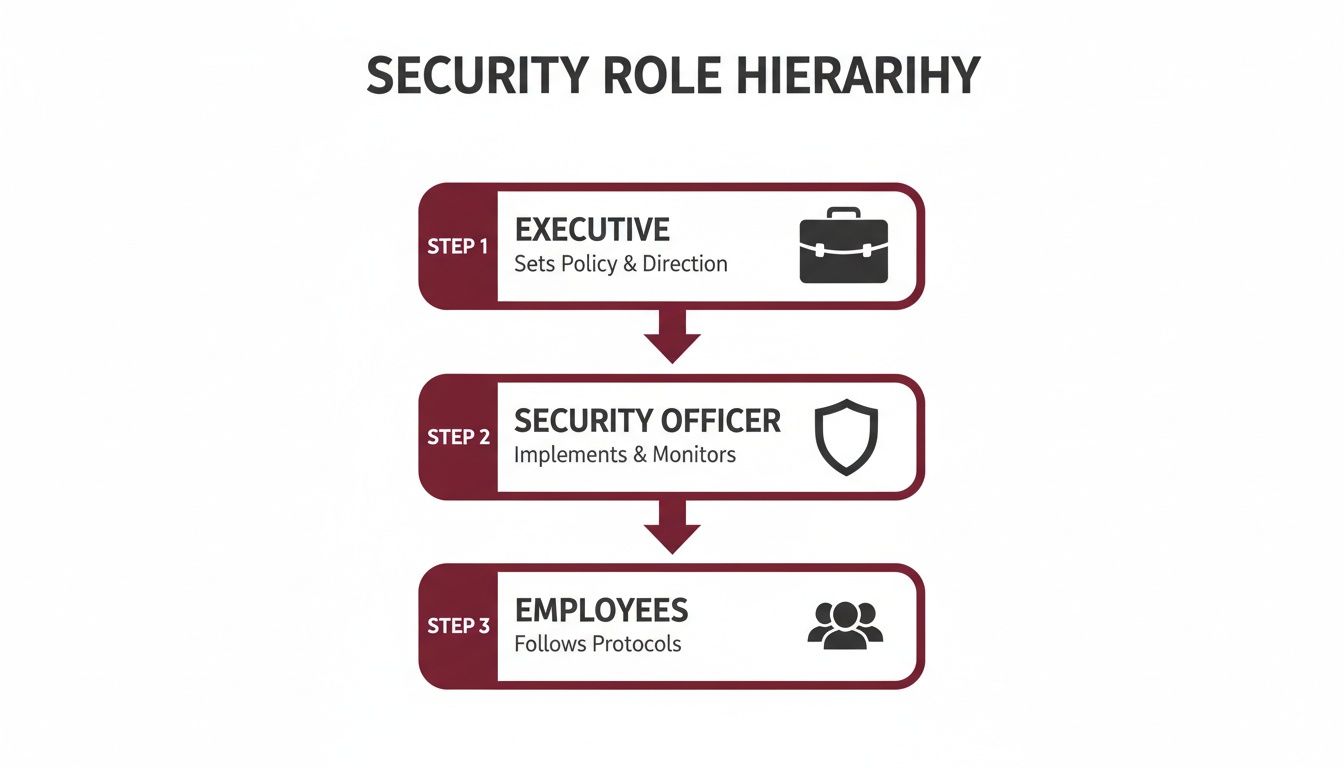
As you can see, leadership provides the authority and the security team manages the framework, but the whole system relies on every single employee doing their part.
Communication and Initial Training
Right, your first job is to introduce the policy to everyone. Don't just email it out and hope for the best—that approach is doomed to fail. You need to explain the why behind the rules. Your goal is to frame this not as a set of annoying restrictions, but as a shared mission to protect the business, its data, and everyone’s livelihoods.
I’ve found the best way to do this is with a mandatory all-hands meeting. Walk everyone through the key sections that impact their daily work, like password rules, data handling, and using personal devices. This is your moment to get everyone on board, answer questions, and squash any concerns right from the start.
Immediately follow that up with proper security awareness training. And please, don't make it a snoozefest of PowerPoint slides. Good training is interactive. It uses real-world examples of phishing scams and social engineering tricks that your team might actually encounter. For some great ideas on this, take a look at our guide to effective cybersecurity training for employees.
A policy people don't understand is a policy they won't follow. Your goal isn't just to make them aware of the rules, but to get them to genuinely accept security as part of their job.
Integrating the Policy into Operations
For your policy to stick, it needs to be baked right into your standard business processes. The most logical place to start is with new hires.
- Day One Briefing: Make reviewing the IT security policy a non-negotiable part of every new starter’s induction.
- Policy Acknowledgement: Get every new employee to read and sign an acknowledgement form. This simple step creates a clear line of accountability from their very first day.
- System Access: Here’s a pro tip: don't grant full system access until after they've completed their initial security training.
By embedding security into your onboarding checklist, you set a strong standard from the get-go.
Ongoing Maintenance and Auditing
Your IT security policy can't be a "set and forget" document. Threats are constantly changing, your technology stack evolves, and your business grows. Your policy has to keep up.
Schedule a formal annual policy review. Get your key people in a room—management, IT, department heads—and go through it. Does it still make sense for the business? Does it address the latest risks? You should also trigger a review if something big changes, like moving to a new cloud provider or overhauling how you manage customer data.
This constant upkeep is vital for improving your overall security readiness. The 2025 Cisco Cybersecurity Readiness Index found that only 4% of Australian organisations are considered 'Mature' in Identity Intelligence, with a whopping 29% calling it their biggest challenge. This is a gap you can close through diligent policy maintenance, like regularly auditing who has access to what.
Finally, don’t wait for a formal audit to discover your blind spots. Run your own simple spot-checks. A quarterly review of user access logs or a quick check to ensure ex-employees' accounts were disabled promptly can make a huge difference. These small, consistent actions keep your policy relevant and effective, preventing minor issues from snowballing into major security incidents.
Keeping your policy current is an ongoing commitment, not a one-off project. Here is a simple checklist to guide your annual maintenance process.
Annual IT Security Policy Maintenance Checklist
This checklist outlines the essential tasks to perform each year to ensure your IT security policy remains a current, effective, and compliant asset for your business.
| Task | Frequency | Owner | Objective |
|---|---|---|---|
| Full Policy Review | Annually | Security Officer | Assess overall relevance, alignment with business goals, and compliance with standards. |
| Risk Assessment Update | Annually | IT/Management | Identify new threats and vulnerabilities that have emerged over the past year. |
| Incident Response Plan Test | Annually | IT/Security Team | Run a tabletop exercise or simulation to test the effectiveness of the response plan. |
| Access Control Audit | Annually | IT Manager | Review user permissions and remove any unnecessary or excessive access rights. |
| Stakeholder Feedback Session | Annually | Security Officer | Gather input from department heads on policy practicality and operational impact. |
| Update Training Materials | Annually | HR/Security Team | Refresh training content to reflect policy changes and new threat intelligence. |
| Review Third-Party Agreements | Annually | Legal/Management | Ensure vendor security requirements are still being met and are up to date. |
| Policy Communication & Sign-off | Annually | Management | Communicate any updates to all staff and obtain fresh acknowledgement where needed. |
By systematically working through these tasks, you can be confident that your policy isn't just a document, but a dynamic tool that actively protects your organisation.
Answering Your IT Security Policy Questions
It’s completely normal to have questions pop up as you get into the nitty-gritty of creating and managing a document as important as an IT security policy. I’ve been there. Let’s tackle some of the most common queries I hear from business owners and IT managers, so you can move forward with real confidence.
Getting these details right is what makes a policy truly work in the real world, not just on paper.
How Long Should an IT Security Policy Be?
Honestly, there's no magic number. I've seen effective policies for small businesses that are a neat 10-20 pages, and I've worked with large enterprises whose documentation is far more extensive. The goal isn't to hit a specific page count; it's to achieve clarity and cover your specific risks.
Your policy needs enough detail to cover the essentials—like acceptable use, data classification, and what to do when something goes wrong—but it has to be written in a way that your team will actually read and understand. Often, the best approach is to have a core policy document supported by shorter, dedicated guidelines (like a standalone Password Policy). This is much more digestible than one monster document that no one will ever open.
What’s the Biggest Mistake People Make When Writing a Policy?
Hands down, the most common pitfall is creating a generic policy that doesn't connect with the people who need to follow it. Grabbing a template off the internet and just changing the company name is a recipe for disaster. If it isn't customised to your business, your technology, and your unique company culture, it’s just not going to stick. A policy has to be practical and enforceable.
Another huge mistake? Forgetting to get the leadership team on board from the start. If the people at the top don't champion the policy, it sends a message to everyone else that it's not a priority. Without that visible support, it quickly becomes just another document collecting dust on a server.
An IT security policy's success isn't measured by its length or how technical it sounds. It's measured by its adoption. If your team can't understand it or doesn't believe in it, you're left with a false sense of security—which is often more dangerous than having no policy at all.
How Often Do We Really Need to Train Our Team?
Security training is never a "one and done" deal. The absolute baseline is providing comprehensive security awareness training for every new hire during their onboarding, with a mandatory annual refresher for the entire team.
But let's be realistic—threats evolve much faster than that. The best defence is continuous education. Think about running monthly phishing simulations to keep everyone sharp or sending out quarterly security updates with fresh tips and reminders. Most importantly, whenever you make a significant change to the IT security policy, you absolutely must roll out specific training on those updates. It’s the only way to ensure everyone knows the new rules of the road.
We specialise in taking the complexity out of information security. With a 100% success rate, we guide Australian businesses through ISO 27001 certification, transforming your IT security policy into a powerful asset that builds trust and drives growth. Contact us today to simplify your certification journey.
Recent Comments