

Pen Testing as a Service (PTaaS) is a newer, smarter way to handle cybersecurity testing. Instead of the old-school, once-a-year penetration test, PTaaS works on a subscription model, giving you continuous security testing. It cleverly blends automated scanning tools with the sharp insights of human experts to find and help you fix security weaknesses as they pop up.
Why Your Security Strategy Needs an Upgrade
Picture this: a successful Australian business, built on years of trust and hard work, suddenly finds its digital doors kicked in by a cyberattack. This isn't just scaremongering; it's a real and growing risk for any business still relying on outdated security checks. The traditional annual pen test, which used to be the benchmark, simply can't keep up with the speed of modern threats.
Think of it like this: a one-off security audit is like having a single health check-up and then assuming you're perfectly fine for the other 364 days of the year. Pen Testing as a Service (PTaaS), on the other hand, is like wearing a 24/7 fitness tracker that constantly monitors your vitals, alerting you the moment something looks off.
The Problem with Point-in-Time Security
The digital world moves at a blistering pace. Cybercriminals are always cooking up new attack methods, and your business is constantly changing too—launching new apps, tweaking code, and connecting new systems. Every single one of those changes can accidentally open up a new backdoor for an attacker.
A static, once-a-year pen test can create a dangerous illusion of security. It’s just a snapshot of your defences on one particular day, leaving you completely blind to flaws that might appear the very next week, or even hours later. This reactive approach forces you to play catch-up with attackers.
This gap between tests is a massive window of opportunity for criminals. It’s precisely in this quiet period that they can exploit newly discovered weaknesses before you even know they exist.
Embracing a Continuous, Agile Model
This is exactly why shifting to pen testing as a service isn't just an improvement; it's essential for survival. PTaaS turns security from a single, scheduled event into an ongoing, integrated part of how you operate. It's built for the fast-moving reality of modern business, giving you a proactive defence that adapts as you do.
This model brings some immediate, practical benefits:
- Real-Time Visibility: Forget waiting months for a dense report. You get a live, up-to-the-minute view of your security posture.
- Faster Fixes: Vulnerabilities are flagged the moment they're found, so your team can patch them before they become a real problem.
- Smarter Budgeting: The subscription model spreads the cost, making top-tier security testing affordable without a huge upfront investment.
The urgency here is highlighted by the rising tide of cyber incidents in Australia. We've seen a huge spike, with over 36,700 cybersecurity-related hotline calls—a 12% jump from the year before. In that same timeframe, over 1,100 major incidents were reported. Worryingly, state-sponsored actors targeted critical infrastructure in more than 11% of these cases, pushing more and more Australian organisations to adopt PTaaS.
More Than a Tool, It's a Business Service
At the end of the day, you should see PTaaS as a crucial service for business continuity. This isn't just about finding bugs in your software. It’s about protecting your revenue, your reputation, and the trust you've worked so hard to build with customers.
To truly bolster your security, it's also vital to implement strong API security best practices, which is something PTaaS is perfectly designed to help you test and validate. By moving away from a reactive, "check-the-box" mindset to a proactive, continuous security culture, you're setting your business up not just to survive, but to thrive securely.
How Pen Testing as a Service Really Works
So, what exactly is Pen Testing as a Service (PTaaS)? Let's break it down.
Imagine hiring an inspector to check your office building’s security. In the old-school, one-off pen testing model, that inspector shows up once a year. They'll jiggle the door handles, check the alarm system, and hand you a thick report a few weeks later. For that one moment in time, you know where you stand.
PTaaS, on the other hand, is like having a dedicated security team on-site 24/7. They’re constantly patrolling the perimeter, checking every door and window, and immediately flagging any new weakness they find—day or night.
This isn’t just a simple scan; it’s a far more sophisticated model. At its core, PTaaS is a platform-based approach that fuses the raw power of automated scanning with the clever, creative thinking of expert ethical hackers. It stops security from being a static, once-a-year event and turns it into a living, breathing part of your day-to-day operations.
The Hybrid Power of Automation and Human Skill
The real magic of PTaaS is in its hybrid model. You’re not forced to choose between the speed of a machine and the intuition of a human expert. Instead, it intelligently combines both to give you a much deeper and more reliable security assessment.
Think of it as a layered process:
-
Continuous Automated Scanning: First, the PTaaS platform unleashes powerful scanners that work tirelessly in the background. They’re constantly probing your digital assets—apps, networks, cloud infrastructure—for known vulnerabilities and common security mistakes. This gives you a wide, always-on baseline of defence.
-
Expert Human Validation: This is where PTaaS truly separates itself from the pack. Instead of just dumping a raw list of potential issues on your desk, seasoned security pros step in. They review the automated findings, filter out all the "noise" and false positives that waste your team's time, and confirm which alerts are genuine, exploitable risks.
-
Creative Manual Testing: Now, the human experts take it a step further. They think like real attackers, trying to exploit the confirmed vulnerabilities. They’re looking for the kind of complex business logic flaws or chained exploits—where they combine several small issues to create a massive security hole—that automated tools will always miss.
This combination gives you the best of both worlds. The machines provide the scale to cover your entire digital footprint continuously, while the human experts deliver the depth and context needed to find the most subtle and dangerous threats.
From Vague Risks to Actionable Insights
One of the biggest headaches with traditional testing is getting a 100-page, jargon-heavy report weeks after the test concluded. By the time your team even starts to decipher it, the findings are probably already stale. PTaaS completely changes this dynamic.
Instead of a static PDF, a good PTaaS provider gives you a live, interactive dashboard. This becomes your command centre for security, showing new vulnerabilities in real time and tracking your team’s progress in fixing them.
This platform-centric model turns vague risks into clear, prioritised tasks for your developers. Every finding is enriched with the details they actually need to get the job done quickly.
- Severity Score: Each vulnerability is ranked by its potential impact (often using a CVSS score), so your team knows exactly what to tackle first.
- Detailed Explanations: You get plain-English descriptions of the flaw, explaining how it works and what the real-world business impact could be.
- Proof-of-Concept: Pentesters provide clear evidence, like screenshots or code snippets, showing precisely how the vulnerability can be exploited.
- Actionable Remediation Guidance: Your developers receive specific, step-by-step instructions on how to properly patch the weakness.
The Complete PTaaS Lifecycle
The entire pen testing as a service process is designed to be a continuous loop, not a one-and-done event. It weaves security right into your workflow, making it part of the fabric of how you operate.
Here’s what that journey typically looks like:
-
Onboarding and Scoping: You’ll sit down with the provider to define the testing scope—which applications, networks, or cloud environments are in play. This makes sure the testing is focused on what matters most to your business.
-
Continuous Assessment: The hybrid model kicks off, with automated scans and expert manual testing running constantly in the background.
-
Real-Time Reporting: As soon as vulnerabilities are found and verified, they pop up on your dashboard. Your team gets notified about critical issues immediately, not weeks later.
-
Collaborative Remediation: This is where the “service” part really shines. Your developers can chat directly with the pentesters through the platform, ask questions, and get clarification on the fixes. To get a better sense of what this involves, you can explore the full range of professional penetration testing services.
-
Verification and Re-testing: Once your team deploys a fix, they can request a re-test with a click of a button. The security experts will then jump back in to confirm that the patch worked and the vulnerability is officially closed.
This agile, collaborative cycle moves security from a dreaded annual audit to a genuine partnership. It helps your team find and fix flaws faster than ever before, dramatically shrinking your window of exposure to cyber threats.
What is the Business Value of PTaaS?
Let’s be honest: thinking of security as just another technical box to tick is a surefire way to end up on the news for all the wrong reasons. The real value of Pen Testing as a Service (PTaaS) isn't just about finding bugs in your code. It's about delivering real, tangible business value that transforms security from a cost centre into a genuine competitive advantage.
This isn't about spending money; it's about protecting it. A continuous approach to security delivers a powerful return by safeguarding your most critical assets. We're talking about preventing the kind of catastrophic data breach that can obliterate profits, shatter customer trust, and mire your team in regulatory headaches for years. A proactive security posture, proven through PTaaS, is a non-negotiable part of modern business resilience.
The process itself is straightforward, moving logically from discovery to actionable intelligence.
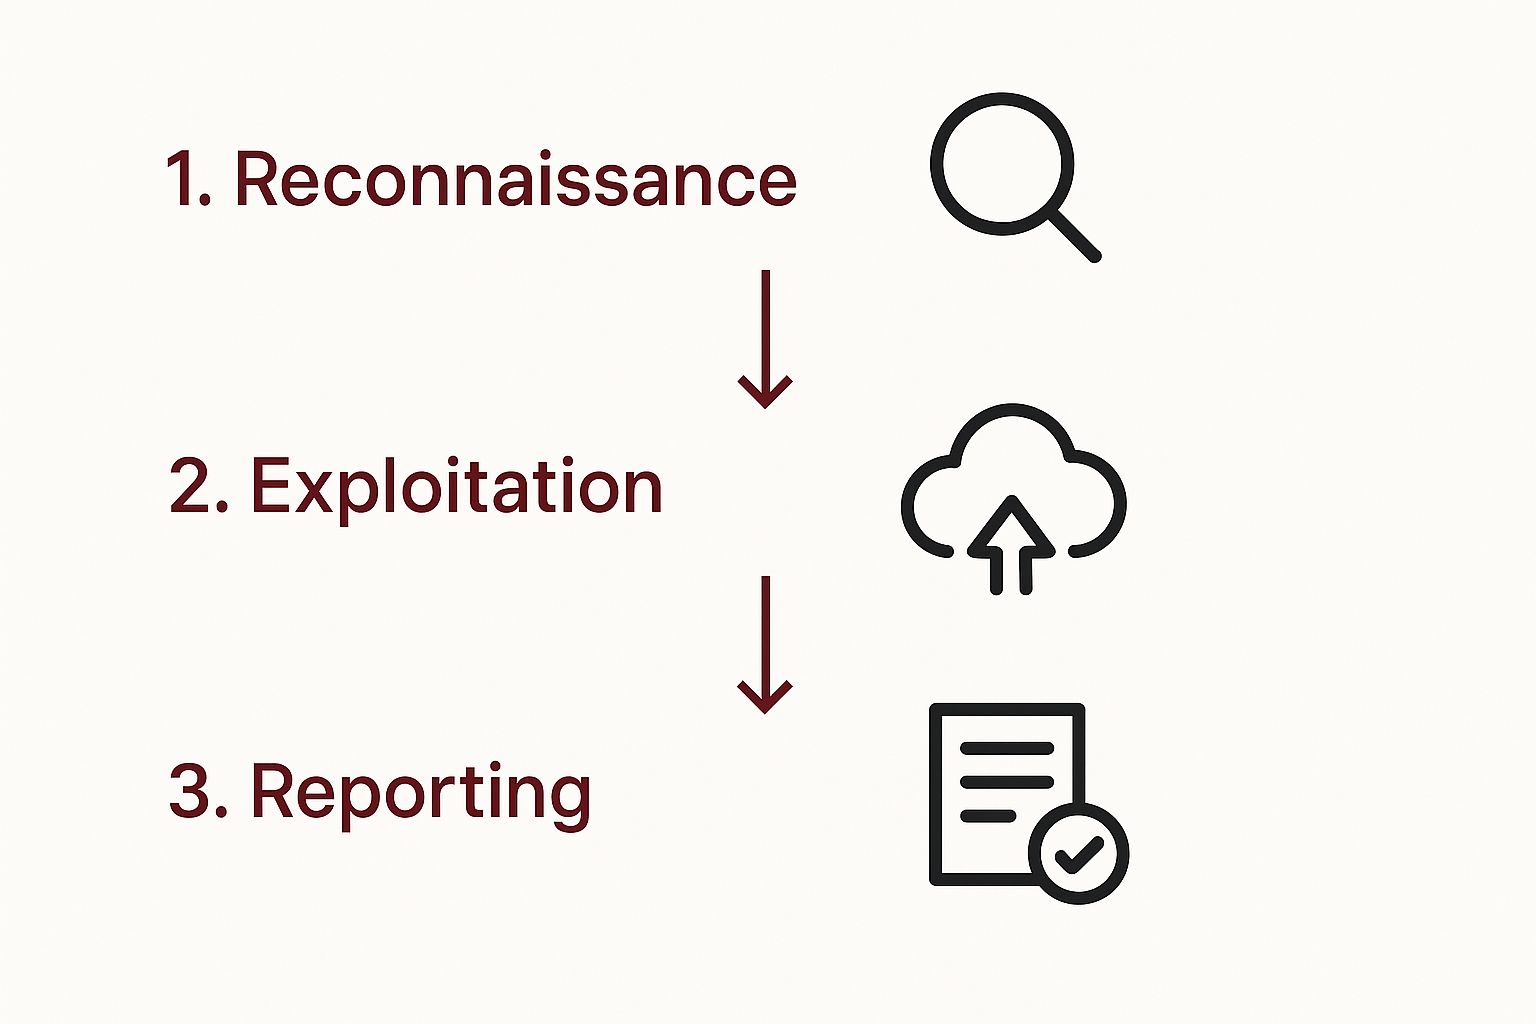
This workflow ensures that threats are not only found but are presented in a way that allows your team to address them systematically and effectively.
Turn Compliance From A Burden Into An Advantage
For any Australian business, navigating the dense jungle of regulations isn't optional. Mandates like APRA's CPS 234 and the ever-present Privacy Act require a provable, consistent handle on information security. Crossing your fingers and hoping for the best simply won't cut it.
This is where PTaaS really shines. It provides the very mechanism you need to meet these stringent demands head-on. Forget the frantic, last-minute scramble before an annual audit. With PTaaS, you exist in a state of continuous compliance, backed by a live, auditable trail of every test, vulnerability, and remediation effort.
Suddenly, compliance shifts from a stressful, periodic nightmare into a smooth, ongoing part of business as usual.
Imagine an auditor asks for proof of your security testing program. Instead of digging through old reports, you pull up a dynamic dashboard showing a complete history. This demonstrates a mature, proactive security culture that regulators and potential partners absolutely love to see.
This level of preparedness doesn't just keep you on the right side of the law; it gives you a massive advantage when bidding for contracts where security is a deal-breaker.
To better understand the shift, here’s a look at how the two models stack up.
Traditional Pen Testing vs Pen Testing as a Service
This table breaks down the key differences, highlighting why the PTaaS model is a better fit for the dynamic nature of modern business.
| Feature | Traditional Pen Test | Pen Testing as a Service (PTaaS) |
|---|---|---|
| Frequency | Annual or bi-annual point-in-time snapshot. | Continuous, on-demand, and automated scans. |
| Scope | Fixed scope, often outdated by the time it's tested. | Dynamic scope that adapts to new features and code changes. |
| Reporting | A static, lengthy PDF report delivered weeks later. | Real-time dashboard with actionable, prioritised findings. |
| Remediation | Manual tracking; re-testing is a separate, costly project. | Integrated ticketing, collaboration, and instant re-testing. |
| Cost | High upfront cost for a one-off engagement. | Predictable subscription-based model (SaaS). |
| Agility | Poor fit for Agile/DevOps; slows down development. | Designed for modern CI/CD pipelines; accelerates delivery. |
The contrast is stark. PTaaS moves security from a periodic, disruptive event to a fluid, integrated function that supports business goals instead of hindering them.
Build Unbreakable Customer And Partner Trust
In today's market, trust is everything. A single security incident can vaporise years of hard work building a loyal customer base. The data tells a sobering story: a Deloitte survey found that 68% of Australian consumers would likely abandon a brand after a data breach. Security is no longer a back-office function; it’s a core part of the customer experience.
Pen testing as a service gives businesses a way to conduct the regular, automated security checks needed to meet partner requirements and protect sensitive information. It’s a powerful signal to the market that you take the protection of their data seriously.
When you can confidently prove you have a robust, continuous security testing program, you unlock several critical business outcomes:
- Win Larger Contracts: Enterprise and government clients have strict vendor security requirements. PTaaS provides the verifiable proof needed to sail through their due diligence and land those lucrative deals.
- Strengthen Partner Relationships: When other businesses integrate with your systems, they’re trusting you with their data. A continuous testing model assures them you aren't the weakest link in their supply chain.
- Enhance Brand Reputation: In a crowded field, a strong security posture is a powerful differentiator. It tells customers you’re a reliable and trustworthy partner.
From Reactive Firefighting To Proactive Defence
The old way of doing security often feels like constant firefighting. An incident flares up, and everyone drops everything to contain the damage. It's stressful, inefficient, and incredibly expensive.
PTaaS completely flips this script. By continuously probing for weaknesses, it lets you shift to a far more strategic and proactive defence. This is closely aligned with the idea of active defence, where you don’t just sit back and wait for an attack. To dig deeper into this mindset, you can learn more by reading our guide on threat hunting as a proactive method to neutralise cyber threats.
This proactive stance creates a virtuous cycle of improvement. Instead of learning about a vulnerability from an attacker, you find out from your trusted PTaaS partner in a controlled, collaborative setting.
Your team can then schedule fixes into their normal development sprints, avoiding those chaotic, all-hands-on-deck emergencies. The result? Better security, higher team morale, and more predictable development cycles that keep your business moving forward, securely.
Weaving PTaaS Into Your Workflow
Picking a powerful security solution like pen testing as a service is one thing. Making it a natural, productive part of how your team works every day? That’s something else entirely. The real magic of PTaaS isn’t just finding weaknesses; it’s about knitting security right into the fabric of your development and operational cycles. It’s built to be a catalyst for improvement, not just another tool that creates friction.
This simple shift changes security from a last-minute hurdle into a real-time, collaborative effort. Instead of being an afterthought, security becomes fundamental to how you build and run your products from the very start.
It's here, in the day-to-day integration, that the "as a service" model truly shines, helping your teams become more secure and more efficient at the same time.
Shifting Security Left With DevSecOps
Modern software development is all about moving fast. In a DevSecOps culture, security isn’t just the job of a separate team that appears at the finish line. It’s a shared responsibility that’s "shifted left," meaning it's baked into every phase of the development lifecycle.
PTaaS is the perfect engine to drive this cultural change. It effectively demolishes the old walls that stood between your development, operations, and security teams.
Imagine your developers getting instant, clear feedback on a security flaw right inside the tools they already live in. This quick-fire feedback loop stops security bugs from ever reaching production, which saves a phenomenal amount of time and money down the track.
Instead of waiting weeks for a dense report, a developer can get an alert in their project management board the moment a vulnerability is found in a new feature. This means they can fix it on the spot while the code is still fresh in their mind.
Seamless Integration With Your Existing Toolchain
One of the biggest wins with PTaaS platforms is how well they connect with the tools your teams already know and love. This is what makes the whole process feel natural instead of forced. A quality provider will offer solid integrations that smooth out the entire vulnerability management process from discovery to resolution.
Common integration points include:
- Project Management Tools: When the PTaaS platform uncovers and validates a vulnerability, it can automatically create a ticket in systems like Jira or Asana. That ticket arrives fully loaded with all the crucial details—severity, description, and remediation advice—ready for a developer to grab.
- Communication Platforms: Critical alerts can be pushed straight into team channels on Slack or Microsoft Teams. This guarantees that high-priority issues get eyes on them immediately, kicking off a rapid response.
- CI/CD Pipelines: You can hook PTaaS directly into your Continuous Integration/Continuous Deployment pipeline. This sets up automated security checks that run every time new code is committed, acting as a security gate to stop vulnerable code in its tracks.
As you plan to weave PTaaS into your infrastructure, thinking about how to deploy any necessary components is key. Looking into different automated installation methods for enterprise software can give you some great ideas for a pain-free rollout.
Fostering a Culture of Shared Security Ownership
Something powerful happens when security insights land directly in your developers' laps. Security stops being someone else's problem and becomes everyone's job. This isn't about pointing fingers; it's about empowering your team with the knowledge they need to write safer code from day one.
The collaborative features of a PTaaS platform are what make this happen. Developers can chat directly with the ethical hackers who found the flaw, ask questions, or get help validating a fix. This turns what used to be a chore into a genuine learning opportunity. Over time, your team’s security instincts sharpen, and they start to think more like a defender.
This sense of shared ownership brings some profound benefits to an organisation:
- Faster Deployment Cycles: By catching and fixing security issues early, you kill the delays that last-minute security panics cause.
- Lower Remediation Costs: It's exponentially cheaper to fix a bug during development than to patch it on a live production system.
- Better Team Morale: Developers feel empowered when they can own the quality and security of their work, leading to higher job satisfaction and a stronger, more resilient team.
The expertise needed to manage this integrated approach often goes beyond the tools. Many businesses find that partnering with specialists who get both the tech and the compliance side of things is a game-changer. Seeing how professionals deliver security for managed IT services can paint a clearer picture of how this expertise supports a secure, cohesive workflow. By building a unified front, you ensure your security is rock-solid from code to cloud.
How to Choose the Right PTaaS Provider
Picking a partner for your pen testing as a service is one of the biggest security calls you'll make. This isn't just about hiring another vendor; you're bringing on a strategic ally to help defend your business. To get it right, you have to look past the price tag and really dig into the skills, processes, and expertise that separate the great providers from the rest.
This decision is your chance to move beyond just ticking a compliance box. A top-notch partner won't just find holes in your defences—they’ll work with you to build a genuinely stronger, more secure organisation from the ground up.
Evaluate the Blend of Automation and Human Expertise
The real magic of PTaaS is in its hybrid approach, but not everyone gets the balance right. You need a partner who cleverly combines the relentless speed of automated tools with the creative, out-of-the-box thinking of seasoned ethical hackers. Don't get fooled by platforms that are little more than jazzed-up vulnerability scanners.
You need to ask some direct questions:
- How much of your testing is automated versus done by a real person?
- What's your process for checking automated findings to weed out the false positives?
- Can you give me examples of complex business logic flaws you've found that a scanner would have completely missed?
A first-rate provider uses automation to cast a wide, continuous net but brings in their human experts to hunt down the subtle, high-impact vulnerabilities that pose the biggest threat.
Scrutinise Tester Certifications and Experience
The quality of your pen test comes down to the skill of the testers. The people trying to break into your systems should be highly qualified and have years of real-world experience. Make sure you're looking at a team whose members hold respected, industry-standard certifications.
These aren't just letters after a name; they represent a proven ability to think like an attacker and a commitment to ethical standards.
Key certifications to look for are CREST (Council of Registered Ethical Security Testers) and OSCP (Offensive Security Certified Professional). These are tough, hands-on exams that prove a tester can do more than just run a tool and print a report—they can actually find and exploit vulnerabilities like a genuine threat actor.
Beyond the certs, ask about their experience in your specific industry. A provider who gets the unique threats and regulatory headaches facing Australian financial services or healthcare, for instance, is going to deliver a far more valuable and relevant assessment.
Assess the Clarity and Actionability of Reporting
A brilliant pen test is worthless if the results land on your desk as a confusing, jargon-packed report your team can't do anything with. The provider's platform and how they report findings are just as important as their testing skills. You need a system that turns raw security data into clear, actionable intelligence.
A strong reporting platform should give you:
- A Real-Time Dashboard: You need to see vulnerabilities as they’re discovered, not wait weeks for a static PDF to arrive.
- Prioritised Findings: Issues should be ranked by severity (using something like a CVSS score) and actual business impact, so your team knows exactly what to fix first.
- Detailed Remediation Guidance: Every finding must come with clear, step-by-step instructions that your developers can actually use to patch the weakness.
The whole point is to empower your team, not bury them in data. The platform should be a collaborative tool where your developers can talk directly with the security experts to ask questions and get fixes validated.
Demand Deep Australian Regulatory Understanding
If you're doing business in Australia, compliance isn't optional. A provider with only a surface-level understanding of the local regulatory scene can leave you dangerously exposed. You need a partner with deep, hands-on experience helping businesses meet specific Australian rules.
This is especially critical in such a fast-growing market. The global penetration testing market, currently valued at USD 2.45 billion, is tipped to reach USD 6.25 billion by 2033, with the Asia-Pacific region leading the charge. This boom makes it even more important to choose a partner who understands both global threats and local regulations. You can learn more about the penetration testing market's growth and what it means for Australian organisations.
Your provider should be able to talk confidently about:
- APRA CPS 234: The essential information security standard for the financial services industry.
- The Privacy Act: Particularly the Notifiable Data Breaches (NDB) scheme.
- ISO 27001: The global standard for information security management.
Ask them to show you exactly how their reporting and processes map to these frameworks, making your life easier when audit time comes around.
Verify Remediation Support and Scalability
A true pen testing as a service partnership doesn't stop the moment a vulnerability is found. The best providers stick with you through the entire fix-it cycle, offering solid support to make sure flaws are actually patched. This is a massive differentiator.
Look for a provider that offers:
- Direct Access to Testers: Your team should be able to chat directly with the experts who found the issue to get clarification and advice.
- Integrated Re-testing: The platform should make it dead simple to request a re-test once a fix is in place, with experts on hand to quickly verify it worked.
- Scalable Service: The provider has to be able to grow with you. Whether you're a small startup today or a large enterprise tomorrow, their platform and team must be able to scale without friction.
By carefully working through these points, you can confidently choose a PTaaS provider who will become a genuine, long-term partner in securing your business. This focused approach ensures you’re investing in a service that delivers continuous value, strengthens your defences, and supports your growth.
Your PTaaS Questions, Answered
Even when the benefits seem clear, stepping into a new security model like Pen Testing as a Service naturally comes with questions. Business leaders want to feel certain, clear, and confident before they shift strategy. Let's tackle the most common questions and concerns we hear from Australian businesses, with straight-talking answers to help you make your decision.
"Isn't PTaaS Just for Big Corporations?"
That's a really common assumption, but the opposite is true. PTaaS is actually a game-changer for small and medium-sized businesses (SMEs). For years, proper penetration testing was just too expensive and complicated for smaller companies, which left them wide open to attack.
The subscription nature of pen testing as a service completely changes the game. It puts enterprise-grade security within reach by spreading the cost out over time, making it affordable. It lets SMEs prove they have a strong security posture without needing a huge upfront budget—something that’s often a deal-breaker when trying to land contracts with larger corporate or government clients.
At the end of the day, PTaaS levels the playing field. It delivers continuous protection that scales right alongside your business as it grows.
"How Is This Any Different From an Automated Scanner?"
Getting this distinction right is absolutely vital. While any good PTaaS platform will use automated scanners to give you broad, continuous coverage, that’s just the starting point. The real value, and what you’re paying for, is the human brainpower layered on top.
Expert ethical hackers take what the scanner finds, toss out all the false positives that would waste your team's time, and then get creative. They hunt for the complex, clever vulnerabilities that automated tools will always miss.
Think of it like this: a scanner can tell you a door is unlocked. A human expert can show you how an attacker could slip through that door unnoticed, what they could steal once inside, and how they could use that access to get to other parts of the building. And most importantly, they'll tell you exactly how to secure it for good. With PTaaS, you get the best of both worlds: machine speed and human intellect.
"Will This Testing Disrupt Our Business?"
Not at all. A professional PTaaS provider designs every test to be as quiet and non-disruptive as possible. The whole point is to strengthen your defences without getting in the way of business. The vast majority of scans and manual tests are done in a way that won’t affect the performance or availability of your live systems.
Before any testing starts, you'll work together to establish clear "rules of engagement." This is just a document that spells out what’s in scope, what’s off-limits, and the methods they’ll use. Any more intense testing can simply be scheduled for after-hours or run against your staging environments. The entire process is a safe, collaborative partnership designed to harden your systems, not break them.
"What Happens After You Find Something?"
This is where PTaaS really shines compared to the old way of doing things. Instead of getting a massive, 100-page PDF report weeks after a test, you see vulnerabilities pop up on a live dashboard in real-time. Everything is automatically prioritised based on its severity and potential business impact.
Each finding is more than just a red flag; it’s a complete, ready-to-use package for your tech team. It includes:
- A simple, plain-English summary of the flaw and the risk it poses.
- Detailed, step-by-step instructions for your developers on how to fix it.
- Proof-of-concept evidence, like screenshots or code snippets, showing exactly how it can be exploited.
Even better, the platform is built for collaboration. Your team can chat directly with the security experts who found the issue. They can ask questions, get a second opinion on their fix, and then request a re-test with a single click. This turns security from a one-off audit into a continuous, collaborative cycle of improvement.
"What's the Typical Cost of PTaaS?"
The cost of pen testing as a service will depend on the size and complexity of your digital footprint, but it’s far more predictable and budget-friendly than traditional one-off tests. The subscription model, usually billed monthly or annually, gets rid of the big, chunky capital outlays you see with project-based testing.
Pricing is generally based on a few key factors:
- The number of applications or IP addresses you need tested.
- The frequency and depth of manual, expert-led testing required.
- The level of support and collaboration you need to fix things.
While a simple scan for a small website might start in the low hundreds, a comprehensive program for a complex application could be several thousand dollars a month. The key is that the cost is transparent and scales with your needs, turning it into a predictable operating expense. When you remember that the average cost of a data breach can run into the millions, the return on investment for continuous testing becomes crystal clear.
"How Does PTaaS Help With Our Compliance?"
PTaaS is a brilliant tool for staying on top of—and proving—your compliance with various regulations. For Australian businesses, this is especially important for frameworks like ISO 27001, APRA CPS 234, and the Notifiable Data Breaches (NDB) scheme under the Privacy Act.
Instead of scrambling to find evidence during an audit, a PTaaS platform gives you a continuous, ready-made audit trail of all security testing. The dashboard acts as a living document, showing every vulnerability found, when it was fixed, and proof of the fix. It demonstrates a mature, proactive approach to security that auditors and regulators love to see. It transforms compliance from a stressful, periodic chore into a steady, business-as-usual process.
At Anitech, we specialise in helping Australian businesses navigate the complexities of information security. Our expertise in ISO 27001 and robust security practices can help you build a resilient and compliant organisation. If you're ready to move beyond outdated security checks and build a truly proactive defence, explore our consulting services.
Recent Comments