

Quick Summary: A process defines the high-level strategy of what needs to be done and why it's important for a business goal. A procedure provides the detailed, step-by-step instructions on how to perform a specific task within that process. Understanding this difference is fundamental for building a logical and auditable Information Security Management System (ISMS).
Getting the difference between a procedure vs process straight is the first—and most critical—step in building an Information Security Management System (ISMS) that's logical, effective, and ready for an audit. A process lays out the strategic flow of work, answering the 'what' and 'why,' while procedures give you the tactical, step-by-step instructions on 'how' to ensure that work gets done correctly and consistently.
This isn't just about semantics; it's the foundation of successful ISO 27001 compliance. Auditors need to see both the big-picture strategy (your processes) and concrete proof that you're following through with standardized actions (your procedures).
Unpacking Process vs Procedure: Core Differences
To really get a feel for this, it helps to break down the core differences. A process is all about the bigger picture—it defines the inputs, the outputs, and the ultimate goal of a string of related activities. It answers the ‘what’ and ‘why’ behind a major business function, like managing user access or handling a security incident.
A procedure, however, is the detailed, boots-on-the-ground guide. It answers ‘how’ a specific task gets done, ‘who’ does it, and ‘when’. It’s designed to eliminate guesswork and ensure critical tasks are repeatable and predictable, which is absolutely essential for managing risk. This is the level of detail that gives an auditor the evidence they need to see your security controls are actually working as you claim.

At a Glance: Key Differences Between Process and Procedure
This distinction is crucial when you start documenting your ISMS. A well-defined process gives you a solid framework, but without clear procedures to back it up, you have no real guarantee of consistent execution.
The table below offers a simple breakdown of the fundamental attributes that separate these two vital types of documentation.
| Attribute | Process | Procedure |
|---|---|---|
| Focus | Defines what to do and why | Details how to do it |
| Scope | Broad and strategic (end-to-end workflow) | Narrow and tactical (a specific task) |
| Level of Detail | High-level overview with key steps | Granular, step-by-step instructions |
| Ownership | Typically owned by management or department heads | Executed and owned by frontline teams |
| Purpose | To achieve a strategic business objective | To ensure consistency and standardisation |
| Format | Often visualised as a flowchart or map | Usually a written, numbered checklist or guide |
| Flexibility | More flexible and adaptable to change | Rigid and prescriptive for consistent results |
Ultimately, a well-structured ISMS needs both working in harmony. You can't have one without the other and expect things to run smoothly, especially under the scrutiny of an audit.
Key Takeaway: Processes give you the strategic roadmap for your security goals. Procedures are the turn-by-turn directions that ensure your team gets to the destination safely and consistently, every time. In a robust security framework, one is simply incomplete without the other.
Why This Distinction Is Critical for ISO 27001 Success
Getting your head around the difference between a process and a procedure isn’t just about semantics. It’s the bedrock of a solid Information Security Management System (ISMS) and a non-negotiable for passing an ISO 27001 audit. The standard demands a ‘process approach’, which is really just a way of saying you need to show how all your security activities connect to achieve your wider business goals.
An auditor wants to see that your security program is a strategic, cohesive system—not just a random checklist of tasks you tick off.
A well-defined process gives you the strategic "what" and "why" for managing information security risks. In contrast, the detailed procedure provides the "how," making sure your security controls are applied the same way, every time, without fail. This structure is what makes an ISMS effective, resilient, and most importantly, auditable.
The Shift to Formalised Security Practices
The move away from casual security isn't happening by chance. It's a direct reaction to a world where ad-hoc measures are a massive liability. Businesses are waking up to the fact that informal practices create risks they simply can't afford to take.
We’ve seen this play out dramatically right here in Australia. Between 2020 and 2024, Australia saw one of the sharpest spikes in ISO 27001 adoption in the entire Asia-Pacific region. This surge wasn't a coincidence; it followed major corporate breaches that exposed the personal data of over 20 million Australians. It marks a fundamental change in how local businesses now view information security. You can get more details on the framework for ISO 27001 certification in Australia on iso-27001.com.au.
The message is clear: stakeholders, customers, and regulators are done with promises. They want verifiable proof that you’re taking security seriously, and documented processes and procedures are that proof.
Building an Auditable and Resilient ISMS
When an ISO 27001 auditor walks through your door, their job is to confirm your ISMS actually works the way you say it does. They are looking for a clear, logical thread connecting your high-level security objectives to the day-to-day actions of your team. This is where the distinction between process and procedure truly shines.
Your processes define the big picture—the "what" and "why" of your security program. Think of things like your:
- Risk Management Process: How your organisation finds, analyses, and treats security risks.
- Incident Management Process: The complete workflow for spotting, reacting to, and recovering from a security incident.
- Access Control Process: The system that governs who gets access to what, when, and why.
These processes prove to an auditor that you have a strategic game plan.
But it’s your procedures that provide the concrete, auditable evidence that your plan is actually in motion. They contain the specific, step-by-step instructions that demonstrate your controls are working and being applied consistently.
Without that link, your ISMS is just a dusty binder of policies. For instance, your overarching Access Control Process is brought to life by a specific Procedure for Onboarding New Employees, which spells out the exact steps for granting system access. The process sets the direction; the procedure delivers the on-the-ground execution.
This two-tiered structure is precisely what auditors are trained to find because it shows both intelligent design and operational discipline. It proves your security system is a living, functioning part of your organisation, built to withstand both internal changes and external attacks.
Deconstructing the Core Differences in Practice
To really get a handle on the procedure vs process debate, we need to look past the dictionary definitions and see how they play out on the ground. The differences pop when you examine them through three key lenses: the breadth of their scope, the nitty-gritty of their detail, and who holds the ownership. Nailing these distinctions is non-negotiable for building an ISMS that an ISO 27001 auditor will actually respect.
Think of it this way: a process sets the strategic direction, but the procedure provides the tactical, on-the-ground instructions to get there. If you have one without the other, you've got a massive gap in your compliance. You're left with either a grand strategy nobody knows how to execute or a bunch of disconnected tasks without a clear purpose.
Scope: Strategic vs Operational Focus
The biggest giveaway is always the scope. A process is strategic, a high-level view of how you achieve a major business objective. It often cuts across multiple teams or even whole departments. It answers the big question: "What's our overall approach here?"
A procedure, on the other hand, is purely operational. It’s a zoomed-in, tightly focused guide for a single task within that bigger process. It’s all about ensuring a specific activity happens the same way, every single time. It answers the simple question: "How do we do this one thing right?"
- ISO 27001 Example:
- Process (Strategic): The Risk Management Process is your high-level playbook. It defines how the entire organisation identifies, assesses, and treats information security risks. It pulls in people from IT, finance, and the C-suite to make sure risk decisions align with business goals.
- Procedure (Operational): The Procedure for Conducting a Third-Party Risk Assessment is just one small piece of that puzzle. It's a specific, step-by-step guide for vetting a new vendor—who sends the security questionnaire, how their answers are scored, and what red flags mean we walk away.
Level of Detail: High-Level vs Granular Instructions
This brings us to the level of detail, another dead giveaway. Processes are intentionally light on the details. You’ll often see them as flowcharts showing the main stages and decision points. They give you the "what" and the "why" but leave the "how" to other documents.
Procedures are the polar opposite; they are all about granular detail. They are written instructions, checklists, or work guides that leave zero room for interpretation. Their job is to standardise an action to get a predictable, repeatable outcome—something absolutely critical for security controls.
A process is the road map showing the major cities on your journey. A procedure is the turn-by-turn GPS navigation telling you precisely when to turn left and which lane to get into.
Let's look at another common ISO 27001 scenario to make this crystal clear.
- Process (High-Level): The Incident Management Process lays out the major phases of dealing with a breach: Detection, Containment, Eradication, Recovery, and Post-Incident Review. It defines the goals for each phase, not the specific tools or commands you’ll be running.
- Procedure (Granular): The Procedure for Isolating a Compromised Server is a detailed checklist that lives inside the "Containment" phase. It would have explicit steps like, "1. Log into the firewall management console. 2. Apply the 'Quarantine' access control list to the server's network interface. 3. Document the time of isolation in the incident log."
This is exactly what auditors are looking for. It’s tangible proof that your security controls aren't just ideas on a whiteboard; they're being implemented effectively. It shows your team isn't just making it up as they go when a crisis hits.
Ownership: Management vs Frontline Teams
Finally, look at who owns it. This tells you everything about responsibility. Processes are almost always owned by management or department heads. These leaders are accountable for the strategic outcome, making sure the process stays aligned with business objectives and gets the resources it needs.
Procedures, conversely, are owned and used by the frontline teams—the people doing the work day in and day out. They are the experts on the "how," and frankly, they’re the best people to write and refine the instructions to make sure they're practical.
This split in ownership is vital for a healthy ISMS.
- Management Ownership (Process): The Chief Information Security Officer (CISO) or IT Director owns the overarching Change Management Process. Their job is to ensure every change to a production system goes through a proper review and approval workflow to keep risk in check.
- Frontline Ownership (Procedure): A systems administrator or a developer owns the Procedure for Submitting a Change Request Ticket. They are the ones following the detailed steps to fill out the form, attach the testing evidence, and get it to the right approvers. They make sure the process is followed to the letter, every time.
When ownership is this clear, so is accountability. Management ensures the "why" is solid, and the frontline teams make sure the "how" is executed flawlessly. That creates a powerful, auditable structure that will stand up to any scrutiny.
What Auditors Really Look for in Your Documentation
When an ISO 27001 auditor walks through your door, they aren't just looking to tick boxes on a checklist. They're on a mission to understand the story of your organisation's commitment to information security. The goal is to see a clear, unbroken line connecting your high-level strategy to what your team does every single day. This is where the distinction between a process vs procedure becomes a genuine test of your ISMS maturity.
Auditors have a trained eye for disconnects. A beautifully crafted process with no procedures to back it up is an immediate red flag—it signals good intentions with no real plan for execution. On the flip side, a jumble of detailed procedures that don't roll up into a larger, strategic process suggests a reactive, chaotic approach to security. It’s just a collection of tasks without a unifying purpose.
They need to see that your ISMS is a living, breathing part of your business, not a set of binders collecting dust on a shelf. This means demonstrating a clear line of sight from a strategic process, like Access Control, right down to the nitty-gritty procedure that makes it happen, such as the User Access Review Procedure.
Proving Due Diligence Through Cohesive Documentation
In the current climate, proving you've done your due diligence is non-negotiable. The threat isn’t some abstract concept; it’s a very real and growing risk for every Australian business. The Australian Cyber Security Centre fielded over 94,000 reports of cybercrime in a recent 12-month period. That’s a staggering 23% jump from the year before.
This is exactly why auditors put so much weight on documentation. Without formalised, documented security measures, how can you possibly respond effectively or prove you took reasonable steps to protect your information? This is where auditors dig in, searching for evidence of a 'process approach'. They want to see a logical hierarchy.
- The Process: This defines the big-picture goal (e.g., to ensure only authorised users can access company data).
- The Procedure: This provides the specific, repeatable steps to achieve a piece of that goal (e.g., the step-by-step guide for deactivating a departing employee’s account).
This structure proves your security controls aren't accidental; they are deliberate, consistent, and woven into the fabric of your operations.
Connecting the Dots for the Auditor
Think of your auditor as an investigator trying to follow a trail. Your job is to make that trail as clear and easy to follow as possible. Your documentation should allow them to trace the logic from a high-level risk assessment all the way down to a specific action someone on your team took last Tuesday.
A common mistake we see is documentation created in a silo. Having a detailed procedure for patching servers is great, but it’s infinitely more powerful when it’s clearly linked to a broader Vulnerability Management Process. That process would outline how you find, assess, and prioritise threats, making the patching procedure the tactical tool that gets the job done.
Auditor's Insight: Auditors don't just want to see that you have a procedure. They want to understand why it exists, what process it serves, and how you verify that it's actually being followed. The connection between the 'what' (process) and the 'how' (procedure) is where they find confidence in your system.
Making sure your documentation meets this standard means writing with compliance in mind from the start. You can learn from guides that explain how to write HR policies and other business documents, as the core principles of clarity and auditability are universal. The aim is to create a seamless narrative that tells your security story. For a deeper dive into what to expect during the audit itself, check out our guide on the ISO 27001 audit process.
The Litmus Test for a Mature ISMS
At the end of the day, auditors are really gauging the maturity of your ISMS. A mature system shows both strategic foresight (the processes) and operational discipline (the procedures).
Here’s what an auditor is implicitly asking when they review your documents:
- Is there a clear owner? Does the process have a manager responsible for it, and does the procedure have a designated owner on the team that executes it?
- Is it practical? Is the procedure written so that a real person can follow it, or is it just dense, theoretical jargon?
- Is there evidence of use? Can you pull up records, logs, or completed forms that prove the procedure is being followed consistently as part of its parent process?
When you can confidently answer "yes" to these questions, backed by well-structured documentation, you’re set up for a smooth and successful audit. It shifts the conversation from, "Do you have this document?" to a much more powerful, "Show me how this process works in practice."
Structuring Your Documentation From Process to Work Instruction
If you really want to get your head around the procedure vs process debate, you need to see the complete picture. A well-built Information Security Management System (ISMS) doesn't just stop with procedures. It actually drills down even further, into what we call work instructions.
This three-tiered approach—Process → Procedure → Work Instruction—is the gold standard. It creates a documentation framework that’s logical, scalable, and practically foolproof. It’s exactly what auditors are looking for.
This hierarchy is powerful because it connects the high-level strategy (the "why") with the specific, on-the-ground actions (the "how"). It ensures every single task performed in your organisation can be traced back to a strategic security goal, leaving zero room for confusion.
The Role of Work Instructions
So, what exactly is a work instruction? If a procedure is the instruction manual for getting something done, a work instruction is the specific page that shows you exactly which button to press and when. It’s the most granular document you’ll have, providing step-by-step guidance for a single activity.
Think of them as task-level cheat sheets. They're written for the people on the frontline, helping them execute a specific task flawlessly and consistently without having to remember every little detail. Their focus is 100% on execution.
Many work instructions are essentially micro versions of a Standard Operating Procedure (SOP), so understanding that concept is crucial for creating clear, compliant documentation.
Visualising the Documentation Hierarchy
Let's make this tangible. The diagram below clearly shows how a high-level ISMS process cascades down into more detailed procedures and, finally, specific work instructions.
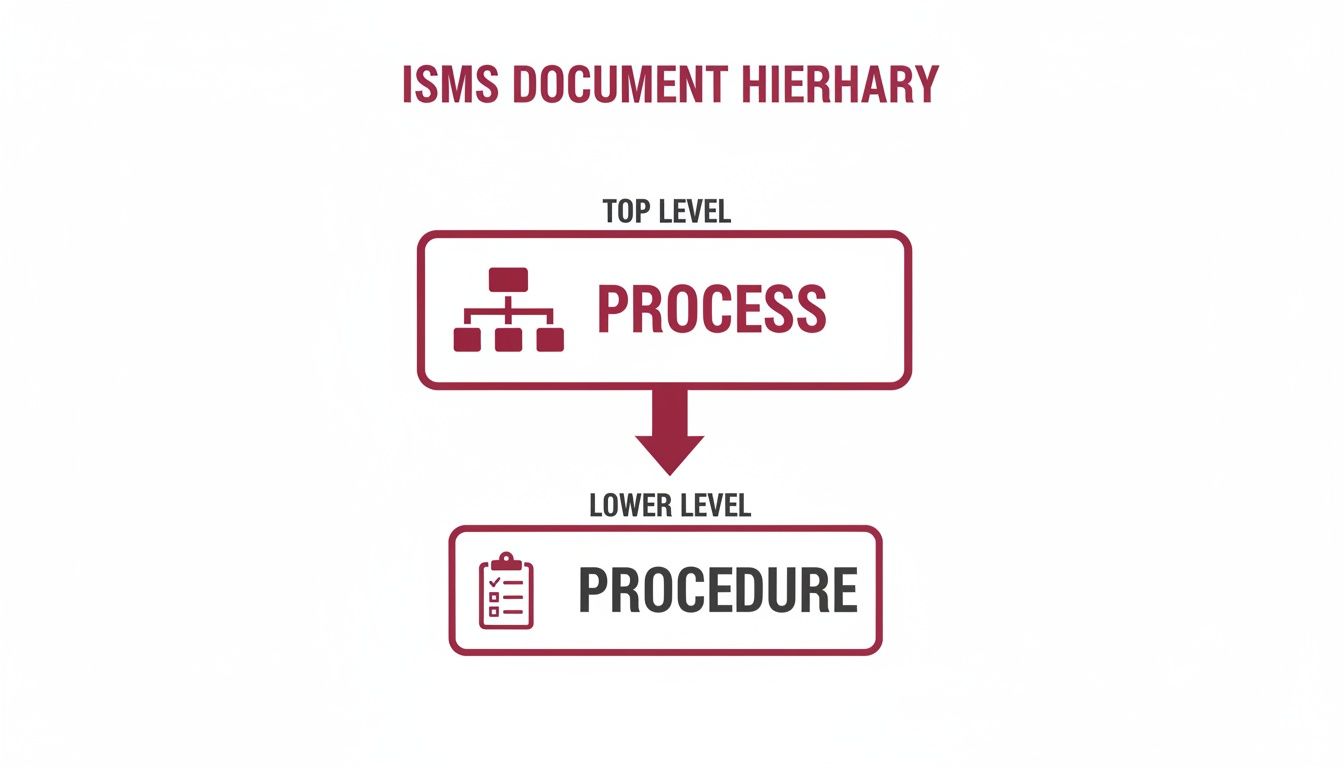
This visual shows that processes set the overarching strategy. Procedures then break that strategy into repeatable tasks, and work instructions detail how to perform those individual tasks.
This structure is what transforms your ISMS from a theoretical idea into a living, breathing operational system. An auditor should be able to pick up any work instruction and trace its lineage all the way back up to the strategic process it supports. This proves you have a mature and well-managed security program.
If you’re preparing for certification, it's worth getting familiar with the minimum documented information for ISO 27001.
Key Insight: A process is a collection of related procedures. A procedure is a collection of related tasks, and a work instruction tells you exactly how to complete one of those tasks. Each level adds a layer of specificity.
Let's ground this with a real-world example from an ISO 27001 context. Every organisation needs to manage changes to its IT systems. Here’s how that would break down.
To further illustrate this hierarchy, the table below shows how a single process can spawn multiple procedures and work instructions.
Documentation Hierarchy Example From Process to Work Instruction
| Level | Example Name | Purpose and Scope |
|---|---|---|
| Process | Change Management Process | The 'What': Defines the entire end-to-end workflow for proposing, approving, implementing, and reviewing changes to production systems to minimise disruption and security risks. |
| Procedure | Emergency Change Procedure | The 'How': Outlines the distinct steps for handling a critical, out-of-band change needed to fix an urgent issue. It covers who authorises it and what documentation is required post-incident. |
| Work Instruction | How to Apply an Emergency Patch to a Firewall | The 'How-To': A step-by-step guide with specific commands, screenshots, and verification checks to ensure a firewall patch is applied correctly without causing more problems. |
As you can see, this top-down approach ensures every single action, no matter how small, is directly aligned with your overarching security strategy. It’s a simple but incredibly effective way to build a robust and auditable ISMS.
A Practical Plan to Align Your Documentation for ISO 27001
Knowing the difference between a process and a procedure is one thing. Turning that knowledge into documentation that will pass an ISO 27001 audit is another challenge entirely. This is where theory meets reality, and it's often where businesses stumble on their path to certification.
Let's walk through a clear, structured plan to get this right. By following these steps, you’ll build an Information Security Management System (ISMS) that isn't just a pile of documents, but a coherent framework an auditor can easily understand and appreciate.
Identify and Map Core Security Processes
Before you even think about writing a procedure, you need to zoom out. Start by identifying the big-picture workflows that are fundamental to keeping your information secure.
Think high-level. Your first job is to map the end-to-end journey of each critical security function.
- What to map: Don't get lost in the weeds. Focus on major pillars like Risk Management, Access Control, Incident Response, and Change Management. These are your non-negotiables.
- How to do it: Grab a whiteboard or use a simple flowchart tool. Visualise each process, noting the inputs, key decision points, and the final outputs or outcomes. This high-level map becomes the skeleton of your ISMS, giving every procedure a logical place to hang.
This initial mapping is your strategic blueprint. It ensures every detailed document you create later has a clear purpose and connects back to the bigger picture.
Conduct a Gap Analysis for Necessary Procedures
With your processes mapped out, it's time to figure out where you actually need to write detailed procedures. A gap analysis is your best friend here. It helps you zero in on tasks where inconsistency could introduce serious risk.
This is all about bridging the strategic 'what' with the operational 'how'. A great way to start is by looking at our ISO 27001 gap assessment template. For each step in your process flowcharts, ask yourself a simple question: "If two different team members had to do this, would they do it the exact same way?" If the answer is no, you’ve just found a gap that needs a procedure.
Prioritise Documentation Based on Risk
Here’s a secret: you don't need to document every single task from day one. That's a recipe for burnout. Instead, let risk be your guide. Focus your energy where it will make the most difference.
Start with procedures for activities that could cause a major security incident if done wrong. Think about things like configuring firewall rules, revoking access for a departing employee, or restoring critical data from backups. An auditor will see this risk-based approach as a sign of a mature, well-thought-out ISMS.
Use Templates and Implement a Review Workflow
Consistency is king in a well-managed security system. Using a standard template for all your procedures makes a world of difference. It ensures they all have a familiar structure, making them far easier for your team to use and for auditors to follow.
Finally, set up a proper review and approval cycle. Procedures should be reviewed by the people who will actually use them and formally signed off by management. This collaborative loop ensures your documentation is both practical for the frontline and aligned with your high-level security processes.
This structured approach is proven to work. The Queensland Government, for instance, saw a massive 68% growth in ISMS adoption by 2024, a success they directly credit to their formalised governance program. You can read more about how this framework can be applied to Australian ISMS governance on iso-27001.com.au.
Got Questions? Let's Talk Real-World Scenarios
Alright, theory is one thing, but how does the whole process vs. procedure distinction play out on the ground during an ISO 27001 implementation? Let's tackle a few common questions I hear all the time.
Do All Our Processes Need a Written Procedure for ISO 27001?
Not necessarily, but the decision comes down to one crucial factor: risk.
Think about a high-level process like 'Management Review'. You can document the process itself—what it aims to achieve, who's involved, and what inputs it needs—without a rigid, step-by-step procedure. Its execution can be more fluid, as long as the core objectives are met.
But when it comes to a critical security process like 'Data Backup and Recovery', an auditor will absolutely expect to see a detailed procedure. If messing up the steps could lead to a data breach or catastrophic loss, a documented procedure is non-negotiable. It’s the only way to prove consistency and provide a clear audit trail.
How Often Should We Be Reviewing This Stuff?
For ISO 27001, a good rule of thumb is to review all your procedures at least once a year. But don’t just wait for the calendar reminder. A review should be triggered immediately if there’s a major change in your business, your tech stack, or the threat environment.
Your processes, on the other hand, are more strategic. They should be a standing item on the agenda for your formal management reviews. This ensures they’re still aligned with your business goals and are doing their job to manage information security risks effectively.
What’s the Biggest Mistake People Make With Their Documentation?
Hands down, the most common pitfall is creating procedures that are either so generic they're useless, or so ridiculously detailed that no one in their right mind would ever follow them.
The sweet spot for documentation is that perfect balance: it needs to be specific enough to get the right result every single time, but practical enough that your team can actually use it without it feeling like a burden.
Another classic blunder is writing documentation in an ivory tower. If you don't involve the people who actually do the work in creating the procedure, you'll end up with a document that’s completely out of touch with reality. It becomes shelf-ware, useless for training and a red flag for auditors.
Trying to get your ISO 27001 documentation just right for an audit can feel like a massive headache, especially when you’re trying to connect high-level processes to detailed procedures. With over 20 years of experience and a 100% success rate in consulting, Anitech helps Australian businesses navigate this exact challenge. We take the complexity out of the entire journey, from documentation to the final audit, so you can get certified and get back to growing your business. Chat with our experts today at https://iso-27001.com.au.
Recent Comments